In an April 2025 report, SentinelOne documented more than 1,000 job applications linked to North Korean IT-worker operations, using roughly 360 fake personas. The cumulative total covered applications for its own roles. A cybersecurity company was being repeatedly targeted through the process it used to recruit new colleagues.
The AI connection is real. The FBI’s January 2025 advisory reported North Korean IT workers using artificial intelligence and face-swapping during video interviews to conceal their identities. It also warned of workers stealing proprietary data and code and demanding payment. A convincing applicant can create both a payroll problem and an insider-security problem.
This is the North Korean deepfake job scam: an established employment-fraud operation gaining another means of deception. Fake résumés, stolen identities, misleading profiles and concealed locations can support the same objective. A live deepfake is one technique within that wider scheme; it is not established as the method used in every fraudulent hire.
The scam works because it exploits a perfect storm: the global shift to remote work, the pressure to fill IT roles quickly, and the increasing sophistication of synthetic media tools. In some cases, workers have also stolen company data and code or demanded payment, as the FBI warned. The risks therefore extend beyond salaries and into the access an employer entrusts to a new colleague.
This blog provides a deep dive into the North Korea IT worker scam, examining the mechanics of the fraud, the scale of its impact, and what companies need to do now to protect themselves. Whether you’re an HR lead at a fast-scaling SaaS firm or a federal policymaker shaping cybersecurity strategy, understanding the reality of this remote worker infiltration is no longer optional.
We cover stories like this in our newsletter. Subscribe here to stay ahead of emerging threats.
Key Takeaways
- North Korean IT-worker fraud uses stolen or fabricated identities; the FBI has also observed AI and face-swapping during video interviews.
- A polished résumé, successful video call or completed background check does not establish that the applicant is the person whose identity was checked.
- A December 2024 indictment alleged at least $88 million in revenue over roughly six years in one employment-and-extortion scheme. That is not a total for all North Korean hiring fraud or all deepfake use.
- U.S.-based laptop farms can conceal workers operating elsewhere. The location of company equipment and the location of the person controlling it are different questions.
- Identity inconsistencies, manipulated video, evasive verification, shipping changes, payment mismatches, concealed access and unauthorized data activity are seven reasons to investigate. None alone proves North Korean affiliation.
- Employers need coordinated HR and security checks, restricted onboarding access, monitoring and a clear escalation route when several indicators point to fraud.
How the Deepfake Scam Works
False Résumés and Online Profiles
North Korean operatives begin their scam not with code, but with credibility. The applicant needs a work history, references and an identity that appear consistent enough to survive recruitment. A résumé may describe genuine technical ability while misrepresenting the person offering it. A skilled developer can still be using somebody else’s identity.
The October 2023 joint guidance on North Korean IT workers describes false identities, misleading online profiles and the use of intermediaries to obtain work. For recruiters, the important question is whether the résumé, profile, identification and person on the call belong together. Several convincing documents supplied by the same applicant do not amount to several independent confirmations.
AI can strengthen the appearance of a false persona, but polished writing is not evidence of state affiliation. Nor does a professional-looking LinkedIn page establish that its employers or references are genuine. The goal of verification is to test the underlying claims, rather than judge whether an application looks sufficiently polished to be trustworthy.
The goal is to build a false but credible digital persona: one that looks like your next DevOps hire but is actually part of a sanctioned state operation.
Deepfake Video Interviews

The interview process, long considered a final filter for fraud, is also a weak point. Real-time face-swapping can change the appearance of the person answering questions. It therefore matters that the FBI’s warning describes observed use during North Korean hiring fraud, rather than only a possible future technique.
For deepfake job applicants using face-swapping, fake tech job interviews provide an opportunity to answer questions while presenting someone else’s appearance. A technically convincing answer still leaves the identity claim to be checked.
Palo Alto Networks’ Unit 42 demonstrated the low barrier to creating an interview deepfake: one researcher produced a passable synthetic identity in 70 minutes using readily available tools. This was the researcher’s demonstration, not a measured North Korean setup time or proof that a fake could reliably pass a full interview.
The demonstration also showed limitations, including tracking, lighting and lip-sync inconsistencies. A convincing picture is not necessarily flawless, but the absence of an obvious glitch is not proof of authenticity. Video gives an interviewer more information; it cannot replace checking who the applicant is and whether that person is entitled to do the work.
Location Spoofing and Laptop Farms
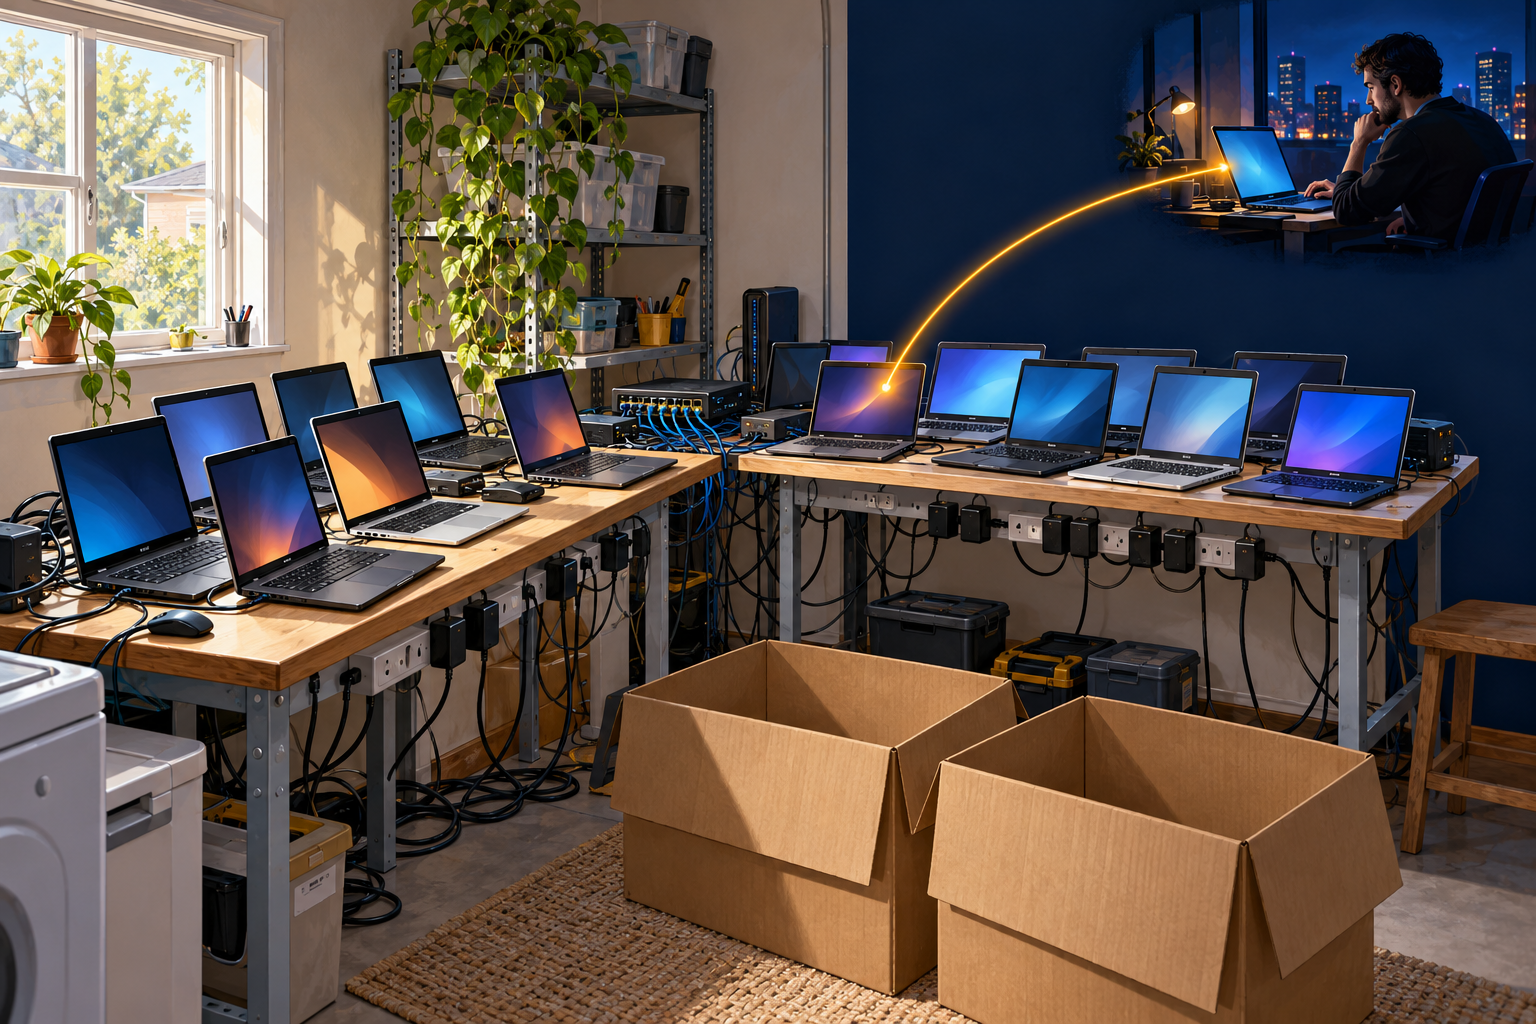
Getting hired is only half the mission. A worker concealing their location also needs the employer’s equipment and connections to appear consistent with the job. A laptop farm can place company-issued devices with a facilitator in the United States while the worker controls them remotely from elsewhere.
The Justice Department’s May 2024 enforcement announcement described alleged schemes that defrauded more than 300 U.S. companies. U.S.-based intermediaries and company laptops helped give foreign workers the appearance of operating domestically. The equipment did not have to be shipped overseas for that deception to work.
This infrastructure explains why a domestic IP address or shipping destination cannot settle the location question. It also explains why hiring checks and device controls must connect: an approved address is less useful if the organization does not examine a later request to reroute the laptop or permit unexplained remote access.
Who’s Behind the Fraud: North Korea’s IT Operative Networks
State-Run Employment Fraud Schemes
This is not the work of isolated cybercriminals. The May 2022 State, Treasury and FBI advisory describes thousands of North Korean IT workers operating inside the country and abroad to generate revenue for the government. It identifies dispatching entities associated with the Munitions Industry Department, including its 313 General Bureau, and links the revenue to prohibited weapons programs.
Front companies and facilitators add distance between the employer and the state receiving the proceeds. That distance is part of the problem for due diligence: the person, intermediary and payment recipient visible to an employer may conceal a different working relationship underneath.
The workers may perform real technical work. The deception concerns identity, location, affiliation and payment, not necessarily whether the person can write code. Treating the problem solely as a test of technical competence misses the state-directed revenue operation behind the application.
Estimated Scale and Profit
The scope is substantial. In December 2024, DOJ announced charges against 14 North Korean nationals in an alleged employment-and-extortion conspiracy that generated at least $88 million over approximately six years. The defendants worked for Yanbian Silverstar in China and Volasys Silverstar in Russia, placing the employment operation across several jurisdictions.
The $88 million figure describes one charged conspiracy over a multi-year period. It illustrates how sustained employment fraud and extortion can accumulate substantial revenue, even when an employer sees only an individual contractor and ordinary payments for work.
The 2022 advisory estimated that some individual IT workers could earn more than $300,000 annually and that IT-worker teams could collectively earn more than $3 million a year. Its separate hundreds-of-millions annual revenue figure referred to wages withheld from overseas North Korean workers more broadly, rather than an IT-only total. These are attributed estimates, not a global payroll census or a typical salary for one job. They show why the regime has a strong incentive to keep the operation running.
Links to Weapons Programs
This is not just about fraud. The official warning connects the workers’ revenue to North Korea’s weapons development, including nuclear and ballistic missile programs. Employers can therefore be funding a sanctioned state’s priorities while believing they are paying an ordinary remote contractor.
The national-security concern is the revenue stream and the system designed to sustain it. Salary payments, state control and concealed affiliations create a policy problem as well as a business loss. An employer’s assessment therefore needs to consider the working relationship behind the apparent individual hire.
For North Korea, this is a business model, not a side hustle. The same arrangement that earns money can also put a deceptive worker in a position of trust inside an employer. Revenue generation and insider risk are connected even when a particular case involves no successful malware attack.
Infiltration of U.S. Companies: The Scope
Sectors at Risk
The documented examples include cybersecurity companies and other technology employers. The May 2024 allegations reached hundreds of U.S. businesses, showing that the problem is not confined to one vendor or one recruitment platform. That does not establish that every affected employer suffered a data breach or used the same hiring process.
Why do these roles matter? Organizations may entrust developers and administrators with source code, customer information or systems on which other businesses depend. A successful fraudulent hire can therefore create an exposure greater than the value of the salary. The extent depends on the permissions actually granted, not the job title alone.
A remote-first company should examine where identity checking ends and access provisioning begins. Technical screening can establish that someone can do the work while leaving unanswered who they are, who controls their accounts and where the payments ultimately go. Those unanswered questions are the opening the scheme exploits.
Case Numbers and Employer Impact
The May 2024 DOJ announcement alleged fraud against more than 300 U.S. companies. The December indictment alleged at least $88 million in a separate, multi-year conspiracy. SentinelOne’s April report counted applications for its own roles. Together, these accounts show the problem at different stages: attempted recruitment, fraudulent employment and revenue generation.
Each fraudulent hire can carry financial, legal and reputational consequences. Employers may pay salaries, provision accounts and ship equipment before discovering that the identity or working arrangement was false. Discovery then raises practical questions about what the worker accessed, what information was copied and which controls need to change.
The employer must distinguish what happened from what could have happened. A fraudulent application stopped before hiring, an employee with limited onboarding access and an insider who copies a repository present different incidents. All warrant attention, but the response and assessment of harm should reflect the evidence in the particular case.
Hiring Pipelines Under Pressure
Part of the reason these scams work so well is volume. Companies can be overwhelmed with applications, especially for remote IT roles. Hiring managers are under pressure to fill roles quickly and efficiently, often relying on automation, third-party recruiters, or minimal human screening to manage the load.
A résumé, interview and background check can each look acceptable while the identity linking them is false. If a recruiter assumes that security has verified the person, while security assumes that recruiting already did so, an important responsibility can fall between the teams.
This is a process problem, not simply a failure to notice a strange face on a screen. Employers need to know who resolves conflicting information and who can pause onboarding before more access is granted. Passing one stage should not automatically close questions raised at another.
What Happens After Hiring: Internal Threats and Malware
Immediate Post-Onboarding Risks
KnowBe4’s July 2024 account of a fraudulent hire shows how quickly attempted abuse can follow delivery of a company laptop. The worker tried to load an infostealer, security tools raised an alert and the team isolated the device 25 minutes after the first alert. The incident was an attempted malware installation, not a successful takeover of the corporate network.
Access levels matter from the first day. Developer or administrator roles may require substantial privileges eventually, but those privileges need not accompany an unverified new hire through initial training. Restricted onboarding can limit the damage when recruitment controls fail.
The North Korean deepfake job scam is not simply about harvesting salaries. It uses the guise of employment to obtain trust and authorized access. Firewalls alone cannot answer the identity question behind a newly created account; hiring and access decisions are part of the security boundary too.
Long-Term Insider Threats
If not detected quickly, these operatives can become persistent insider threats. Unlike external attackers who rely on phishing or brute force, North Korean operatives hired through false identities appear to be trusted team members on paper. They attend virtual standups, receive onboarding materials, and participate in internal Slack or Teams channels. This remote worker infiltration turns an employer’s ordinary collaboration into part of the access that needs protecting.
The FBI’s January warning describes workers copying proprietary code and using personal accounts or cloud storage to retain company material. It also identifies potential harvesting of credentials and session cookies as a further risk. These concerns justify examining access and data movement rather than focusing only on the initial interview.
An employer investigating a case should establish the worker’s actual permissions, transfers and changes. Those records help determine what information was exposed and what access needs to be contained. The ability to copy company material can create lasting harm after the account itself has been disabled.
Data Theft and Extortion
The FBI reported workers threatening to release stolen proprietary data and code unless employers paid. Some victims’ code was publicly released. A company can face that demand even when its systems have not been encrypted: the leverage comes from possession of confidential information and the threat of exposure.
Ransomware and data extortion are different mechanisms. Ransomware can deny access to files through encryption; data extortion threatens disclosure of material already stolen. In the hiring cases described by the FBI, the theft and demand for payment could continue to affect the employer after the worker was discovered.
Email filtering addresses a different entry point from an authorized user misusing access. Monitoring inside the environment remains important. The practical response is to connect endpoint alerts, account activity, repository access and data-transfer evidence with the identity concern that triggered the investigation.
Financial and National Security Risks
Funding the Regime’s Priorities
At its core, the North Korean deepfake job scam is more than a financial crime against an individual employer. The official advisories describe a revenue-generating operation for a sanctioned government. A worker can appear to be completing useful assignments while concealing the affiliation that makes the employment and payment arrangement dangerous.
This is why the weapons-funding argument matters. Employers cannot assess the harm only by asking whether a contractor delivered working software. The identity and payment deception can support the regime’s revenue even in cases where no customer information is lost.
Undermining Sanctions
The success of these schemes undermines the purpose of sanctions. False identities and intermediaries can conceal a prohibited relationship from employers and financial institutions. A transaction that looks ordinary at the payroll desk may be part of a larger effort to evade restrictions.
The 2022 advisory warns of sanctions exposure for businesses involved in prohibited transactions. Employers should involve their compliance and legal teams when credible evidence of North Korean affiliation emerges. The answer depends on the applicable restrictions and the facts; nationality, residence and a particular transaction must not be collapsed into a casual legal conclusion.
In effect, a company deceived by the scheme can become part of a sanctions-circumvention network. HR, security, finance and compliance therefore have overlapping responsibilities. A change in payment instructions should not be assessed in isolation from unresolved identity or location questions.
Exposure Beyond the Employer
A technology employer may hold information or maintain services used by other organizations. If a deceptive worker obtains sensitive access, the potential consequences can extend beyond one payroll or one account. That is a risk to assess, rather than proof that every fraudulent hire already reached critical infrastructure.
The same distinction applies to administrative privileges. A job in cloud operations or software development can be sensitive, but the actual access depends on the employer’s controls. It is important to identify the accounts, environments and data involved before describing the scope of a compromise.
Our article on AI-powered cyberattacks against critical infrastructure examines the wider consequences of attacks on essential services. Here, the immediate connection is the trust placed in people who build, support or administer technology. Identity assurance and restricted access help protect that trust.
Seven Red Flags in a Deepfake Job Application
The aim is to identify inconsistencies that deserve investigation, not to turn an accent, nervous response or video problem into a nationality test. Apply a consistent process to applicants, give people an opportunity to explain discrepancies and corroborate concerns through independent information.
1. Identity and Employment Records Do Not Agree
Look for differences between the claimed identity, résumé, references and identification presented during hiring. Check important claims through independently obtained employer or institution contacts. An email reference supplied by the applicant can be useful, but it should not automatically settle a discrepancy.
The question is whether the records refer to the person being hired. A legitimate identity can pass a background check even when it is being used by someone else. Likewise, a plausible online profile does not resolve conflicting names or employment dates.
2. Video and Audio Behave Inconsistently
The FBI’s June 2022 warning about remote-interview fraud describes reported mismatches between speech and the person visible on screen. That warning concerns remote-work fraud generally; it does not attribute every such event to North Korea. Unit 42’s later demonstration also showed facial tracking and lighting defects.
Treat unusual lip-syncing, face distortion or repeated unexplained changes as reasons for additional checks. Connection problems and ordinary video processing can also produce artifacts. A clean video is not identity verification, and an awkward one is not proof of a deepfake.
3. Requests Avoid or Disrupt Verification
Repeated attempts to bypass agreed identity checks or unexplained changes in who attends an interview deserve attention. A team should know how to pause the process and resolve those issues before hiring. The concern is an unresolved pattern, rather than the mere fact that an applicant asks for an accommodation.
Questions about claimed employment, education or location can help test consistency. They should relate to facts that can be checked, rather than favorite holidays, food or cultural assumptions. An accent or unfamiliarity with local trivia does not demonstrate a false identity or North Korean affiliation.
4. Equipment Must Be Sent Somewhere Unexpected
A request to reroute a company laptop away from the verified destination can matter, especially when the explanation conflicts with earlier records. Confirm the proposed recipient, address and reason before shipping. A domestic address alone does not establish that the employee will personally use the equipment there.
Laptop farms make this distinction concrete: the employer’s device can remain in the United States while a different person controls it remotely. The relevant question is who receives and controls the device, not simply whether a parcel tracking record shows domestic delivery.
5. Payment Details Do Not Match the Working Arrangement
Third-party recipients, inconsistent account names or unexplained changes in payment instructions should be checked against the verified arrangement. The concern is the mismatch and its explanation, rather than a rule that every international payment or payment service indicates fraud.
Finance needs a way to raise that concern with HR and security. If an identity discrepancy is already open, treating a new payment destination as an unrelated administrative request can miss the connection. The same verification standard should apply when instructions change after onboarding.
6. Connections Conceal Who Is Operating the Device
Investigate unauthorized remote-access software, inconsistent account activity or connections that do not fit the approved work arrangement. The January FBI advisory recommends monitoring for anomalous remote connections and multiple logins from different locations. These are technical leads, not a standalone attribution method.
An IP address can identify a connection point without locating the person controlling it. VPNs and remote desktop tools also have legitimate uses. Compare activity with the role, permitted tools and other evidence before deciding whether it indicates concealed control.
7. Access or Data Movement Exceeds the Job
An attempted unauthorized installation, unexpected repository copying or transfers to personal storage can indicate misuse after hiring. Investigate promptly, preserve the relevant records and limit access according to the incident-response process. Do not wait for certainty about state affiliation before addressing a concrete security event.
A technically capable worker can still misuse access. Performance reviews and completed assignments do not make unrelated data transfers acceptable. This warning sign connects the hiring concern to the activity that may determine the actual damage.
For the separate problem of manipulated audio and cloned voices, see our article on AI voice-cloning scams. No single sensory clue substitutes for corroborating the identity and actions involved.
Real Cases and Employer Responses
CrowdStrike and SentinelOne Investigations
CrowdStrike’s February 2025 Global Threat Report announcement reported 304 FAMOUS CHOLLIMA incidents uncovered during 2024, about 40% involving insider activity. This measures incidents in the company’s reporting; it does not provide a separate count of successful hires or deepfake interviews.
SentinelOne’s April report described roughly 360 false personas and more than 1,000 applications for its roles. Its intelligence and recruiting teams worked together to identify and engage suspicious applicants. The practical lesson is that recruiting information can become security information when teams have a process for comparing it.
Neither report supplies a universal hiring-fraud rate. They do show why companies should examine the links between an applicant’s identity, previous personas and the access eventually granted, rather than assume a technical interview resolves the whole problem.
KnowBe4’s Fake Hire Incident
KnowBe4’s contemporary company white paper identifies the persona as “Kyle.” The applicant passed four video interviews and background checks using a stolen U.S. identity and an AI-altered profile photograph. Those facts support the hiring-deception example; they do not establish that the interviews themselves used live deepfake video.
The company’s July 2024 clarification says malware execution was blocked and the worker never gained access to customer data, private networks, cloud infrastructure or code. Restricted onboarding permissions and endpoint controls limited the consequences of a recruitment failure. The laptop was contained within 25 minutes of the first alert, and the company said no breach occurred.
The case highlights the need for monitoring after onboarding. It also shows that a failed hiring check need not become unrestricted internal access. Accurate reporting should preserve both parts of that lesson: the worker got hired, and additional controls stopped the attempted abuse.
Cooperation Between Teams and Companies
In its May 2025 account of identifying a suspected North Korean applicant, Kraken described combining industry-shared indicators, examination of the claimed identity and questions during interviews. KnowBe4 shared incident information with Mandiant and the FBI. SentinelOne connected threat intelligence with recruitment.
These examples connect recruitment, threat intelligence and incident response. For an employer, the practical question is whether relevant information reaches someone able to act on it before another account, device or payment is approved. Sharing a concern is useful only if the receiving team knows what decision it needs to make.
Action Steps for Employers to Protect Themselves
The North Korean deepfake job scam exposes weaknesses in how companies connect identity checks with remote access. Organizations need a layered approach: verify important claims, resolve discrepancies, restrict initial access and keep monitoring after the employee starts. A convincing candidate should not cause those responsibilities to disappear.
Strengthen Identity Verification
Check identity before, during and after onboarding, particularly when names, addresses or payment details change. Verify employment and references through independently obtained contacts. Where practical, complete important checks in person or through an appropriate trusted process rather than relying entirely on applicant-supplied material.
Use video as one part of that process, with reasonable accommodations. Liveness checks may help assess a presented image, while multifactor authentication protects account access. Neither alone establishes that a person is who they claim to be or that the employment arrangement is legitimate. The same distinction applies to a valid identity document used by an impostor.
Combine Screening With Security Review
Give recruiters a clear route for referring unresolved inconsistencies to security and compliance. Record the concern and the evidence needed to resolve it. Consistent decisions are more useful than improvised cultural tests or an unsupported promise that a tool will detect every fake.
Review device and account activity against the approved role. Restrict new-hire permissions, examine unexpected remote access and investigate unauthorized installations or data transfers. Our discussion of AI security tools and their uses provides broader context; a product purchase does not replace this coordination.
Control Device Shipping and Access
Verify equipment destinations and recipients, and investigate changes before shipping. A setup call can provide context, but it cannot conclusively establish physical location. Compare the shipping record with identity information and the approved working arrangement.
Limit initial permissions to what onboarding requires. The KnowBe4 example shows why that boundary matters even after a seemingly thorough interview process. If concerns emerge, preserve account and device evidence and use the incident-response process to determine what was accessed or copied. Keep compliance and security decisions connected.
Share Indicators and Report Suspected Cases
Employers should not go it alone. Appropriate information-sharing networks and industry contacts can help teams recognize reused identities, infrastructure or contact details. Share useful evidence through established channels, with attention to privacy and the sensitivity of employee and company information.
Benefits of ISAC participation include:
- Access to threat indicators such as IP ranges, file hashes and behaviors.
- Early warnings on scam variants or tactics.
- Coordination with law enforcement when infiltration is suspected.
The FBI recommends reporting suspected North Korean IT-worker activity to its Internet Crime Complaint Center and examining the suspected worker’s network and device activity. An incident report should distinguish observations from assumptions: what was inconsistent, what access existed and what activity occurred. That evidence gives other teams something concrete to investigate.
Conclusion and Future Outlook
The North Korean deepfake job scam exposes the convergence of AI-assisted deception, remote employment and a state-directed revenue operation. AI and face-swapping make an existing identity problem harder to assess through a screen. They do not need to account for every fraudulent hire to be a serious part of the threat.
What makes the scheme dangerous is its exploitation of trust and ordinary business processes. A worker can earn revenue for the regime, obtain sensitive access or steal information while appearing to occupy a legitimate role. The national-security concern extends beyond wages, while the consequences for each employer depend on what actually happened.
The documented cases also show that defenses can work. Fraudulent applications can be identified, onboarding privileges can be limited and attempted malware can be blocked. Employers need to join those controls together rather than rely on a polished résumé, a completed interview or a background-check result in isolation.
For HR, security and policymakers, the priority is the same: protect the link between a real person, a verified working arrangement and the access entrusted to that person. Failing to examine that link can turn an ordinary recruitment process into a route for sanctions evasion and insider harm.
The North Korea IT worker scam is a glimpse into the next generation of cyberwarfare. Jobs become weapons, interviews become infiltration points, and salary payments become a route for evading sanctions. Organizations that fail to update their defenses are not just risking a bad hire. They are risking a breach with global implications.
FAQ
How do deepfake interviews work in real time?
Face-swapping can alter the appearance of the person answering questions during a video call. The FBI’s January 2025 warning reported observed use in North Korean IT-worker fraud. The person can still be answering the interviewer’s questions themselves; an altered face does not mean that the entire conversation is generated by AI.
Which employers should be concerned?
The examples include cybersecurity and other technology companies, and DOJ’s May 2024 allegations reached more than 300 U.S. companies. Remote roles involving sensitive systems deserve particular attention to identity and permissions. Those figures do not establish which industry has the highest fraud rate or that every affected employer suffered a data breach.
Can hiring a North Korean IT worker create sanctions exposure?
Yes. The 2022 joint advisory warns that employers can face sanctions exposure for prohibited dealings. The relevant identities, affiliations, transactions and restrictions need careful review by compliance or legal staff. A suspicious interview alone does not establish nationality or determine a company’s liability.
How can HR staff recognize the warning signs?
Look for corroborated inconsistencies in identity, claimed experience, verification, shipping, payments and access. Video artifacts can prompt further checks, but accents, nervousness or unfamiliarity with local trivia do not prove deception. Share unresolved concerns with security and compliance before granting additional access.
What should an employer do if it suspects a fraudulent hire?
Follow the incident-response process, preserve relevant records and assess the person’s accounts, device access and data activity. The FBI recommends reporting suspected North Korean IT-worker activity to IC3. Keep observations distinct from assumptions and coordinate the security response with HR, finance and legal staff.