In April 2025, cybersecurity firm iVerify published a report that should concern anyone who uses a mobile phone. It identified 60 mobile operators in 35 countries using China- or Hong Kong-based interconnect providers. Its customer tables drew on November 2024 operator documentation. The finding raises serious mobile data privacy risks: an intermediary can become part of a carrier relationship without the subscriber choosing it or understanding the exposure.
The concern is the role of providers subject to Chinese state influence and intelligence-cooperation requirements. It is not a finding that every listed subscriber’s communications were collected, or that every connection physically crossed mainland China. Those distinctions matter, but they do not make the underlying surveillance risk harmless. A person can choose a familiar local carrier while still depending on international arrangements that are difficult to see.
Unlike a phishing attack, this exposure need not arrive as a suspicious message. There may be no warning on the handset that identifies a trusted intermediary or explains the jurisdiction governing it. The problem lies in the infrastructure and agreements behind ordinary service, where individual users have little visibility or control.
This investigation breaks down the threat: what iVerify established, how international data routing and signaling relationships work, the surveillance implications, and what individual protections can realistically accomplish. The central question is accountability. Who can handle the information needed to connect a phone, and what protects the subscriber when that access crosses institutional and national boundaries?
To get weekly breakdowns like this on AI, cybersecurity, and digital privacy, subscribe to our newsletter.
Key Takeaways
- iVerify identified 60 operators in 35 countries using the interconnect providers examined in its April 2025 report; the evidence came from operator documentation, not live traces of every user’s traffic.
- Chinese ownership or control of an intermediary creates an access and governance concern without proving a particular physical route through mainland China.
- SS7 and Diameter have different security designs. Protected transport between network peers does not remove the need to trust intermediaries handling sensitive signaling information.
- End-to-end encrypted app content and carrier information are different exposure surfaces. Protecting one does not automatically hide the other.
- Chinese intelligence-cooperation powers make provider control consequential, while actual collection and the legality of a particular operation require separate evidence.
- VPNs, encrypted conversations, non-SMS authentication and device-security checks have useful but different roles; none gives an ordinary user full control over carrier interconnect paths.
- Carrier and government action matters because individual precautions cannot substitute for secure interconnection, meaningful oversight and clearer responsibility for subscriber data.
What iVerify Discovered About Mobile Data Routing
The iVerify team examined operational information shared between mobile networks through the GSMA’s IR.21 RAEX documentation system. These records describe interconnection arrangements and technical details needed for networks to work together. The report used them to identify customers of the providers it examined across Asia, the Middle East, Oceania and other regions. That is evidence of consequential infrastructure dependency, rather than a reconstruction of every call, message or location update.
The distinction affects how the findings should be read. A documented relationship can identify where trust is being placed and which organizations may have access. It does not establish that every communication used that intermediary at a particular moment. Nor does an operator’s inclusion prove that its customers were all victims of a specific surveillance operation. The report’s warning concerns the opportunity and leverage that such access can create.
The Role of Major Chinese Telecom Providers
China Mobile International, China Telecom Global and China Unicom Global are among the providers discussed in this ecosystem. These entities offer services that connect national carriers and support international communications. A local carrier does not need to own infrastructure in every destination; it can rely on a partner with wider reach. That arrangement makes service possible, while extending the chain of organizations a subscriber must trust.
Commercial reach, reliability and cost can all influence those relationships. The report does not establish what every carrier knew or why each selected a particular provider. The accountability concern survives without inventing those motives: an operator offering service to its customers should be able to explain how it evaluates the security and legal exposure of the partners on which it relies.
SS7 and Diameter: Security Depends on More Than a Name
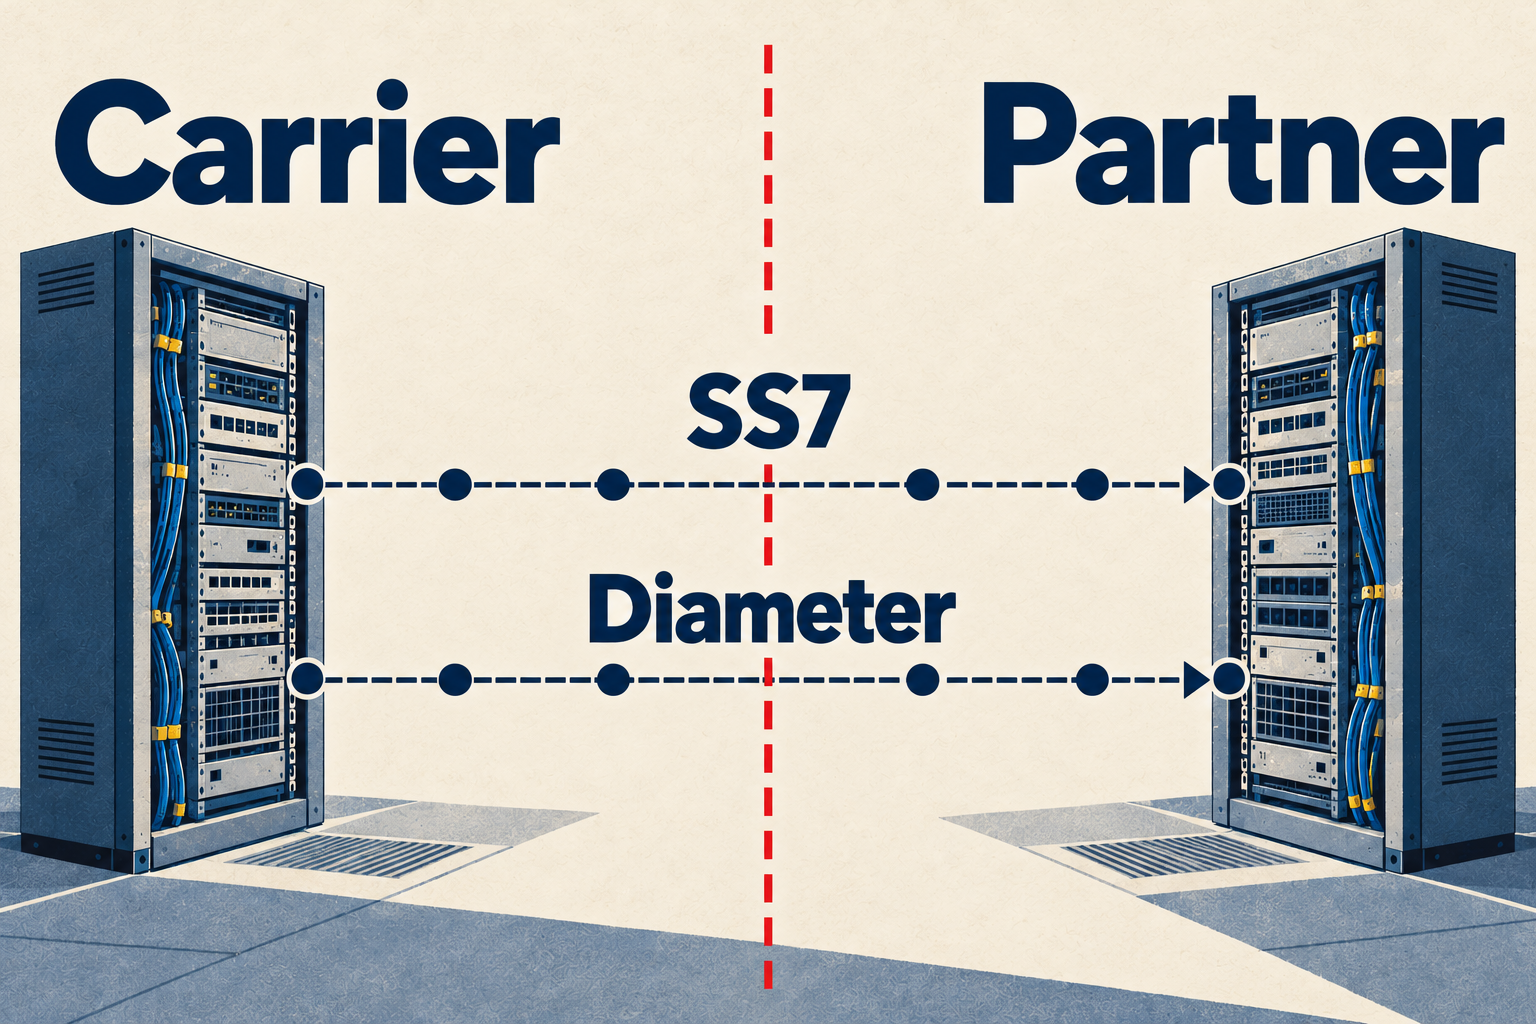
Signaling is the network’s control information: it helps carriers authenticate subscribers, establish service, route communications and manage mobility. It is distinct from the ordinary internet content a person views in an app or browser. SS7 and Diameter are part of that carrier infrastructure, and weaknesses in its trust relationships can have consequences beyond a single application.
It would be inaccurate to say that Diameter was designed without encryption or authentication. The Diameter Base Protocol specification defines protected transport and peer-authentication requirements. The important limit is that securing a connection between participating networks does not itself make sensitive information inaccessible to a trusted intermediary. Its security considerations address that trust problem; they do not establish that every real-world deployment is secure.
SS7’s legacy trust model and insecure or inadequately controlled interconnections also create opportunities for abuse. In the 2017 German banking example discussed in the report, criminals combined stolen account credentials with intercepted SMS confirmation codes. That is a concrete reason to avoid relying on SMS alone for sensitive authentication. It is not evidence that the Chinese providers listed in the 2025 report carried out those thefts, or that metadata by itself opens every account.
The technical issue is therefore more precise than ‘old protocols have no security.’ It includes which peers are trusted, what information they handle, how requests are restricted, and how effectively operators detect abuse. A protected link can still connect organizations whose interests or legal obligations differ from those of the subscriber. Standards and technical controls matter, but the organizational relationship matters too.
How Your Data Ends Up in Foreign Networks
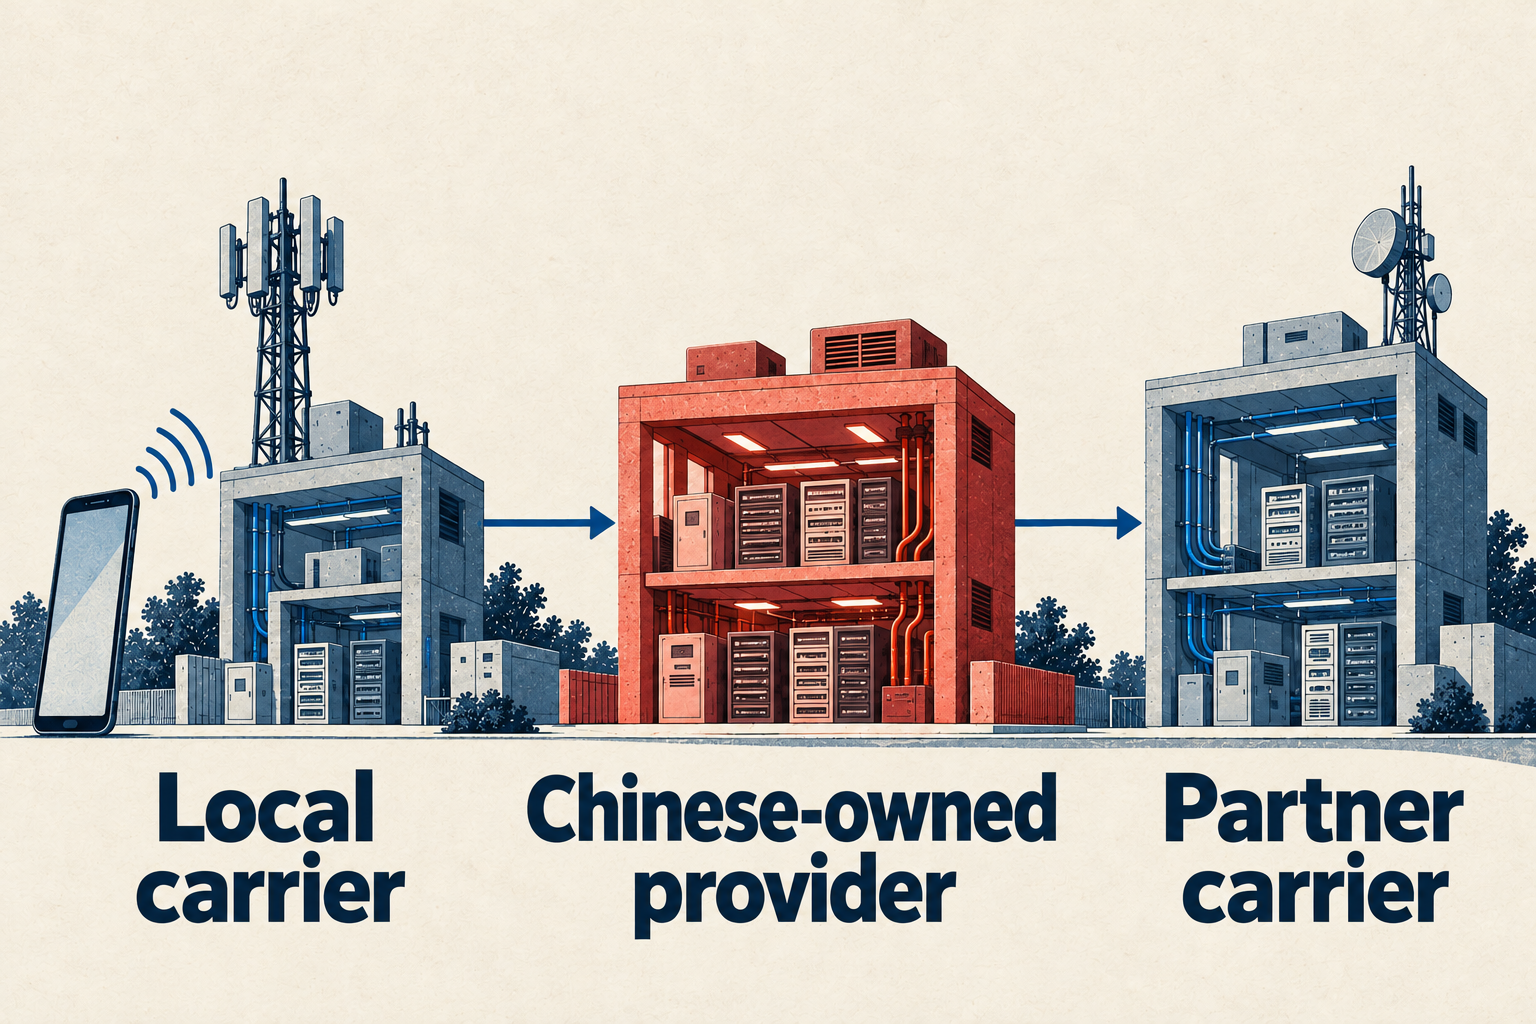
Many users assume their mobile data stays within their home country’s networks. The reality is more complex. Global telecommunications operates through a web of interconnect agreements. Carriers use other providers to reach partner networks and destinations, so the company whose name appears on a phone bill may not be the only organization involved in delivering service.
The Role of Roaming and Interconnect Agreements
Roaming makes this dependence especially apparent. A traveler needs a visited network and supporting arrangements with their home operator. Interconnection also supports communications between different carriers. The relevant question is which information a partner receives and what safeguards apply, rather than whether the subscriber has personally signed up with a Chinese company.
The report identifies operators in countries including Japan, Saudi Arabia and New Zealand, but its documentation should not be converted into proof that purely domestic messages in each country followed a traced path through mainland China. Provider ownership, the jurisdiction governing a provider and the physical location of a particular connection are related questions, not interchangeable facts.
That qualification does not eliminate cross-border data exposure. It identifies the practical gap: users generally cannot inspect the full chain behind their service, decide which intermediary is acceptable, or move a signaling exchange onto a preferred route. A local brand and a local phone number do not answer all the questions about who participates in the wider network relationship.
Telecom Infrastructure Is Global and Opaque
Most users assume their mobile data takes a direct route from their phone to the nearest data center. In reality, mobile signaling traffic can cross borders and pass through networks governed by different privacy laws. That general possibility is not a traced finding about every connection. Different parts of a communication can involve different systems and protections. App traffic, network registration, SMS delivery and other signaling functions should not be treated as one identical stream.
Opacity makes accountability difficult. A carrier’s service can work normally while customers remain unaware of the organizations behind it. The concern is not proof that every operator is ignorant or deliberately hiding a route. It is that a user has little basis for judging these dependencies without meaningful information from the companies responsible for them.
The Privacy and Surveillance Risks Explained
Understanding the technical vulnerabilities in global mobile data routing is important, but the real concern lies in what those vulnerabilities enable: surveillance, interception and manipulation when controls fail or a participating organization abuses its position. The combination of technical access and authoritarian state control creates serious privacy risks with geopolitical consequences. The report warrants scrutiny without establishing that every possible form of abuse has occurred.
These concerns sit alongside the broader infrastructure risks discussed in our analysis of cyberattacks on energy, water and banks. Access to a trusted system can affect people who never chose the organization exercising it. The systems differ, but responsibility for that access remains a central security question.
Chinese Law and Intelligence Cooperation
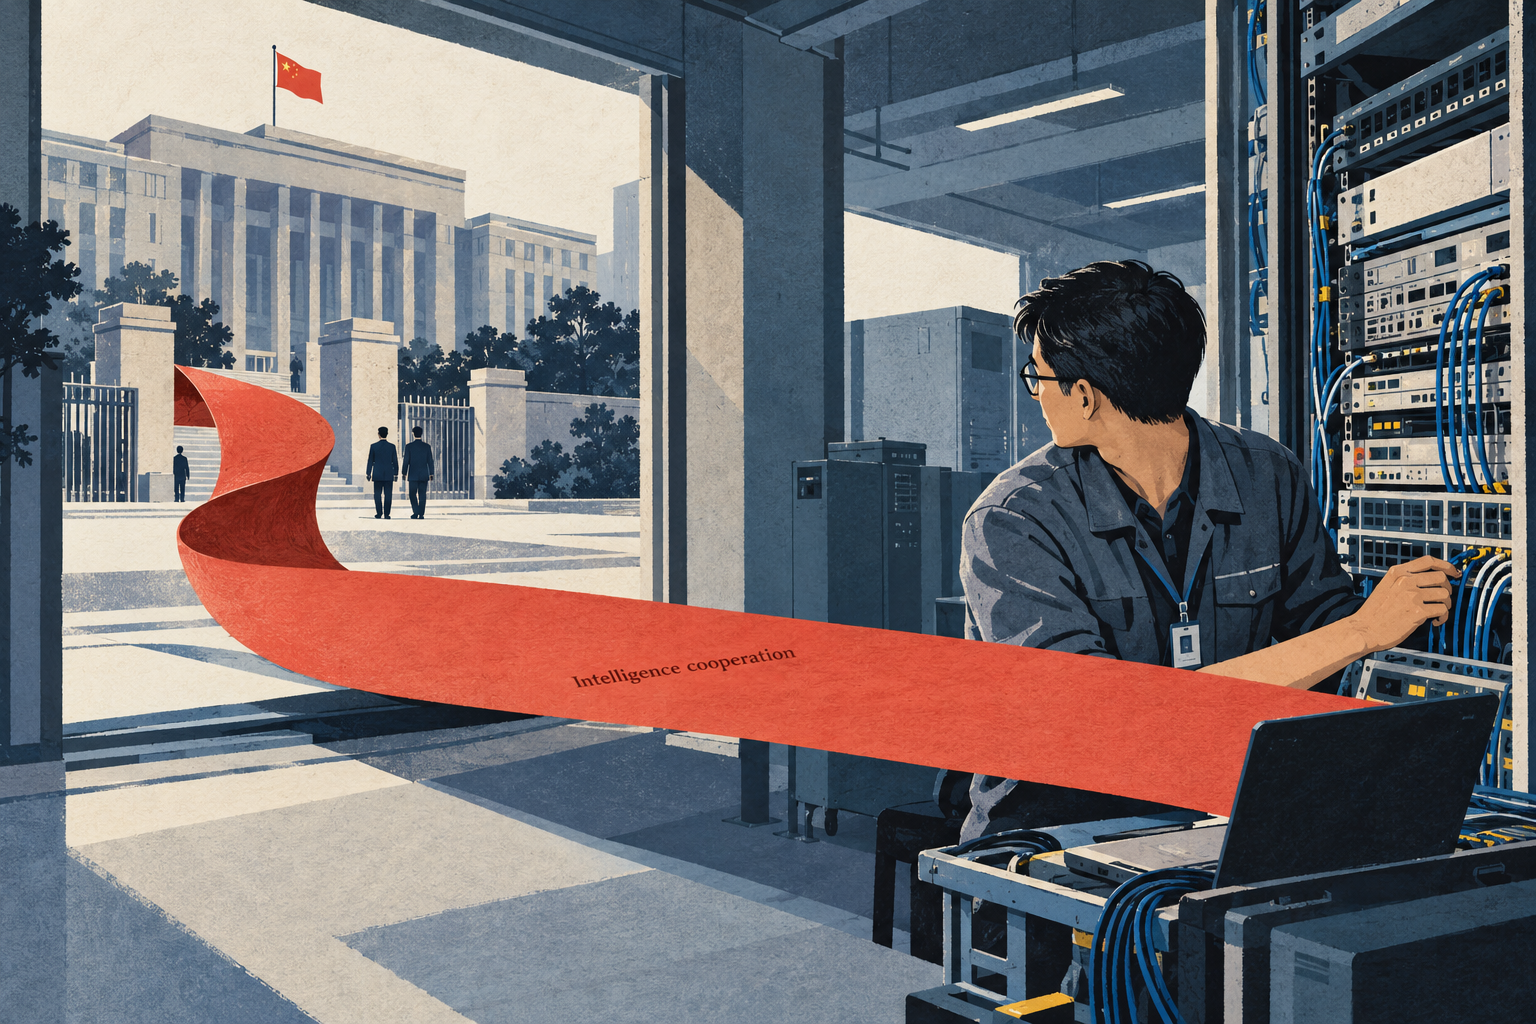
Chinese intelligence-cooperation requirements are part of the concern. In its 2020 assessment of Chinese intelligence-law powers, the FCC discussed Articles 7 and 14 as grounds for compelling organizational support and cooperation. For a state-linked telecom intermediary, that creates a reason to examine who controls the provider and what demands it may face.
A legal power to demand assistance is different from evidence that a specific request was made or a particular person’s communications were collected. Other jurisdictions also have compulsory-access mechanisms; the issue here is the Chinese institutional setting and its implications for a provider trusted with sensitive information. The law does not make every foreign operation automatically lawful under every other country’s rules.
What Information May Be Exposed
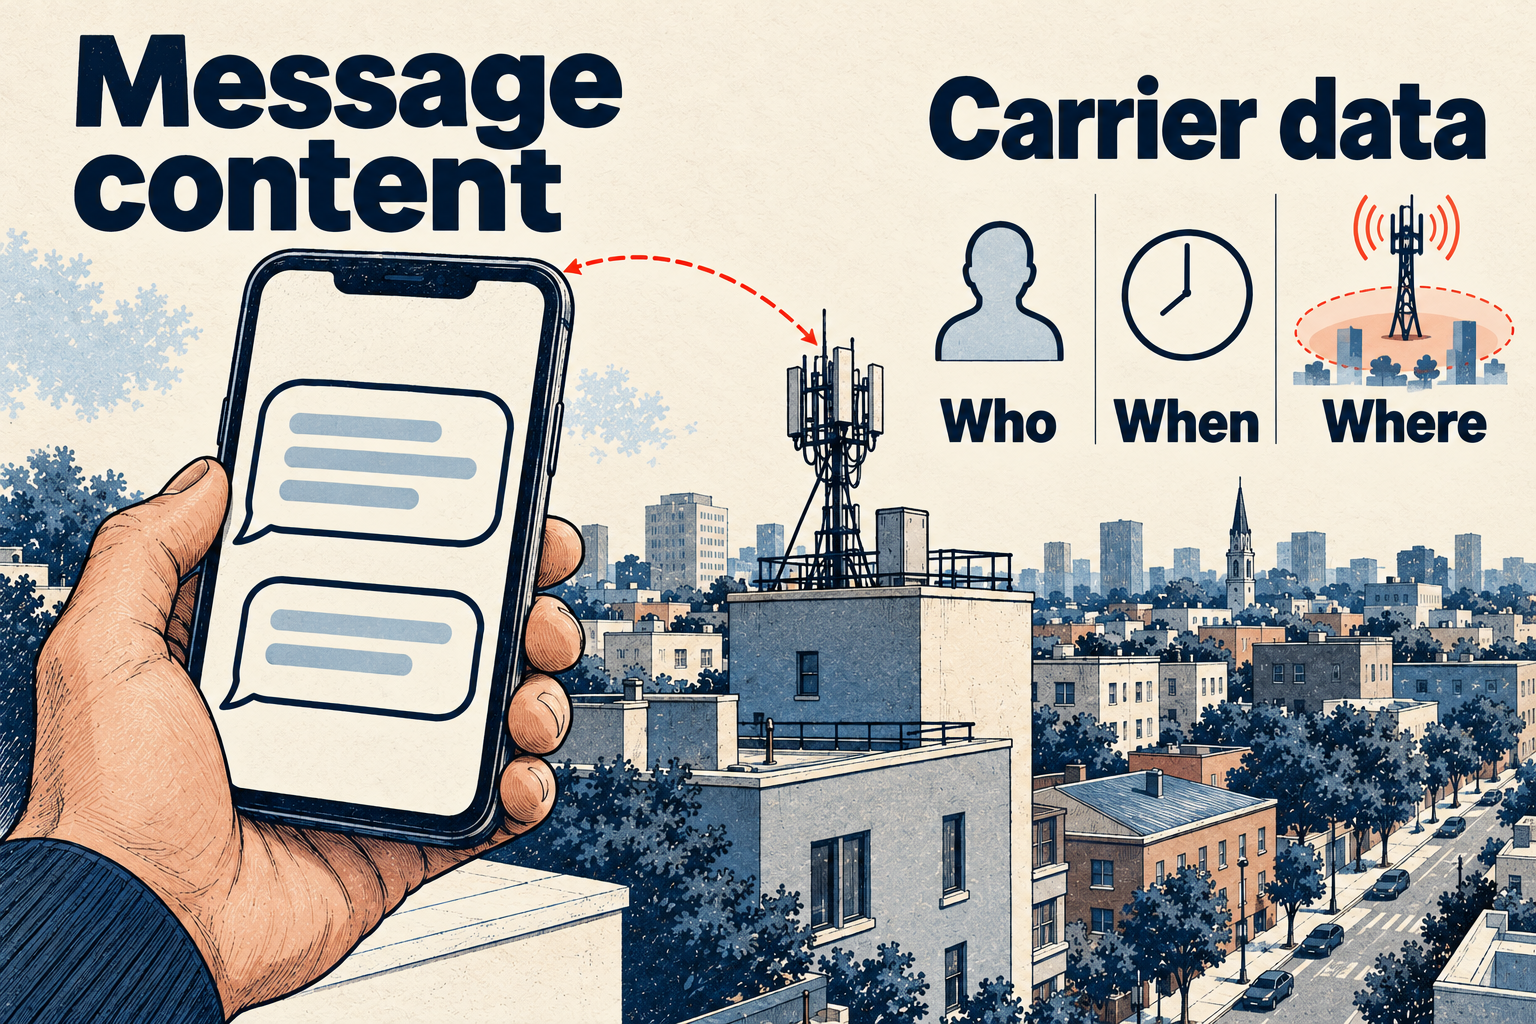
The information at risk depends on the network function, the intermediary’s access and the controls in place. The report describes why mobile-signaling relationships can be valuable to a party seeking to locate, identify or target subscribers. Possible exposure should be distinguished from a demonstrated collection of every item on every connection:
- Subscriber identifiers, including an IMSI associated with a subscription, can help identify a device or subscriber within the mobile system.
- Communication and routing information can reveal aspects of who communicated, when service was used and how communications were handled.
- Network-location and roaming information can reveal a subscriber’s presence or movements, with detail that depends on the information available.
- Abuse of SMS delivery or signaling access can put confirmation codes and other sensitive messages at risk. A code’s content is not simply the same thing as call metadata.
Metadata matters even when a conversation’s content is protected. Patterns of contacts, timing and location can reveal relationships and routines. That is sufficient reason to take the exposure seriously without claiming that one dataset tells everything about a person’s life. An encrypted app can protect a message’s content while the carrier still needs information to provide the phone’s network service.
Beyond Surveillance: Active Exploitation and Identity Theft
The security risks are not limited to passive observation. Depending on the access obtained and safeguards defeated, signaling abuse can assist targeted attacks. The potential consequences include:
- Intercepted confirmation codes helping an attacker who also has the credentials or other information needed to access an account.
- Communication redirection or manipulation that places a malicious party in a position to observe or interfere with delivery.
- Misuse of subscriber information to support impersonation, targeting or further attempts to compromise an account.
For businesses, the risk of espionage or account compromise via mobile signaling is a significant operational concern, particularly when operating abroad. The scope of this issue goes far beyond individual inconvenience. Communications may reveal professional relationships, travel or organizational activity. Business travelers, journalists, diplomats and others handling sensitive information need protections suited to their exposure; avoiding suspicious links alone does not address the infrastructure problem. Our Privacy & Identity Protection hub provides related guidance on limiting and responding to personal-information exposure.
What Users Can Do to Protect Themselves
The scale of the problem may feel overwhelming, but individual users are not powerless. While you cannot control a carrier’s interconnect choices, you can choose how to protect some communications and accounts. The useful distinction is between reducing a particular exposure and claiming to make the entire mobile system safe. Each control below acts on a different part of that problem.
Use End-to-End Encrypted Conversations
End-to-end encryption can protect message or call content between participating endpoints. It is useful when an intermediary handling the connection should not be able to read that content. Signal and WhatsApp provide end-to-end encrypted messaging and calling features, but the protection does not mean the phone’s carrier loses all knowledge of network use. It also does not protect readable content on an already compromised endpoint.
Email needs an additional distinction. A service associated with encryption does not make every exchange with every recipient end-to-end encrypted automatically. The 2019 ProtonMail security guide describes password-protected messages for recipients outside its service. Tuta’s explanation of confidential external email likewise describes a shared-password workflow. Check that the particular exchange uses the supported encrypted method rather than relying on the provider’s name alone.
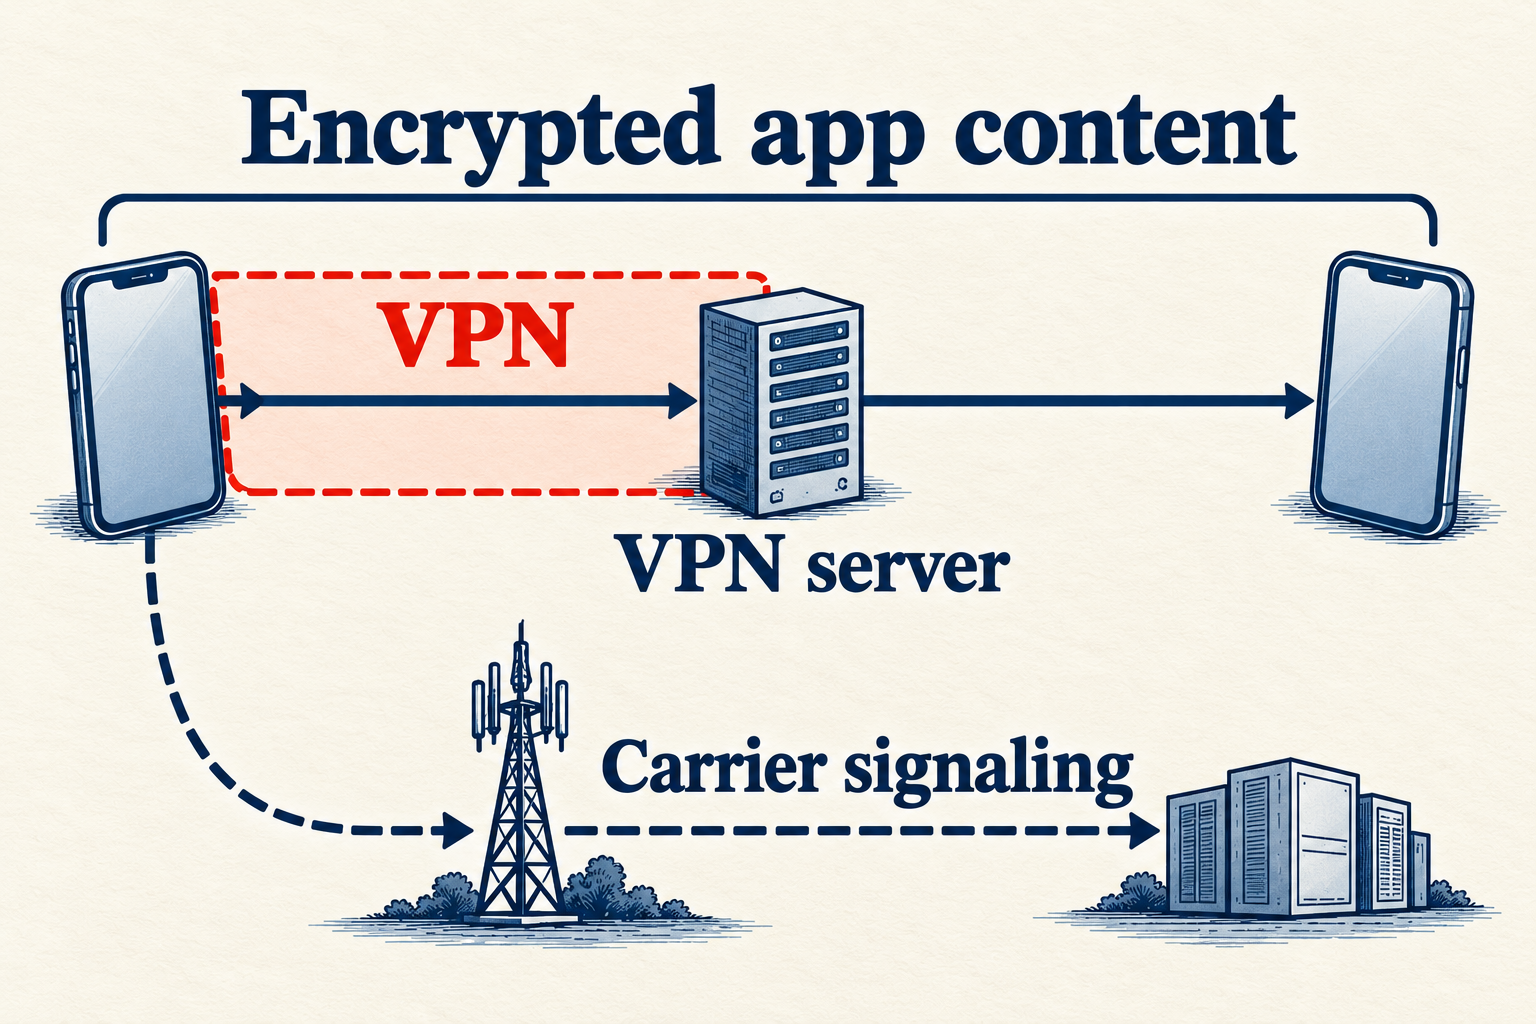
These tools can reduce the value of content available to an intermediary, but they do not erase every form of metadata. That is why the carrier-information question remains important even for a person who consistently chooses encrypted apps. Keep the content and network layers separate when evaluating what has actually been protected.
Use a VPN Within Its Actual Limits
A VPN protects internet traffic carried inside its tunnel between the device and VPN server. The explanation of VPN tunnels published by Proton VPN in 2023 describes that boundary and the importance of application encryption beyond the VPN endpoint. A VPN shifts trust to its operator; it is not a guarantee that every onward connection or application is confidential.
This tactic does not protect carrier signaling such as SS7 exchanges or hide the phone’s network registration from its carrier. It cannot give a user a preferred route for those separate functions. HTTPS and end-to-end application encryption remain relevant to the content they protect. A VPN’s price or home jurisdiction alone is not a substitute for examining its practices and the protection actually needed.
Understand Data Roaming, Permissions and Authentication
Turning off data roaming can limit cellular internet-data use on a visited network. It does not necessarily stop voice, SMS or the signaling used to register a phone there. Apple’s description of cellular-data settings distinguishes data roaming from other cellular-service settings. Treat a data control as a data control, rather than assuming it disconnects the handset from every foreign telecom function.
Review app permissions too. Disable unnecessary app location access and restrict unneeded background activity. These settings concern what apps can use or send; they do not control the carrier’s own interconnect arrangements. That distinction prevents a useful privacy habit from becoming an incorrect assurance about network-level surveillance.
Where a service offers an appropriate alternative, reduce dependence on SMS confirmation codes for sensitive accounts. An authenticator app addresses a different exposure from a VPN or an app-permission setting. Our guide to passwords, passkeys and two-factor authentication explains those choices. Changing the authentication method does not make every other part of the phone’s connection private.
Keep Device Security Separate from Route Visibility
An ordinary user generally lacks direct visibility into a carrier’s complete interconnect path. Do not assume that installing a security app will reveal whether signaling is handled by a particular transit provider. In its February 2025 account of device threat hunting, iVerify described device scans for signs of compromise. That is a different claim from observing all of a carrier’s routing relationships.
Device hardening and threat detection can still be useful within their stated scope. A clean result does not establish that every signaling exchange was safe, and a provider’s infrastructure research does not automatically describe a consumer-app feature. For an organization, specialist advice and questions to its mobile-service provider may be more relevant than expecting employees to interpret network paths from their handsets.
These actions are not silver bullets. They protect different information and reduce different opportunities for abuse, while the larger infrastructure decisions remain with carriers and governments. Our Cybersecurity Basics hub connects those individual precautions with broader account and device practices. The burden should not fall entirely on users to compensate for arrangements they cannot see.
Why the Accountability Gap Persists
Given the seriousness of these surveillance concerns, one might expect more coordination and clearer responsibility. Yet global telecommunications crosses organizations and jurisdictions with different powers and priorities. Existing standards and government actions do not remove the need to ask how effectively they constrain a specific intermediary or protect the subscriber whose information is involved.
Global Telecom Is a Fragmented and Legacy-Driven System
At the heart of the issue is infrastructure inertia. Established signaling systems and interconnect relationships support ordinary mobile service, especially international mobility. Changing those arrangements involves more than replacing a device or updating an app. Carriers must maintain reliable service while managing trust, security and dependencies across partner networks.
The problem is systemic as well as technical. Improvements can involve modernizing infrastructure, changing interconnect contracts, restricting access and clarifying responsibility between providers. Those tasks require coordination. The existence of standards does not establish that every deployment follows them effectively, just as a commercial agreement does not answer every question about the risks to subscribers.
Cross-Border Processing Is Not Outside Privacy Law
It is too broad to say that privacy law covers storage but not transmission. The GDPR’s definition of processing and international-transfer framework can be relevant to disclosure and cross-border handling where its conditions apply. Whether a particular arrangement falls within those provisions depends on the entities, processing, access and jurisdiction. A network diagram alone does not establish a legal violation.
The narrower accountability gap remains: a person choosing a mobile service has little practical ability to inspect the full interconnect chain or negotiate its security. National rules do not amount to one simple worldwide routing-transparency regime. Meaningful oversight requires understanding the arrangements in question, rather than assuming that data becomes unregulated whenever it crosses a border.
Political Sensitivities and Economic Dependence
Telecom policy isn’t just a technical issue; it’s a diplomatic one. Challenging these arrangements would require more than technical upgrades. It could involve disrupting business deals and straining diplomatic relationships while maintaining international service. Those dependencies can make reform difficult, without proving that every carrier knowingly sacrifices privacy or that one profit motive explains every insecure arrangement.
The U.S. response was not limited to restrictions on Huawei and ZTE hardware. The FCC denied China Mobile USA’s international-service application in 2019 on national-security grounds. Such action matters, but it does not resolve the worldwide interconnect exposure described by iVerify. The criticism is that significant dependencies and opaque trust relationships can remain despite action in one jurisdiction.
That is why user vigilance alone is insufficient. Carriers should be accountable for their partner choices, and government oversight should address how those choices affect subscribers. A system can deliver a reliable connection while failing to give its customers a meaningful account of who is trusted with the information behind it.
Conclusion and Future Outlook
What the iVerify report reveals is not just a technical vulnerability or an obscure network concern; it is a failure of global accountability. Your privacy does not end at the border, and it does not fit neatly within your choice of carrier. The documented interconnect dependencies deserve scrutiny because technical access, provider control and intelligence-cooperation pressure can combine in ways the user cannot readily assess. Customers should not have to discover those institutional risks through an outside investigation.
The finding of 60 operators in 35 countries should be read for what it establishes, without turning it into proof of every route or interception. Precision strengthens the warning. The problem is not made less serious by distinguishing a potential surveillance opportunity from a demonstrated operation; it becomes easier to identify which organizations and safeguards need examination.
The future may bring stronger demands for transparency and clearer assurances from telecom vendors. Those are policy choices, not outcomes established by this investigation. For now, useful individual protections should be understood within their limits, while responsibility for the infrastructure remains with the organizations operating it. Trust should depend on evidence and accountability, not simply on a familiar name on a phone bill.
Frequently Asked Questions
How do I know if my mobile signaling uses a Chinese-owned provider?
Most users cannot inspect that complete relationship directly. The iVerify report examined operator documentation; it was not a consumer-app reading of every phone’s path. Device-security tools can address their stated functions, but their results should not be treated as a complete carrier-routing map. A provider’s participation also does not prove physical transit through mainland China.
Does a VPN protect my signaling data?
No. A VPN protects internet traffic carried inside its device-to-server tunnel, not the carrier’s separate signaling or network registration. It does not replace HTTPS or end-to-end encryption for the content those systems protect. Choose a control for the exposure it actually addresses rather than expecting one tunnel to protect every layer.
Is this surveillance legal?
Chinese intelligence-cooperation powers create an access concern, but they do not establish the legality or occurrence of a particular operation. Other countries’ privacy and telecommunications rules may also be relevant. The article’s warning concerns institutional leverage and exposure; it is not a legal verdict on every provider relationship listed in the report.
Does this prove U.S. carriers sent all customer data through China?
No. A list of interconnect relationships does not establish that every U.S. carrier or subscriber used a particular route. International travel and partner networks can create dependencies, but those must be evaluated in their actual scope. The article’s concern is the trust placed in intermediaries, not an unsupported claim about all American mobile traffic.
What is the risk for businesses and professionals?
The consequences can be serious when communications reveal sensitive work, contacts or travel. Businesses should distinguish device compromise, message-content exposure and carrier-signaling risk when considering protections. Staff precautions help within their limits, while questions about network partners and institutional access require attention from the service provider and, where appropriate, specialist advisers.