The U.S. has dismantled a foundational element of its cybersecurity coordination strategy. The Critical Infrastructure Partnership Advisory Council, or CIPAC, brought government and infrastructure owners together to discuss shared risks. Removing that forum does not switch off every information-sharing channel, but it leaves an important partnership problem to solve.
The Department of Homeland Security's March 13 termination notice made the decision effective March 7, 2025. The Trump administration chose to end a longstanding framework; it now bears responsibility for explaining how its work will continue.
What follows is a breakdown of why the council mattered, seven risks its removal creates, and what industry and policymakers should do to protect the systems we all rely on.
Key Takeaways
- CIPAC supplied a joint advisory framework for government and critical infrastructure partners.
- DHS terminated it while implementing Trump's reduction of federal advisory bodies.
- Its FACA exemption supported sensitive discussions; it was not blanket secrecy or immunity from liability.
- Other sharing authorities, sector councils and response relationships did not automatically disappear.
- The urgent task is to preserve useful collaboration, clear responsibilities and trust during the transition.
What CIPAC Was—and Why It Mattered
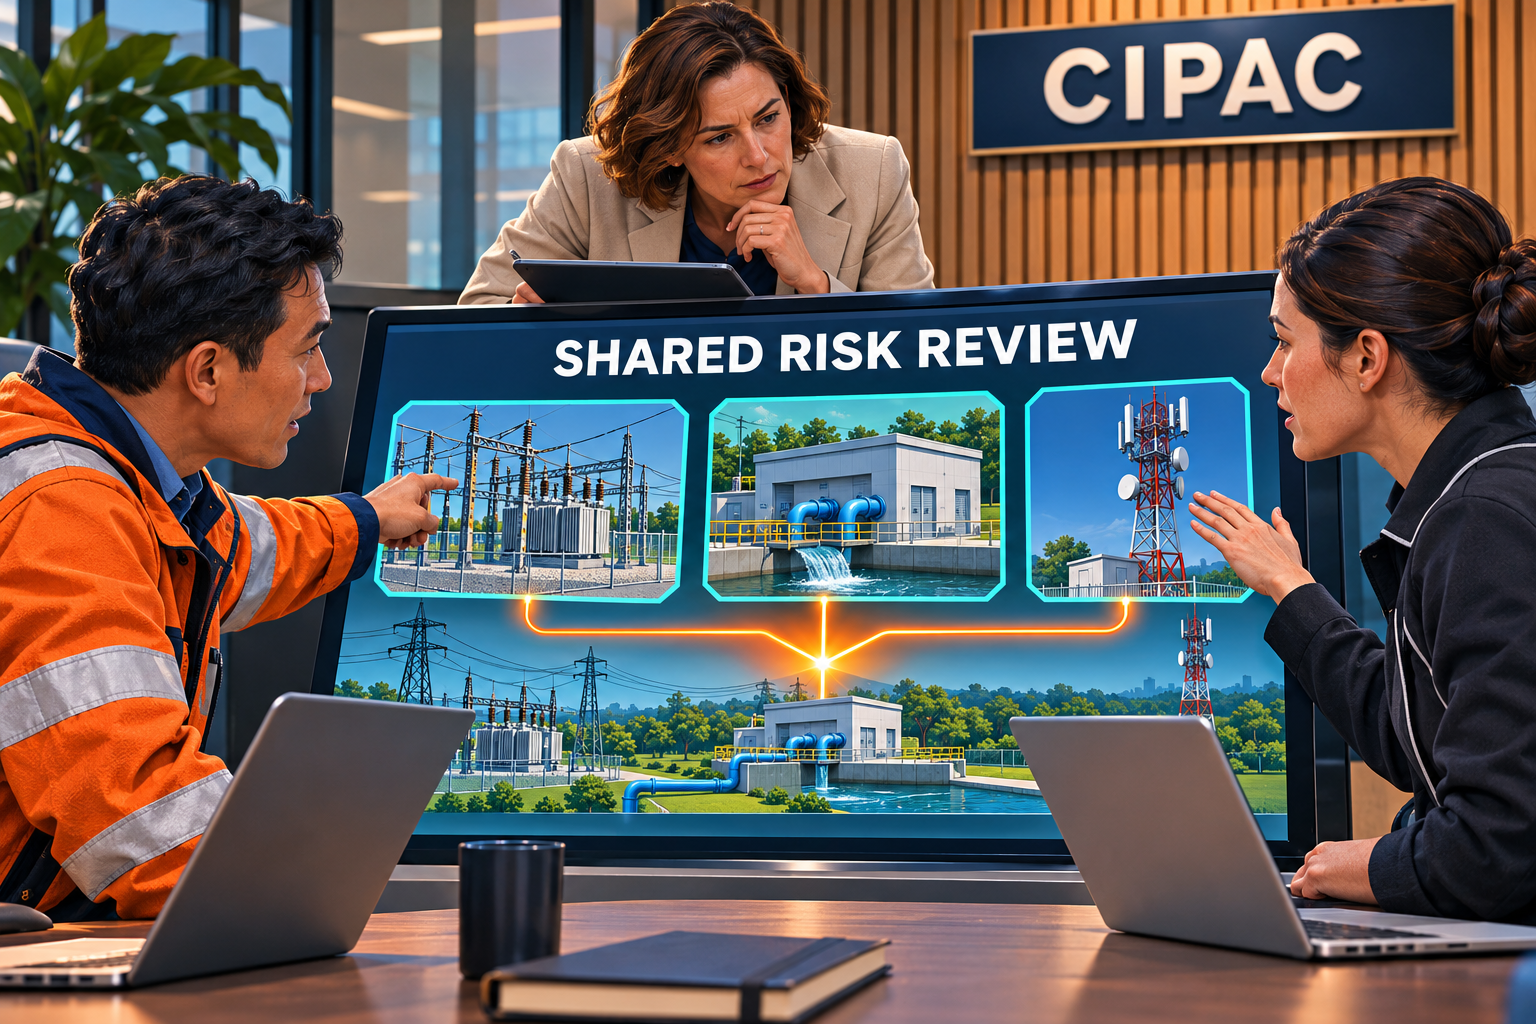
DHS's 2006 establishment notice created the council to support the National Infrastructure Protection Plan's partnership model. It brought together private-sector Sector Coordinating Councils and Government Coordinating Councils, which included federal, state, local, tribal and territorial representatives.
This was a forum for joint deliberation: assessing risks, discussing priorities and developing advice about infrastructure protection. It was not an incident command center, a replacement for CISA, or an agency with power to set federal policy.
Its exemption from the Federal Advisory Committee Act mattered because ordinary committee requirements for open meetings, advance notice and related materials could inhibit timely discussions of sensitive vulnerabilities. The exemption made those discussions more workable. It did not promise that every exchange was confidential under every law, or protect companies against every possible lawsuit.
The charter also distinguished joint meetings from meetings involving only a sector council or only a government council. Ending this framework did not itself dissolve those independent bodies.
Why the Administration's Decision Matters
On February 19, Trump issued Executive Order 14217, directing reductions in federal bodies and identification of additional committees for termination. The order did not name CIPAC. The DHS secretary's subsequent decision did.
The termination notice described the action as in the department's best interest, consistent with the order. It did not explain how each council's useful functions would be preserved or identify a successor to this one.
That is the basis for criticism. Cutting a partnership structure is not the same as demonstrating that its work is unnecessary. The administration should explain who will convene participants, hear operational concerns and maintain continuity—not merely announce that the committee is gone.
The loss was already prompting an industry response. At the March 11 House cybersecurity hearing, Cybersecurity Coalition coordinator Ari Schwartz urged reinstatement and warned that the decision would make gathering sector feedback on incident-reporting rules harder. That is a concrete concern about the forum's value, rather than proof that all national cyber response has stopped.
Seven Risks After CIPAC's Termination
These are risks to manage, not a claim that seven measured failures have already occurred.
1. A trusted place for joint work is lost
Relationships are useful when the next problem does not fit neatly inside one organization. Without a familiar forum, participants may spend time finding the right counterparts or negotiating how a joint discussion should work. Keeping contact lists is important, but it does not by itself replace a continuing working relationship.
2. Industry feedback can become harder to gather
Infrastructure owners need a practical way to explain how proposed policies will affect their operations. The March hearing's concern about sector feedback illustrates the issue. If consultation becomes a series of disconnected exchanges, government may miss common problems or receive an incomplete picture before making decisions.
3. Sensitive advisory discussions face uncertainty
Participants need to know the rules for discussing vulnerabilities, commercial concerns and infrastructure dependencies. Removing an established framework without explaining the alternative can create hesitation. That uncertainty concerns the arrangements for joint advisory work; it does not mean every other route for exchanging threat information has become unlawful.
4. Cross-sector dependencies can receive less attention
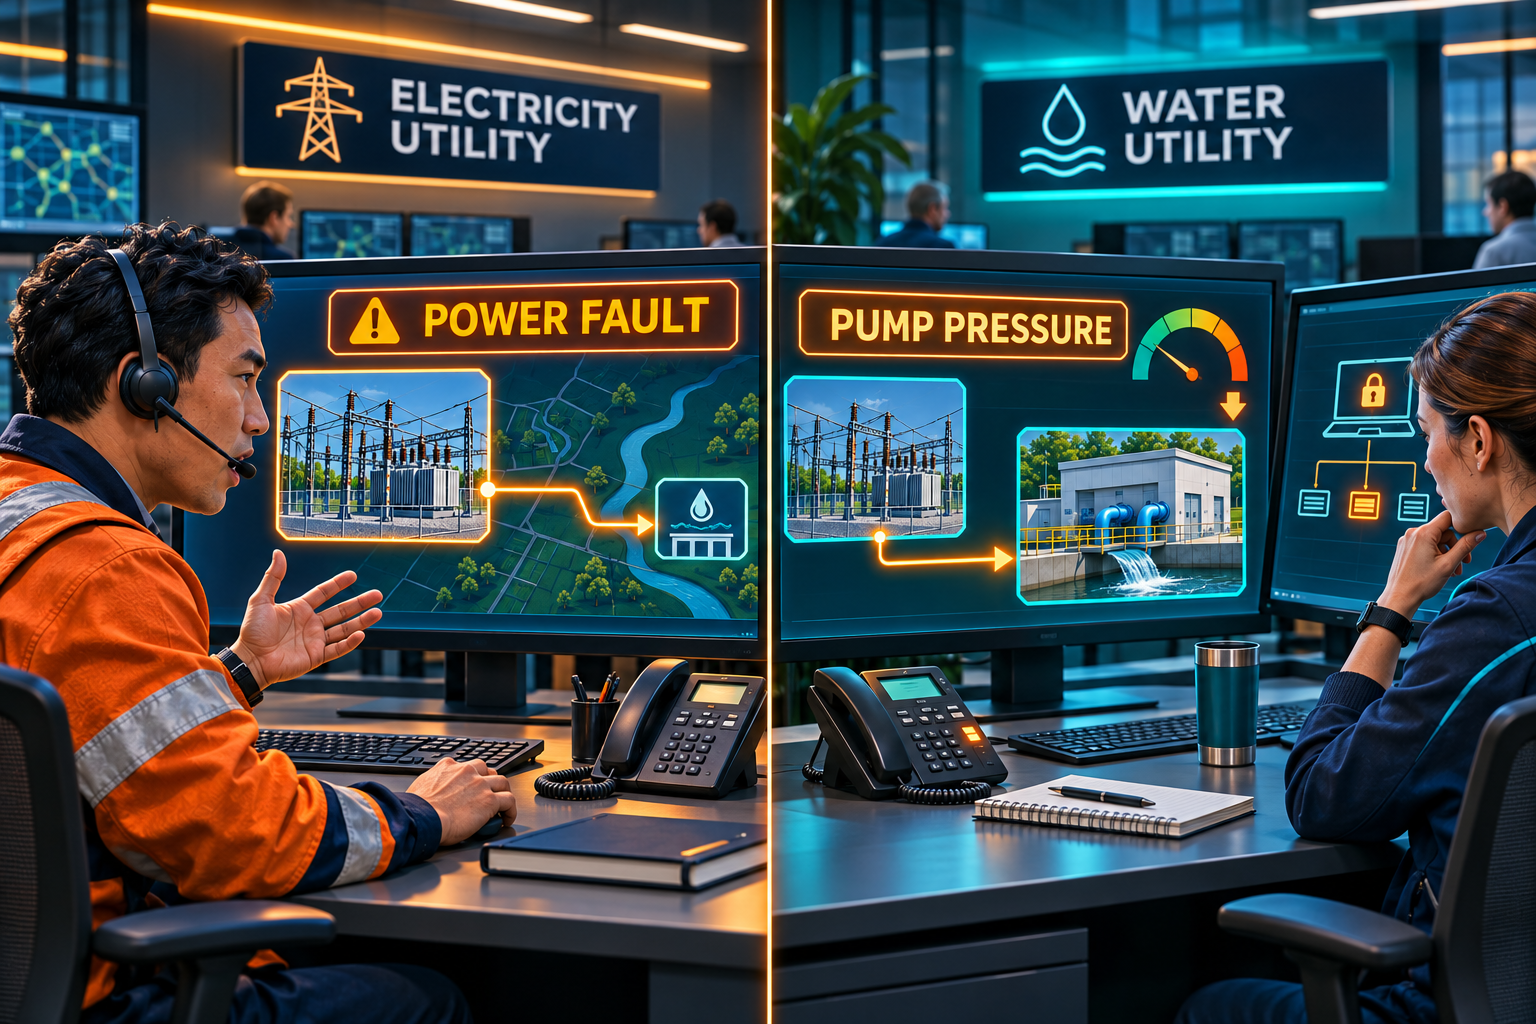
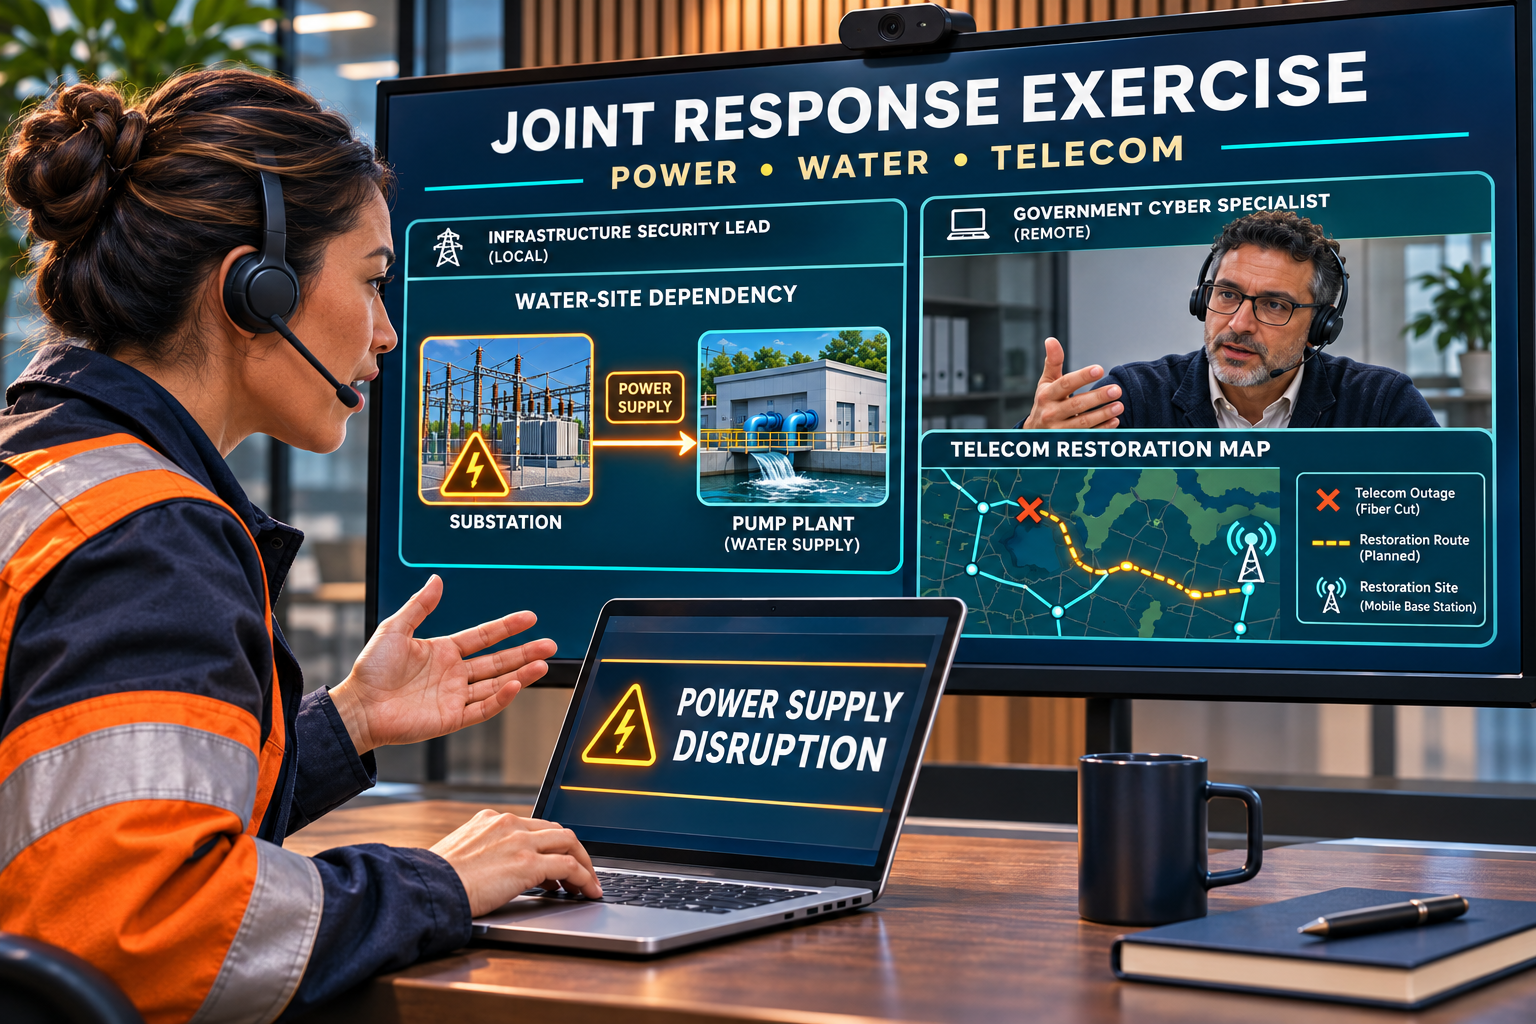
Critical infrastructure sectors are deeply interdependent. Consider a hypothetical incident affecting electricity and water operations. Each operator may understand its own systems while missing the other sector's constraints. Existing response channels can still function, yet a weak shared picture can complicate priorities and coordination.
5. Smaller jurisdictions may struggle to be heard
State and local participants need a place in discussions that affect essential services. A fragmented consultation process risks favoring organizations with the resources to maintain many separate federal relationships. The challenge is to preserve participation—not to assume that every smaller jurisdiction has lost access to threat information.
6. Crisis communications can become inconsistent
During a cyber event, conflicting reports can sow public confusion and distrust. Agencies, vendors and infrastructure owners need clear responsibilities for checking facts and communicating uncertainty. Election infrastructure offers one example where coordination matters; the council's closure does not establish that all election-security collaboration has ended.
7. Rebuilding consumes time and tests accountability
A successor arrangement needs more than a new name. Someone must define its purpose, invite the right participants and maintain a useful process. If the administration removes an existing mechanism without explaining that work, it creates a transition burden for the very organizations expected to protect essential services.
What Did Not Disappear
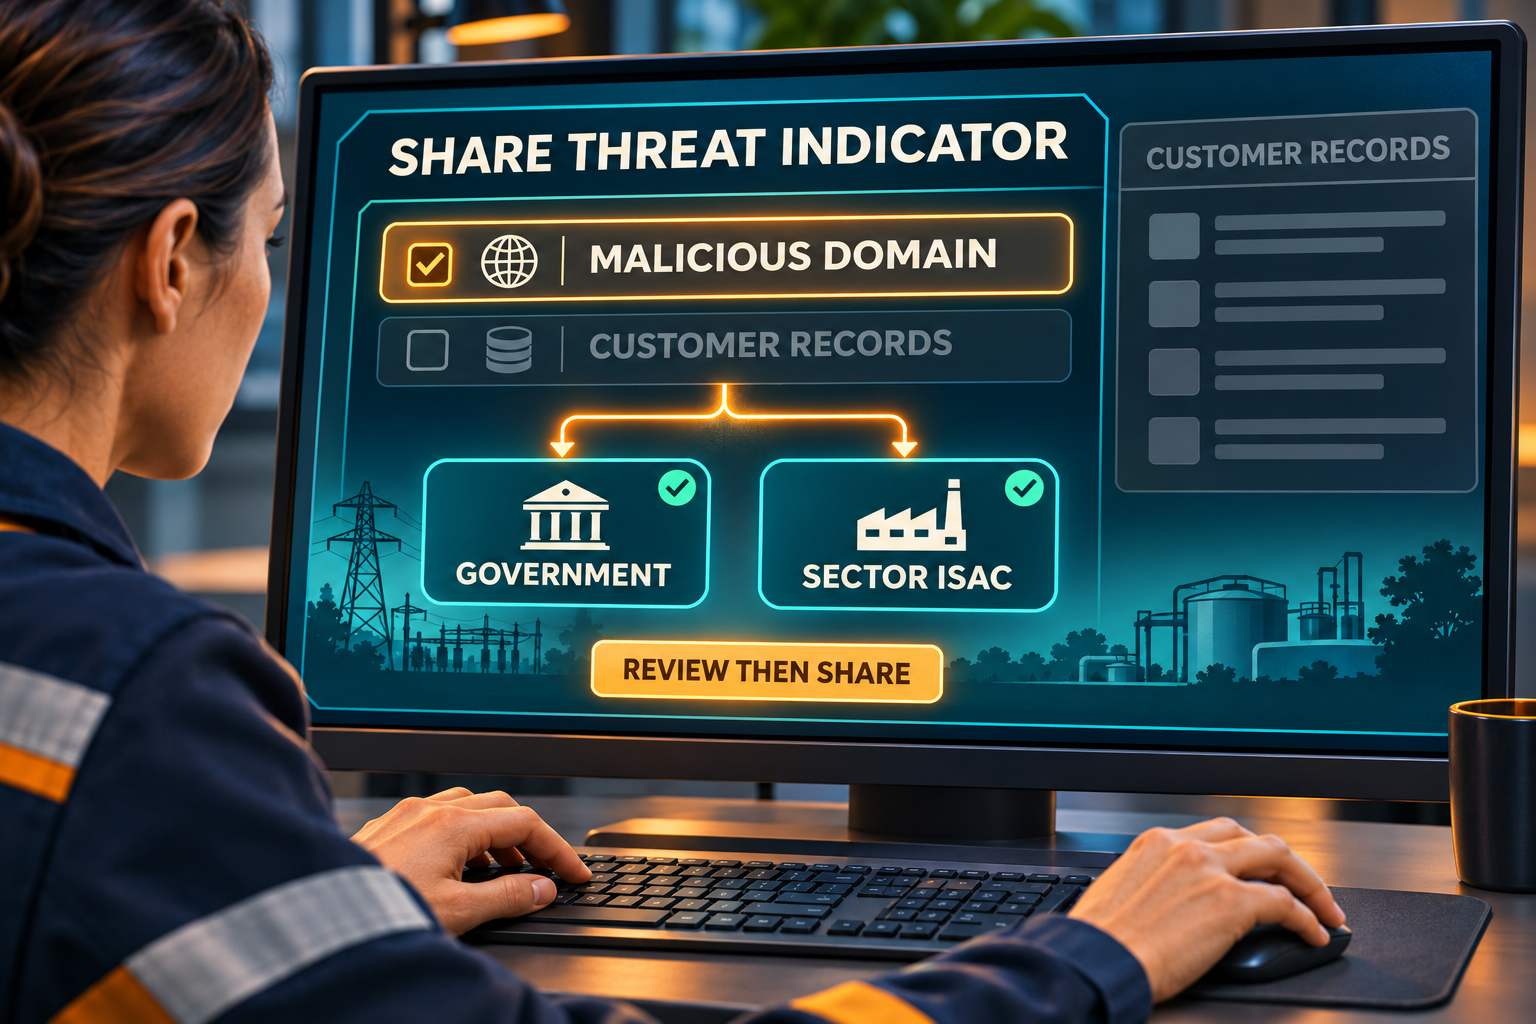
The Cybersecurity Information Sharing Act of 2015 supplied separate authority and conditional protections for qualifying exchanges of cyber-threat indicators and defensive measures. Those protections depended on the activity and compliance with the law; they were not permission to share any data by any method.
Terminating an advisory council did not repeal that statute. Nor did it eliminate CISA, independent sector councils or every government–industry relationship. These distinctions do not excuse the decision. They identify the actual loss so that criticism and corrective action address the right problem.
Organizations should also distinguish useful technical information from unnecessary personal information. Our Privacy & Identity Protection guide provides broader context for that boundary; the applicable sharing rules still require their own attention.
What Industry and Policymakers Should Do Now
Until the administration explains a workable arrangement, companies and public agencies should:
- Maintain existing relationships. Continue appropriate contact with sector Information Sharing and Analysis Centers and government counterparts; identify where joint advisory work now lacks a home.
- Document sharing rules. Establish what may be shared, with whom, through which process and under which authority. Do not treat a former committee exemption as a universal legal shield.
- Ask for a concrete transition plan. DHS and CISA should explain how participants will provide feedback, discuss sensitive risks and coordinate across sectors.
- Keep oversight focused on functions. Congress should examine what was lost and what a replacement must accomplish, rather than assume that renaming a council fixes the problem.
- Keep ordinary security work moving. Coordination complements the controls explained in Cybersecurity Basics; it does not replace them.
The wider question—whether administrative changes strengthen or disrupt security work—also appears in our analysis of Musk's workforce directive and cybersecurity risk.
Conclusion: Collaboration Must Be Rebuilt
Cybersecurity is a collective responsibility. Dismantling the architecture of trust between government and industry is a setback, even when other legal authorities and sharing channels remain.
The Trump administration should be judged on whether its restructuring preserves effective cooperation, not on how many advisory bodies it eliminates. DHS, CISA and Congress must make the arrangements for joint work clear. Infrastructure partners should not have to guess how a useful public-private forum will be replaced.
For future analysis of cybersecurity policy and infrastructure protection, subscribe to Quantum Cyber AI.
FAQ
Did Executive Order 14217 itself abolish CIPAC?
No. Trump's order directed reductions and identification of additional bodies. DHS separately terminated the council effective March 7, 2025, in its March 13 notice.
Did the FACA exemption guarantee secrecy and immunity?
No. It addressed advisory-committee procedures that could impede sensitive joint discussions. It was not a blanket confidentiality rule or protection against every kind of liability.
Can companies still share threat information?
Yes. Separate sharing authorities and relationships remained. Legal protections depend on the information, activity and applicable requirements; committee termination does not make every exchange either prohibited or protected.
Was a replacement identified in the termination notice?
No. The notice did not identify a successor. Industry testimony called for reinstatement. The immediate policy question is how the administration will preserve the useful work.
Why does this matter if CISA still exists?
An agency and a joint advisory forum perform different functions. Keeping the agency does not automatically preserve the structured government–industry deliberation that the council supported.