You are reading a page when a security warning suddenly fills the screen. It may say your computer is locked, play a harsh sound, display a familiar logo, and insist that you call a support number immediately. The safest first move is simple: do not call the number or use a button inside the warning. Close the tab or browser and check your device through a route you choose yourself. The Federal Trade Commission's guidance on tech support scams says real security pop-up warnings do not ask you to call a phone number.
The warning is designed to make a decision feel urgent. Seeing it, however, does not by itself tell you whether anything was installed or whether an account was accessed. Your next steps depend on where the message appeared and what, if anything, you did after seeing it. This guide separates a fake page from a website notification and a genuine alert inside your security software, then gives you a practical response for each.
Key Takeaways
- If an unexpected security warning displays a phone number, do not call it. Close the page and choose your own trusted route to check the device.
- A page can look like a system warning, even in full screen. Appearance and volume are not proof that the operating system found a problem.
- A site notification can keep appearing outside the page because the browser was allowed to show it. Review that site's permission in browser settings.
- A warning you see inside a security app you opened yourself deserves attention. Check that app's status and scan results, without following links from the suspicious message.
- A download you never opened needs a different response from installed software, remote access, a shared password, or a payment. Choose recovery steps based on what actually happened.
What to do in the first minute
Stop the requested action
The warning wants an immediate response. Refuse its choices. Do not call the displayed number, click a repair button, run a command copied from the page, install a suggested program, or enter a password, card number, or verification code. These are different actions with different consequences, but none needs to happen before you can leave the page. If someone nearby is frightened by the sound or the apparent lock screen, say what you know: you are closing the warning and checking the device separately.
You also do not need to photograph the warning before closing it. If a screenshot is easy to take without interacting with the page, it can help later with a report. It is optional. Your immediate job is to stop following the message. Likewise, do not stay on the page to search its text for a clue. Once a warning tries to move you into a phone call, its information is no longer a trustworthy route to support.
Close the tab or browser using its own controls
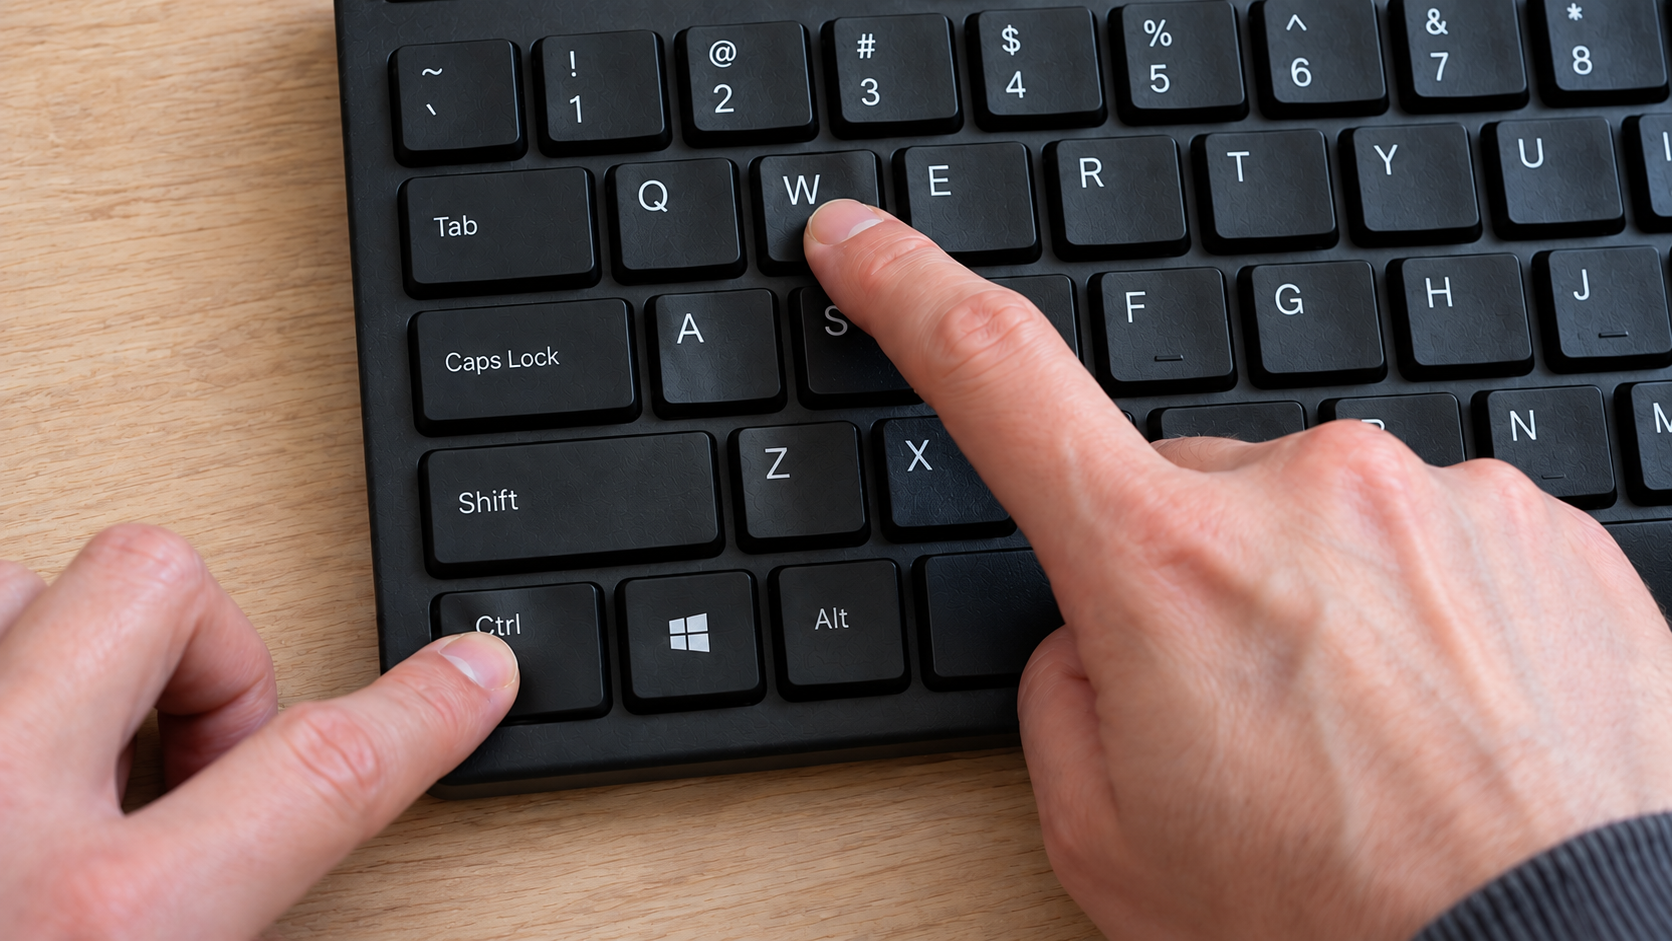
Use a control belonging to the browser or operating system, rather than an X or “Close” button drawn inside the warning. The distinction can be hard to see when a page fills the screen, so a keyboard shortcut can give you a separate way out. Google's Chrome keyboard-shortcut guide lists Ctrl+W on Windows and Command+W on Mac for closing the current tab. Start with the current tab; you do not need to delete your browsing history or reset the device just to leave one alarming page.
If the tab will not close, choose the instructions that fit your device:
- Windows: Try closing the browser window. Microsoft's Windows keyboard shortcuts include Alt+F4 for the active window. If the browser remains unresponsive, Ctrl+Shift+Esc opens Task Manager. Microsoft describes Task Manager as a way to terminate unresponsive programs. Find the browser in its running-app list and end that task; ask a trusted helper if you cannot identify it. Do not end unfamiliar system processes at random.
- Mac: Try Command+Q to quit the browser normally. If it does not respond, Apple's force-quit instructions say to press Option+Command+Esc, select the unresponsive app, and choose Force Quit. If force quitting fails, use the Apple menu's Restart command.
- Phone or tablet: Open the browser's own tab overview and close the suspicious tab. If the browser is frozen on an iPhone, Apple's instructions for closing an unresponsive app describe opening the app switcher and swiping up on the app's preview; devices with a Home button use that button to open the switcher. On another device, use its normal app controls or the manufacturer's support instructions.
Quitting or force quitting a browser can lose unsaved work in its other tabs. In this situation, leaving the warning safely takes priority over completing the page's instructions. When you reopen the browser, decline an offer to restore the suspicious tab. If the warning returns with a restored session, leave that tab again rather than calling the displayed number. Closing a window stops displaying the page; it does not uninstall software, remove a website notification permission, or reverse information you already shared.
Verify from a separate starting point
On Windows, you can open Windows Security from the Start menu and review Virus & threat protection. Microsoft's guide to the Windows Security app explains where to see current threats, protection history, protection updates, and scan options. If you are concerned, update the protection information and run a scan from there. Do not use a security-app shortcut supplied by the suspect page, because that keeps the page in control of your route.
On another device, use the security or system tools you already have and the manufacturer's official support path you navigate to yourself. If you are unsure which protection tool is installed, do not buy one because the warning tells you to. A trusted helper can help you locate the tool you already use. The goal is modest and practical: check a possible problem through a channel that the warning did not select.
Why a fake security warning looks convincing
A web page can imitate the computer
Consider an illustrative example. You click an ordinary search result. A large window announces that your device is infected, uses the colors of a well-known software company, and warns that files will be lost unless you call a number. There may be a countdown or a voice repeating the instruction. The screen looks official because the page is using your entire display to stage the message, not because your device has independently confirmed it.
Microsoft's explanation of tech support scams describes fake error messages, full-screen pages, repeated pop-ups, and audio that can make a browser appear locked. Microsoft also says its error and warning messages do not include phone numbers. These techniques explain why an ordinary page may feel like a Windows alert. The familiar appearance invites trust; the noise and repeated dialogs make leaving feel difficult. The warning then presents a call as the apparent solution, even though the page has not established that your device needs repair.
The warning's claim is not a diagnosis. Keep two observations separate: what the page says, and what a trusted security tool actually finds. A frightening message does not prove infection, while closing it does not prove that an installation or account exposure never happened. This is why the first response is to leave the page and the second is to consider what you did. The distinction avoids both unnecessary panic and false reassurance.
The phone number is the pivot
The phone number moves the encounter from a warning page into a conversation. In the FTC's description of the scam, the supposed technician asks for remote access, claims to find a virus, and offers a paid repair. A call is therefore an important decision point: it creates an opportunity for further requests. Recognizing that transition lets you stop before you install a tool, disclose a code, or authorize a payment.
Do not debate whether the logo looks accurate or whether the warning knows the name of your device. A familiar brand and technical-sounding message are easy to display on a page. You do not need to solve the entire question while the page is flashing. The safer decision is to stop following its directions. If you later need support, open the manufacturer's or service provider's official app or site yourself, use a number already in your account materials, or contact a trusted person. The number inside the alert never gets to choose whom you call.
Is this a web page, a website notification, or a real device alert?
A warning inside the tab you were browsing
Start with where the message lives. Did it appear just after a website loaded or an advertisement opened? Can you see a browser tab behind it? Does closing that tab remove the warning? These observations point toward a page-level warning. They do not tell you why that page opened, and they do not guarantee that no other interaction occurred. They give you a way to leave the message without trusting its buttons.
Apple warns that browser pop-ups claiming a virus or security problem are usually fraudulent ads that try to get a download, information, or money. Its advice on suspicious browser pop-ups is to ignore the message and navigate away or close the tab or window. This applies to the decision in front of you, including on a phone or tablet: close the suspect page instead of following its support link. You can then revisit what happened before the alert appeared. For example, a link from a message or an unfamiliar search result may explain the page, but the explanation is separate from whether you gave it anything.
If you close the tab and nothing else happens, avoid turning the incident into a presumed infection. If the browser reopens the same warning page, starts loading unexpected tabs, or behaves differently afterward, that is a reason to check browser settings and run a trusted scan. Make the response fit the evidence.
A website notification outside the tab
Some alerts are not page pop-ups. They appear near the corner of a desktop screen or in a notification center. They may arrive while you are doing something unrelated to the website that originally asked for permission. Google explains in its Chrome guide to website notifications that sites can request permission to send them and that those permissions can be changed in Settings > Privacy and security > Site settings > Notifications. A warning that appears outside a tab may therefore come from a website with permission, not from the device's antivirus app.
Do not click a notification just to learn what it is. Open the browser's settings yourself and inspect the allowed sites. If an unfamiliar site can send notifications, block it. This is different from blocking ordinary pop-up windows, which have their own setting. If you do not know which browser is responsible, look at the notification's sender label, then open that browser from its normal icon rather than interacting with the alert. A blocked permission addresses the repeated interruption; it does not erase any separate download or information you may already have given.
An alert inside your security software
A genuine security finding can also occur, which is why the response is independent verification rather than blanket dismissal. Close the suspect web content first. Then open the security app from your device's normal application menu or system settings. Look for current threats, protection history, or scan results there. If the app reports a finding, follow the instructions within the app and seek trusted support if you cannot interpret it.
Notice the difference in control. When you choose the app yourself, the scary page does not dictate a phone number, a download, or a payment method. You can check whether there is an actual finding, when it occurred, and what action the app recommends. If the device belongs to your employer or school, use the organization's known IT channel, especially before removing software or changing settings on a managed device.
If the warning returns, find its source
Review notification permissions first
If an alert keeps arriving as a desktop notification, look for a website permission rather than assuming that a tab is still open. Microsoft says Edge site notifications can appear in the lower corner or notification center and can continue while Edge is closed. Its Edge notification guide gives a way to block a site through Settings > Privacy, search, and services > Site permissions > All sites, then the site's Notifications setting. Chrome has a separate Notifications page under Site settings. These paths may move as browser versions change, so use the browser's settings search for “notifications” if the labels differ.
Check the site name before blocking it. A familiar service you chose to hear from is different from an unknown domain that began sending virus warnings. If you accidentally granted a suspicious site permission, removing that permission is a direct fix for the alert's delivery route. It is not a substitute for checking the device if you also downloaded or installed something. Nor does a system-style icon on the notification prove the operating system issued it. Read the sender and go to settings without opening the notification itself.
Look for changes beyond one page
A single scary warning page and ongoing browser misbehavior are different observations. Google lists pop-ups or tabs that will not go away, redirects to unfamiliar pages, unexpected changes to the homepage or search engine, and recurring unwanted extensions as possible signs of unwanted software or malware in its Chrome troubleshooting guidance. The guidance does not say every such symptom proves an infection. It gives reasons to check instead of ignoring persistent behavior.
Begin with simple observations. Does the warning appear only on one website? Does it arrive as a notification even after leaving that site? Do unfamiliar extensions appear in the browser? Did a new application get installed? If you can answer those questions, you can choose a focused remedy: leave the bad page, block a notification sender, remove an unrecognized extension or application with trusted assistance, reset affected browser settings, or run a scan. Avoid downloading a random “cleaner” found through the same warning or a search ad.
If the behavior continues after you remove an unwanted permission and scan, seek help from a known technician, the device maker, or your organization's IT team. Tell them what you actually saw and did, including any software installed or access granted. That short history is more useful than the alarm's claim about how many threats it supposedly found.
If you interacted with a tech support scam, choose the right response
The action you took matters more than how frightening the warning looked. The FTC's recovery guide for people who were scammed separates payment, personal information, account credentials, and device access because each calls for different steps. Use the closest situation below. If more than one applies, work through each relevant response, starting with any active remote access or financial transfer.
You called but shared nothing
End the call. You do not have to explain yourself or wait for permission to hang up. Do not accept a return call from the person who gave you the number. If you still believe your device has a problem, use the independently opened security app and an official support route that you find outside the warning. Calling by itself does not give a person remote access to your computer. It is the later request to install a remote tool, disclose a code, or grant control that changes the situation.
Think back to the call without blaming yourself. Did you read out a password, approval code, or card number? Did you install software or let someone control the screen? Did you authorize a charge? If the answers are no, the response can stay narrow: close the page, inspect the device through trusted tools if concerned, and disregard further contact. If you are uncertain, write down what you remember, then move to the section that matches the possible exposure. There is no benefit in treating every call as if every account was breached.
A file downloaded, but you did not open it
Leave the file unopened. If a browser download warning offers a way to keep a suspicious file anyway, do not override it. Google warns against ignoring a download warning or turning off protection in its troubleshooting guidance. A website's instruction to disable a safeguard is another reason to stop, not a necessary repair step.
Use the device's ordinary download or file controls to delete the unwanted file without opening it. If you want to check it first, Windows Security offers a custom scan for selected files or folders. Use your installed protection tool, rather than downloading a checker from the warning page. These are proportionate steps for the information you have; they are not a guarantee that a file was harmless.
If you are unsure whether the file opened, installed an app, or asked you to approve a profile or other device access, say so when seeking trusted help. Do not assume that every downloaded file is a completed installation, and do not claim that nothing ran when you cannot tell. On a work or school device, report the download to known IT staff and follow their procedure before deleting material they may need to examine.
You opened software, installed it, or granted remote access
Stop the session and end contact. If the other person may still control the device, disconnect it from the network while arranging help through a separate phone or device. Tell the trusted helper exactly what remote-access application or file you installed, if you know. Avoid logging into sensitive accounts on the affected device until you have assessed it. The FTC recommends updating protection, scanning, removing detected problems, and securing accounts after device access. Microsoft also advises removing scam-requested applications and considering a reset when needed. Describe the software and permissions to a trusted helper before deciding that removal alone has dealt with everything.
A scan is useful evidence, but a clean result is not a promise that every effect of remote access has been reversed. The next step depends on what was installed, what the person could see, and whether symptoms continue. A trusted technician or organizational IT team can help decide whether removal and a scan are enough or whether a more extensive recovery is appropriate. Keep the decision tied to the actual access. Ask the helper to explain what the proposed recovery will address and what remains uncertain, especially if the device held work information or sensitive accounts.
You shared a password or verification code
Go to the affected service through its own app or a known address and change the password. If you reused that password elsewhere, change it on those accounts as well. Turn on two-factor authentication where available, then review account security settings and recent activity for anything you do not recognize. If a scammer still has access to an account, use that service's official recovery process. Do these steps from a device you trust if you also gave remote access to the original computer.
The order matters. A new password entered into a device that someone else still controls may not solve the underlying problem. End the access first, then secure the account. If the code you disclosed was for a sign-in or money transfer, contact the relevant service promptly through a route you chose yourself. The warning's support number cannot validate whether your account is safe.
You paid or shared financial details
Contact the bank, card issuer, or payment provider directly using the number on your card, its app, or another known route. Say that a tech support scam may have involved the account or payment, ask whether a transaction can be stopped or reversed, and follow the institution's instructions to protect the account. The FTC says it is worth asking promptly about a refund or reversal even though recovery is not guaranteed. Do not negotiate another payment with the caller to “unlock” a refund.
The method you used affects the next steps. A card payment, bank transfer, payment app, gift card, and cryptocurrency transfer have different providers and possible remedies. Give the provider the time, amount, destination, and any receipt you have. Watch for new transactions and report ones you do not recognize. If a scammer says a refund was too large or asks you to move money to a “safe” account, end the conversation and confirm any actual account movement in your bank's own app or with the bank directly.
You shared identity information
Record precisely what you gave: a name and contact detail, account login, Social Security number, identity document, or other sensitive information. The risk and response vary with that list. If you gave a scammer your Social Security number and know it was misused, the FTC directs you to IdentityTheft.gov to report it and get a tailored recovery plan. If the number has not been used or you are unsure, follow IdentityTheft.gov's data-breach steps to help protect yourself. The Identity Theft Response Checklist can help you organize these actions; use the official route that fits your situation. Keep any contact with the bank, account provider, or identity-recovery service separate from the number in the warning.
You can report an attempted or completed tech support scam through the FTC's ReportFraud portal. A report is worthwhile even if you did not pay. Preserve the relevant facts you know, such as the phone number shown, the site or message that led to it, the approximate time, and what happened after contact. You do not have to keep the fraudulent page open to make that record. If a workplace device or account was involved, notify the organization's known security or IT contact as well.
Build a simple response habit for the next alert
Three questions can keep a surprise warning from making the decision for you. First, where is the message appearing? A browser tab, a website notification, and the security app you opened yourself are different sources. Second, what is it asking me to do? A number to call, a download to install, a command to paste, or a payment to make is a reason to stop. Third, what actually happened after I saw it? The answer tells you whether to close a page, change a browser permission, run a scan, secure an account, or contact a payment provider.
You can make the independent route easy to remember before another warning appears. Know where your device's security settings live. Keep the official support route for a device or service in your account materials rather than trusting a number presented during a scare. If you help a family member, agree that they can close an alarming page and call you or another trusted person first. A brief pause is useful because the warning's power comes from urgency, not from evidence it has shown you.
The same habit helps beyond fake security alerts. Cybersecurity Basics covers the everyday practices that make independent checking easier. If the incident began with a link you clicked in a message, What To Do If You Clicked a Scam Link offers a response focused on that starting point. Choose the guide that matches what happened rather than assuming that every alarming screen requires the same checklist.
For calm, practical explanations of new online scams and device-safety decisions, subscribe to Quantum Cyber AI updates. You do not need to memorize every scam design to use this habit. Know how to leave a warning and whom to contact independently; that gives you time to make the next decision.
Conclusion
A sudden security alert with a phone number is trying to make you act before you can check its claim. Do not call it. Close the page or block the website notification, then open your own security tools or trusted support channel to see whether there is a real problem. If you only saw the warning, that first response may be enough. If you also installed software, gave remote access, shared information, or paid, take the matching recovery steps promptly. The screen may be loud and persuasive, but it does not get to choose your technician, your payment method, or your next click.
FAQ
Does a security pop-up mean my computer has a virus?
No. A page can claim that a virus was found without proving it. Close the page and check with the security app you open yourself if you are concerned. If unwanted tabs, redirects, or unfamiliar software keep appearing, investigate those symptoms rather than assuming the original page was the whole problem. The right conclusion comes from an independent check and what you actually did after seeing the warning.
What if I cannot close the warning?
Use the browser's tab or window control rather than a button inside the message. Leave full screen if necessary, close the browser, and restart the device if the browser will not close normally. When reopening, avoid restoring the suspicious tab. If the behavior continues, ask a trusted technician or your organization's IT team for help and explain what you observed.
Can a fake security alert appear when the browser is closed?
Yes, a website notification can appear outside a page, and some browsers can display permitted site notifications while their main window is closed. Do not open the alert to inspect it. Open browser settings yourself, find the notification permissions for websites, and block the unfamiliar sender. If the alert continues after that or other browser behavior changes, check for unwanted extensions or software and use your trusted security tool.
I called the number but did not share anything. What should I do?
Hang up and avoid return calls. Review whether you disclosed any password, code, payment details, or personal information, or installed a remote-access tool. If none of those happened, a phone conversation alone is not the same as giving computer access. Close the warning and verify any remaining device concern through your own security app or an independently found support channel.
Should I ignore every security warning?
No. Ignore the instructions of the suspicious message, especially its phone number, but check the underlying concern through an independent route. Open the installed security app or device settings yourself and review any actual finding. That distinction lets you respond to a real device problem without trusting a page or notification that may be impersonating one.