Cybersecurity is no longer just a technical field. It is a frontline defense for global stability, national infrastructure, and digital trust. But as cyber threats grow in complexity and frequency, a quiet crisis is brewing within the industry itself. ISC2’s 2023 study estimated a global cybersecurity staffing gap of about 4 million people; that was not a count of advertised vacancies. CyberSeek’s June 2023 release counted 663,434 U.S. cybersecurity job postings during May 2022–April 2023 and estimated an existing workforce of about 1.1 million. And this isn’t just a numbers game. This is a problem of perspective.
Diversity in cybersecurity is more than a moral imperative. It is a foundational requirement for effective defense. Teams need enough skills and experience to recognize critical warning signs. In Fortinet’s 2024 skills-gap survey, 87% of respondents said a breach in the previous year was attributable in part to a lack of cybersecurity skills. The survey covered more than 1,850 IT and cybersecurity decision-makers in 29 countries; it did not measure demographic diversity’s effect on breaches.
While the broader conversation about DEI in tech has gained momentum, the cybersecurity workforce remains disproportionately male and drawn from traditional pipelines. Narrow recruitment can leave relevant experience untapped. In a February 2023 forecast, Gartner predicted that by 2025, a lack of talent or human failure would be responsible for over half of significant cybersecurity incidents.
This blog explores five critical areas where the lack of inclusive cybersecurity teams undermines our defenses. It’s not simply about fairness or optics. Cybersecurity workforce diversity affects every layer of protection. It influences how we identify threats and how we build resilient systems.
Whether you’re a CISO, policymaker, hiring manager, or engineer, the path to stronger security begins by addressing who gets to participate. Let’s examine how this crisis unfolded and why solving it must start with embracing diversity in cybersecurity.
The Cybersecurity Crisis No One Talks About
Global Shortage Meets Growing Threats
The cybersecurity talent gap has been building for years, but the current scale is staggering. In 2021, Cybersecurity Ventures forecast 3.5 million unfilled cybersecurity positions worldwide for 2025. This shortage affects both private companies and national governments, weakening response times and overwhelming existing staff.
In the U.S., demand is equally intense. That June 2023 posting total shows substantial recruitment demand, but it is not a snapshot of 663,434 simultaneously unfilled jobs. These gaps are not theoretical. They translate directly into vulnerability.
The situation is poised to get worse. A tool is only as good as the hands using it. A team is only as strong as its ability to anticipate the full range of threats it might face. As AI-driven attacks grow more advanced, inclusive cybersecurity teams will be vital to keep pace. You can explore this further in AI Cybersecurity Arms Race: 7 Alarming Signs Hackers Are Winning for deeper insight.
Why the Talent Crisis Is Structural, Not Just Technical
Part of the problem lies in how the industry thinks about readiness. Cybersecurity workforce diversity is limited not just by the size of the talent pool but by how we train and recruit people. Universities still prioritize computer science degrees over alternative pathways. Certifications like CISSP or GIAC, while valuable, can become gatekeepers rather than on-ramps.
Moreover, most hiring practices are misaligned with the evolving threat landscape. Too many job postings require four-year degrees, five years of experience, and elite certifications, yet they offer no training or entry-level flexibility. These criteria disproportionately exclude women, people of color, and those from lower-income or nontraditional backgrounds.
The result is a narrow workforce funnel at a time when we need wide access. Fixing the cybersecurity talent gap will require broadening who we recruit, how we train them, and what traits we value in building inclusive cybersecurity teams.
The Role of Burnout and Attrition
Even for those inside the field, the pressures are mounting. Understaffed security operations centers (SOCs), 24/7 incident response expectations, and the psychological weight of defending against nation-state attacks have pushed many professionals to burnout. According to recent reports, high attrition rates are now compounding the workforce shortage across both public and private sectors.
This environment is especially punishing for underrepresented employees who often lack peer support or mentorship within male-dominated teams. When professionals from diverse backgrounds do enter the field, they frequently encounter biased evaluation, cultural exclusion, or unclear advancement paths. Retaining diverse talent in cybersecurity is just as urgent as recruiting it.
The combined effect of global demand, flawed pipelines, and burnout creates a vacuum. And into that vacuum, attackers step. Without systemic change, the shortage won’t just persist. It will become a permanent vulnerability.
How Lack of Diversity Weakens Cyber Defenses
Narrow Thinking in Homogenous Teams
The absence of diversity in cybersecurity is not only an issue of equity. It can weaken our ability to respond to threats. Homogenous teams, no matter how skilled, can share assumptions, risk perceptions, and mental models. This can create blind spots in how threats are interpreted and addressed. The World Economic Forum’s July 2024 workforce article recommended recruiting underrepresented groups and broadening talent pools; it did not establish a direct link between under-representation and failures in breach response planning.
In practice, this means threat scenarios can be shaped by a limited set of lived experiences. For example, phishing emails designed to exploit cultural or linguistic nuances may go undetected if no one on the team recognizes them as suspicious. Inclusive cybersecurity teams can draw on varied experience to recognize social engineering tactics, misinformation campaigns, or platform misuse that target diverse populations.
In a 2020 WIRED opinion essay, Sylvia Acevedo argued that cybersecurity design can overlook the safety needs of women and children. Her argument supports examining whose needs are represented, but it was not a performance experiment showing measurably stronger security systems. Broader representation can widen the search for technical and behavioral vulnerabilities.
Gendered Hiring Biases and Missed Potential
Hiring criteria deserve scrutiny because they shape which skills an organization notices. A study published in 2024, using a 2019 survey of cybersecurity professionals, found differences in the non-technical skills female and non-female respondents prioritized when recruiting junior staff. It did not test hiring-panel outcomes or preferences for technical certifications. While technical acumen is essential, cybersecurity also demands creative thinking, adaptability, and communication. These traits are harder to quantify but vital in a crisis.
A narrow set of hiring criteria can overlook candidates who might bring useful experience or transferable skills; the survey does not show which applicants were excluded. GCF and BCG’s 2024 report estimated that women made up 24% of the global cybersecurity workforce. Employers should examine whether their assessment methods recognize those abilities as well as familiar credentials when evaluating cybersecurity workforce diversity.
Failure to Address Vulnerabilities That Target Marginalized Groups
The consequences go beyond hiring. Design and testing should consider how different communities may encounter a service or be targeted through it. Varied experience can help a team ask whose needs a proposed protection might miss.
For instance, reviewing a bilingual scam scenario calls for knowledge of its language and cultural cues. Security decisions that use algorithms also warrant questions about surveillance or profiling risks for different groups. Inclusive cybersecurity teams can bring additional perspectives to that review, but representation alone does not ensure those risks are recognized or corrected.
Colleagues should have room to challenge assumptions before they become product features. Experiences with how a service is used can inform questions about harm, access and misuse. Those questions still need investigation, testing and follow-through.
Investing in diversity in cybersecurity can widen the experiences available to a team. Organizations need to turn those perspectives into explicit scenarios, shared threat intelligence and tested defensive decisions; demographic representation by itself does not establish greater resilience or precision.
Understanding how diversity impacts threat modeling leads naturally to the question of what happens when representation is missing from the detection process itself. That’s where we turn next.
Why Representation Matters in Threat Detection
How Varied Experience Can Inform Threat Modeling
Diversity in cybersecurity can inform how a team anticipates threats. Different professional, cultural and personal experiences may suggest additional scenarios or questions. Whether those ideas improve a threat model depends on how the team examines evidence and tests its assumptions.
This isn’t just about demographic balance. It is about how teams examine risk. Colleagues need room to challenge assumptions that could lead to overlooked risks. Whether modeling ransomware behavior, predicting phishing evolution, or testing AI-driven scams, cybersecurity workforce diversity can broaden the scope of defensive thinking.
Security planning is only as effective as the team’s ability to imagine the attacker’s next move. Varied backgrounds and cognitive diversity can help a team consider scenarios it might otherwise miss. Red team exercises and simulated breaches give teams a way to test those scenarios and expose gaps in their own defenses.
Skills Gap vs. Hiring Gap
While much of the public conversation focuses on a numeric talent shortage, the real crisis may lie in the mismatch between who is hired and what skills are actually needed. The ISC2 2024 Cybersecurity Workforce Study found that 64% of respondents believed skills gaps could have a greater negative impact than staffing shortages.
This means that even when teams are fully staffed on paper, they can still be ineffective in practice. Overreliance on candidates with similar training or backgrounds leads to intellectual monocultures. Hiring managers often look for familiar credentials or experiences, overlooking transferable skills from candidates outside traditional pipelines. As a result, cybersecurity talent gaps are deepened by hiring processes that fail to prioritize cognitive diversity and lived experience.
DEI in tech initiatives can support looking beyond familiar credentials to abilities such as pattern recognition, communication under stress and cross-cultural awareness. Hiring and development should connect those abilities to the work a role requires, rather than assume that a broader applicant pool automatically produces more resilient detection.
Using Different Perspectives to Examine Threats
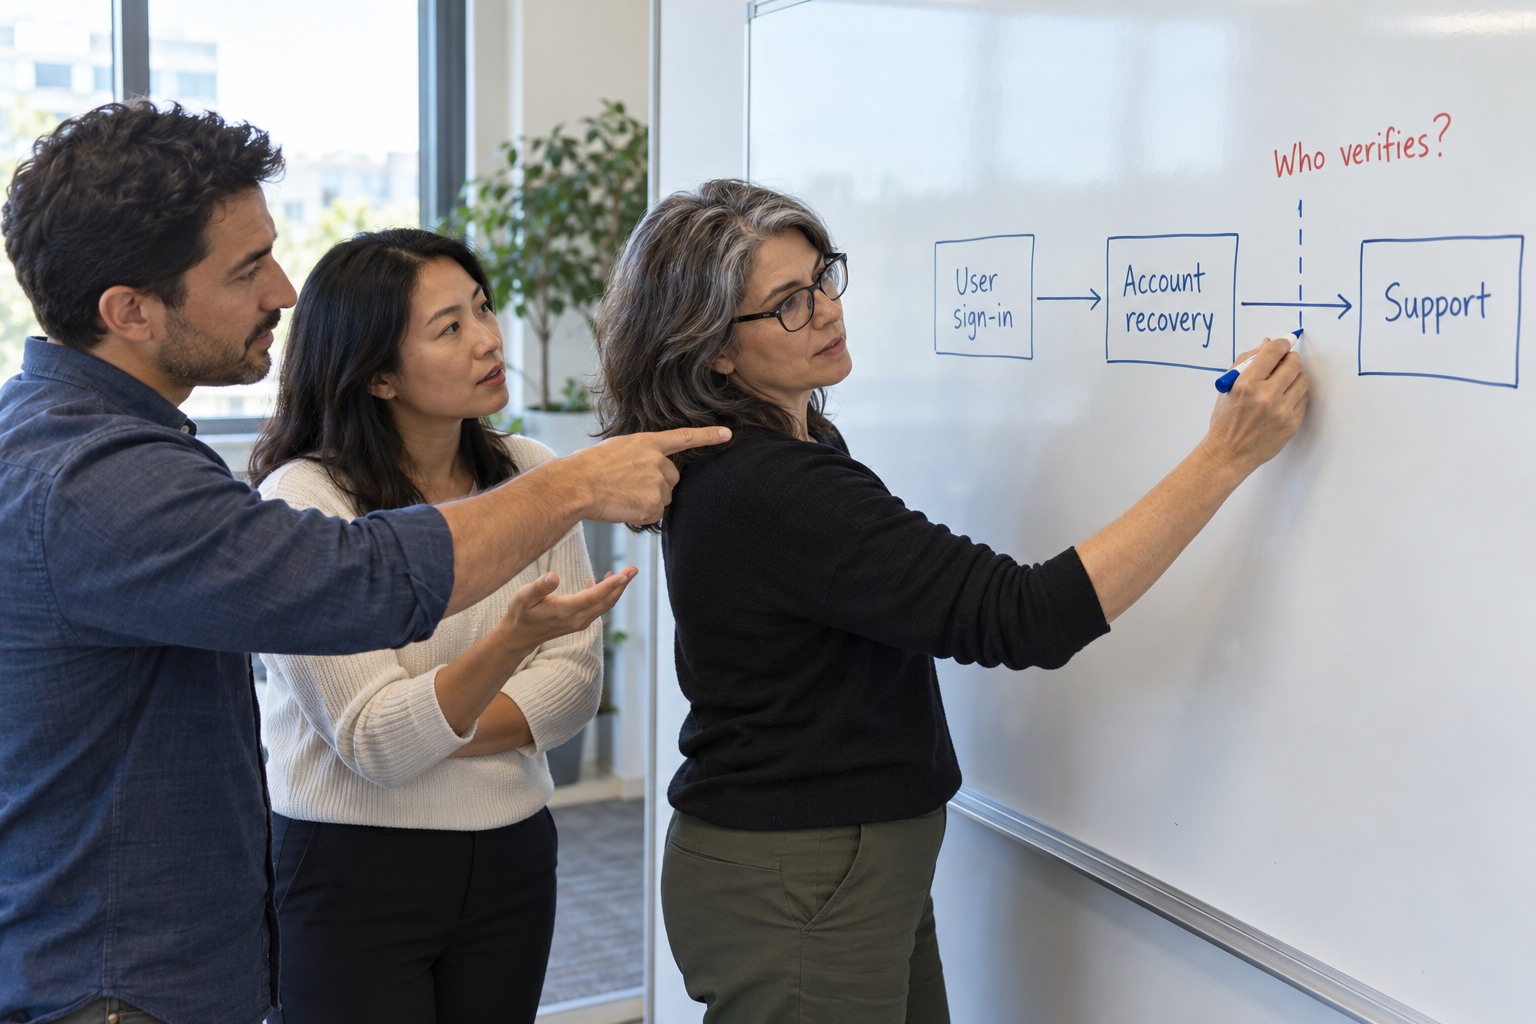
A case for greater representation is the opportunity to examine threats from more than one perspective. Someone familiar with a particular language, service or community may add context to a social-engineering scenario or an unusual technical signal. The team still has to investigate whether that interpretation is supported.
North Korean IT-worker fraud illustrates why recruitment checks need context: applicants can use stolen identities, false work histories and remote-access arrangements to misrepresent who and where they are. The FBI’s January 2025 advisory described companies being deceived into hiring such workers. That case does not establish that a team’s demographic composition caused a failure to detect them. Our article on North Korean deepfake job scams provides related reading.
Inclusive cybersecurity teams can ask how irregular user behavior, AI-generated phishing lures or culturally coded messages might be interpreted differently. Reviewing those possibilities is useful work, but the examples do not establish that demographic composition makes a team more likely to detect an attack.
As we shift focus from threat modeling to workforce access, it becomes clear that the pipeline feeding the industry is just as flawed as the teams themselves. The next section explores who gets left out of cybersecurity, and why it matters.
Barriers to Entry: Who Gets Left Out of Cybersecurity?
Unrealistic Entry-Level Requirements
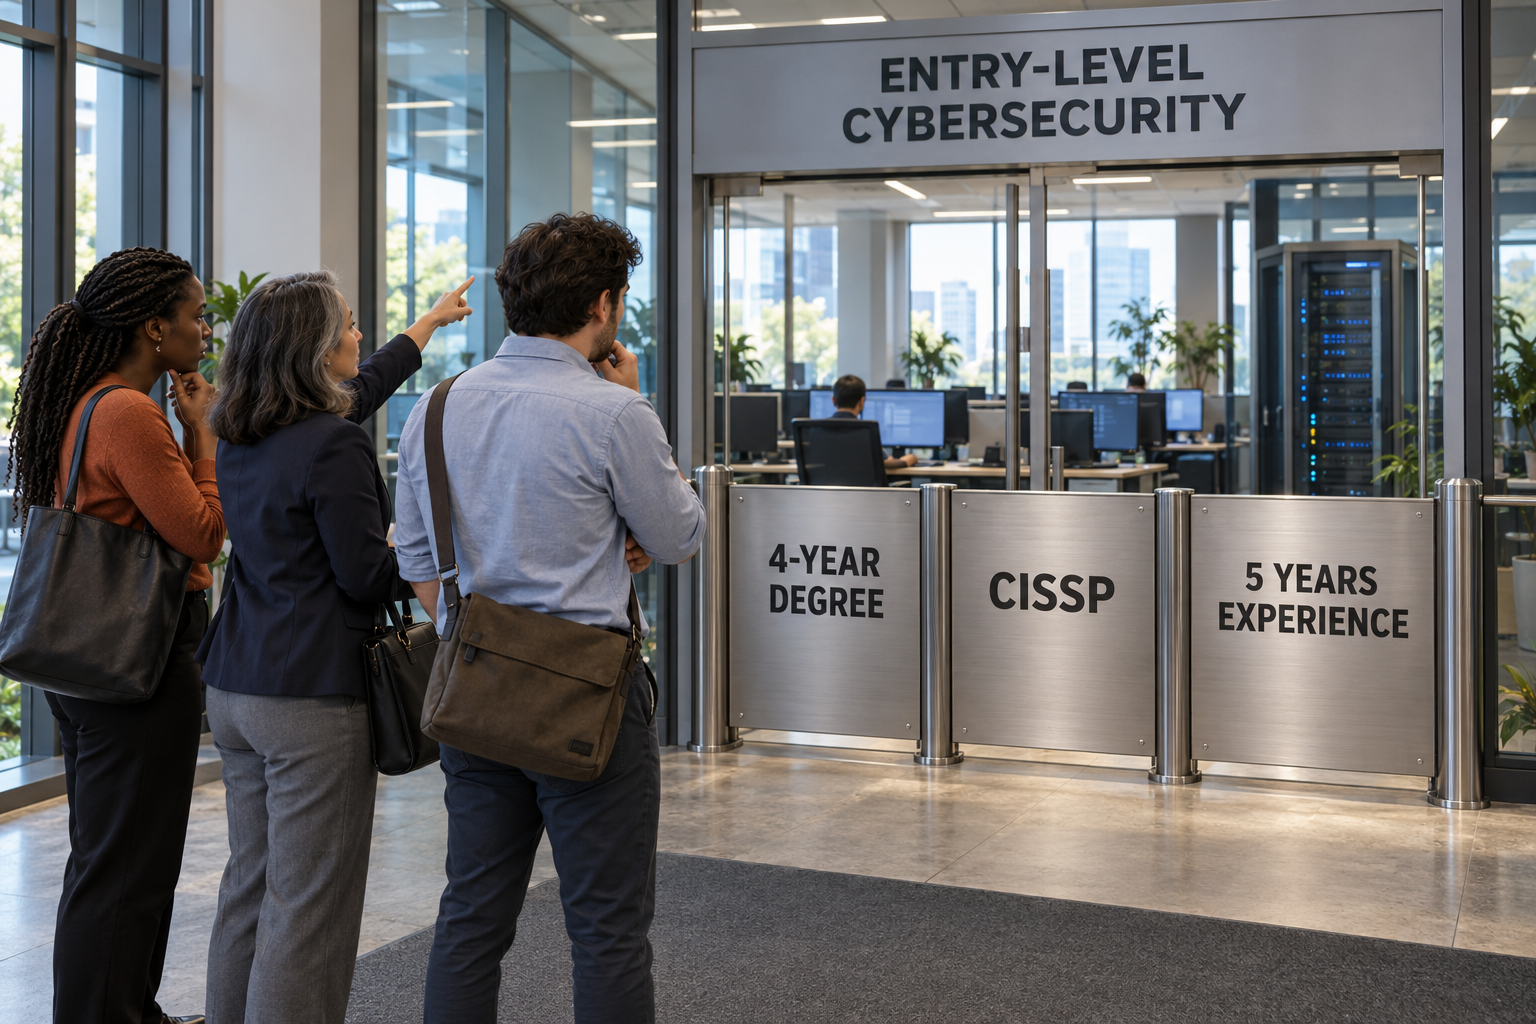
One of the most significant barriers to diversity in cybersecurity lies in how organizations define “entry-level.” According to the 2025 ISC2 Hiring Trends Report, 34% of surveyed hiring managers required CISSP for entry-level roles and 33% for junior-level roles, although the certification normally requires five years of qualifying experience. These inflated expectations immediately disqualify many talented individuals from nontraditional backgrounds who could otherwise contribute valuable skills to inclusive cybersecurity teams.
These unrealistic requirements disproportionately affect underrepresented groups. Many first-generation professionals, women, and people of color face systemic barriers to earning costly certifications or gaining early access to corporate internships. The result is a cybersecurity workforce diversity problem that replicates itself at every level. By requiring “industry ready” applicants for what should be training-focused roles, organizations undermine their own talent pipelines.
This approach also ignores the urgency of the cybersecurity talent gap. Rather than upskilling promising candidates, the industry continues to filter out large swaths of potential contributors based on outdated credential expectations.
Biased Job Postings and Recruitment Channels
Another major obstacle is how cybersecurity jobs are marketed and shared. A recent Wall Street Journal report documented how employers often demand vague or excessive experience requirements, paired with minimal guidance on training or advancement. This ambiguity discourages capable applicants who do not see themselves represented or supported in the field.
Many job descriptions are unintentionally biased. Language like “rockstar,” “ninja,” or “expert-level” often deters women or applicants from outside the traditional tech ecosystem. Meanwhile, companies continue to rely on recruiting from a small circle of elite universities or through networks that exclude historically underrepresented populations.
To improve DEI in tech, organizations need to write inclusive job postings, audit their language, and actively expand where they search for talent. Cybersecurity workforce diversity will only increase if access points are designed to accommodate more than one kind of applicant.
The Education-to-Workforce Gap
A broader issue is the disconnect between cybersecurity education and hiring practices. While universities and community colleges have ramped up cybersecurity programs, many graduates are unable to land jobs. The issue isn’t lack of technical knowledge. It’s that employers still default to candidates with “real-world” experience, which is rarely accessible to students from marginalized backgrounds.
Underserved schools often lack industry partnerships, updated labs, or mentorship programs that would make cybersecurity careers more accessible. This limits exposure to the field long before hiring even begins. Meanwhile, bootcamps and certification programs that claim to fill the gap often carry high costs or offer inconsistent outcomes.
Closing the cybersecurity talent gap requires addressing the systemic exclusion embedded in education and recruitment systems. Expanding apprenticeships, creating formal bridges between schools and employers, and removing unnecessary credential barriers are essential steps toward building inclusive cybersecurity teams.
When hiring processes prioritize exclusivity over potential, everyone loses. The next section explores how forward-thinking organizations are actively reversing this trend and investing in the future of cybersecurity through inclusion.
Building Inclusive Security Teams: What Actually Works
Invest in Apprenticeships and Internships
One of the most effective strategies for increasing diversity in cybersecurity is to open structured pathways for entry-level talent. In ISC2’s 2025 hiring survey, 55% of respondents used internships and 46% used apprenticeships to identify or recruit early-career cybersecurity talent. These programs allow employers to recruit from a broader pool, including students from community colleges, career changers, and individuals without traditional credentials.
Apprenticeships offer a way to close the cybersecurity talent gap while embedding candidates into real-world environments. They also reduce the reliance on high-cost certifications that often serve as barriers to entry. Inclusive cybersecurity teams are built when organizations prioritize hands-on learning over pedigree. This shift supports cybersecurity workforce diversity by providing equitable access to industry experience, particularly for those overlooked by conventional hiring filters.
Internship-to-hire pipelines are especially powerful when combined with mentorship and clear advancement opportunities. When early-career professionals are supported beyond the hiring phase, retention improves and the entire organization benefits from a more resilient talent base.
Mentorship, Conferences, and Community Support
Formal mentorship programs are another key investment in building inclusive cybersecurity teams. These programs give underrepresented professionals guidance, career support, and the confidence to persist in challenging environments. Mentorship also helps reduce attrition by addressing common barriers such as isolation, cultural disconnect, and lack of advancement pathways.
Organizations like Women in CyberSecurity (WiCyS) have created spaces where emerging professionals can network, learn, and gain visibility. Their annual conference attracted more than 1,900 in-person participants in 2024, reflecting a growing demand for supportive ecosystems outside of traditional hiring channels.
These networks act as both recruiting hubs and retention engines. When companies partner with organizations that center DEI in tech, they gain access to talent that is motivated, community-connected, and invested in solving real cybersecurity challenges.
Hiring for Potential, Not Just Credentials
The final shift that defines high-functioning, inclusive cybersecurity teams is a hiring strategy centered on potential. ISC2’s 2025 hiring report ranked teamwork, problem-solving and analytical thinking ahead of data security and cloud security among the most valued skills for early-career hires.
This change reflects a growing recognition that effective security is a team sport. It requires people who can think under pressure, translate complex threats into action, and adapt quickly to new information. These are skills found across many disciplines and life experiences, not just in narrow technical tracks.
By prioritizing adaptability and collaboration over certification checklists, organizations unlock a wider, more diverse pool of capable professionals. This approach addresses the cybersecurity talent gap while simultaneously strengthening the team’s resilience and creativity.
Diversity in cybersecurity is not a side initiative. It is a core security strategy. And as the nature of cyber threats evolves, the future of resilience will depend on how well we embed that truth into national policy and organizational culture.
The Future of Cyber Resilience is Inclusive
National Policy and Workforce Commitments
In July 2023, the Biden administration’s National Cyber Workforce and Education Strategy called for skills-based hiring, broader access to cyber education and a more diverse workforce. Its announcement included apprenticeship and training commitments from government and other partners. It also described the Cybersecurity and Infrastructure Security Agency’s (CISA) partnerships with groups including Girl Scouts, Girls Who Code and Women in CyberSecurity to broaden participation in the field.
This national focus acknowledges what the data makes clear. Increasing cybersecurity workforce diversity is a strategic move. When more people from underrepresented groups have access to training, mentorship, and real career opportunities, the national talent pipeline becomes stronger, broader, and more adaptable to future threats. However, recent proposals to weaken digital identity protections like those explored in this article could undermine that progress and introduce new cybersecurity vulnerabilities.
Corporate Case Studies: Cisco, IBM, United Airlines
Cisco has supported apprenticeships and alternative learning pathways. In November 2022, the company announced support for national apprenticeship standards and said Cisco Talos would use them to launch a cybersecurity apprenticeship program.
IBM’s SkillsBuild platform offers free cybersecurity learning. Its July 2024 announcement described a cybersecurity certificate developed with community colleges, providing another route for learners to develop relevant skills.
Meanwhile, United Airlines described investing in continuous education, mentorship and nontraditional career development in SANS’s 2025 workforce research.
These examples illustrate approaches to widening access and supporting professional development. Organizations should measure whether their own programs improve retention, progression and security performance rather than assuming those outcomes.
Federal Hiring and the Diversity Gap
Representation gaps extend across the federal workforce. A 2023 GAO report found that women and employees from historically disadvantaged racial or ethnic groups remained underrepresented in the Department of Defense civilian workforce compared with the broader federal civilian workforce, especially at senior grades. The report did not isolate cybersecurity roles, but its findings reinforce the need to examine who gets to hold technical positions and shape their priorities.
Civil service reform efforts must include better support for early-career hires, more flexible pathways into GS roles, and deliberate outreach to underrepresented groups. Security clearances and hiring freezes continue to be major chokepoints. Until these barriers are addressed, the cybersecurity workforce will remain skewed toward those who already had access.
From Talent Pipeline to National Security Strategy
The stakes are only getting higher. As AI-enhanced threats evolve and cyberattacks target critical infrastructure, a narrow and under-resourced talent pipeline poses an unacceptable national security risk. Inclusive cybersecurity teams offer a wider set of lenses for identifying weak spots, managing complexity, and mounting effective defenses.
Resilience starts with people. A cybersecurity strategy that includes only those with elite degrees or traditional experience will fail to keep up with an adversary that is constantly adapting. To future-proof American digital infrastructure, diversity in cybersecurity must be viewed as a core requirement, on par with encryption standards or access controls.
By connecting workforce diversity to national preparedness, we can finally move beyond rhetoric and toward measurable action. And that action begins with recognizing inclusion as essential to survival in an AI-driven threat landscape.
Conclusion
Cybersecurity is no longer a numbers game. As we have seen, diversity in cybersecurity is both a moral imperative and a strategic necessity. The estimated global staffing gap reported in 2023 will only worsen if we continue to recruit from a narrow pipeline. Without intentional efforts to build inclusive cybersecurity teams, organizations will miss critical insights, overlook emerging threats, and leave entire communities vulnerable.
Going forward, inclusive cybersecurity teams must be embedded across every stage of the security lifecycle. Policymakers need to tie funding and apprenticeships to diversity metrics. Employers must prioritize mentorship, flexible job requirements, and pipeline partnerships to reduce barriers. Educators should collaborate with industry to ensure curriculum aligns with real-world DEI in tech needs, not just theoretical learning.
Generative AI, deepfakes, and global cyber warfare are already redefining the threat landscape. Teams that draw on a wide range of perspectives can bring more experience to anticipating adaptive attacks and responding effectively. For professionals, the message is clear: investing in cybersecurity workforce diversity is no longer optional. It is an essential component of national and organizational resilience.
Policy leaders, CISOs, and recruiters must commit today to shifting hiring criteria, funding inclusive training programs, and tracking long-term retention of underrepresented talent. The time to act is now. Subscribe to the Quantum Cyber AI Brief to stay ahead of evolving threats, trends in DEI-driven hiring, and strategic insights that matter.
Ultimately, the future of cyber defense will belong to teams that mirror the complexity of the global ecosystem they protect. Higher resilience, wider threat awareness, and stronger response capabilities depend on diversity in cybersecurity, not just in policy statements but in everyday practice and purpose.
Key Takeaways
- ISC2 estimated a global cybersecurity staffing gap of about 4 million people in 2023.
- A narrow range of experience can leave blind spots in threat planning and response.
- Hiring practices often exclude underrepresented talent due to unrealistic entry barriers.
- Inclusive cybersecurity teams can bring broader experience to threat modeling and incident response.
- Practical solutions like mentorship, apprenticeships, and skills-based hiring are already working.
- National resilience requires intentional investments in cybersecurity workforce diversity.
FAQ
Q1: Why is diversity in cybersecurity considered a security issue, not just an HR concern?
A narrow range of experience can leave blind spots around social engineering, asymmetric attacks, and culturally specific threat vectors. Broadening participation can bring additional perspectives to threat detection and response.
Q2: How do staffing shortages differ from skills gaps?
A staffing shortage concerns how many people a team needs; a skills gap concerns the capabilities it lacks, including on a fully staffed team. ISC2’s June 2025 hiring report found that early-career roles were relatively quick to fill compared with more senior roles. That does not establish which roles suffer most overall. Early-career hiring, supervised work and training can help employers develop needed capabilities without expecting new entrants to arrive with senior-level experience.
Q3: Do diverse cybersecurity teams actually perform better?
Varied perspectives can help teams challenge assumptions and consider more threat scenarios. The sources discussed here do not establish that diverse teams consistently outperform others in red team exercises or breach response. Organizations should assess their own team’s performance rather than assume a guaranteed gain.
Q4: Are any companies taking real action to fix this?
Yes. Cisco has supported cybersecurity apprenticeship pathways, IBM offers free learning through SkillsBuild, and United Airlines has described mentorship and nontraditional career development. These are concrete approaches to broadening access and supporting professional development.
Q5: How can someone from a nontraditional background enter the field?
Through community college courses, cybersecurity bootcamps, apprenticeships, or scholarships from groups like Women in CyberSecurity (WiCyS) and ISC2. Many companies now accept transferable skills and offer on-the-job training.