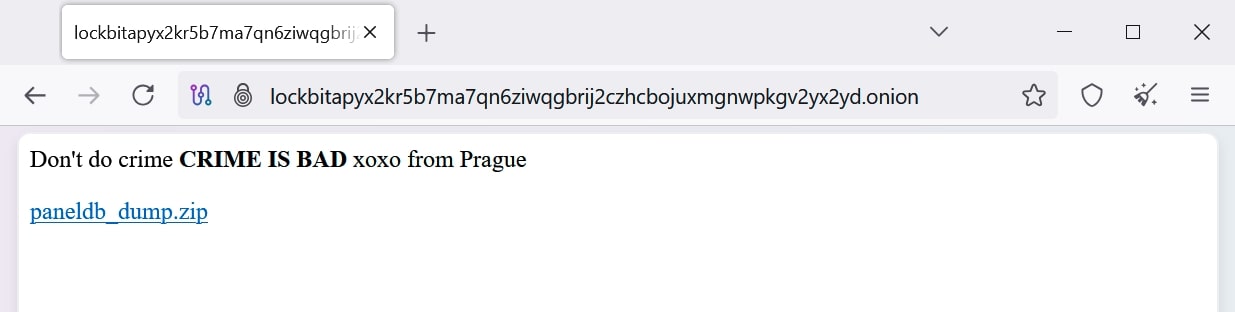
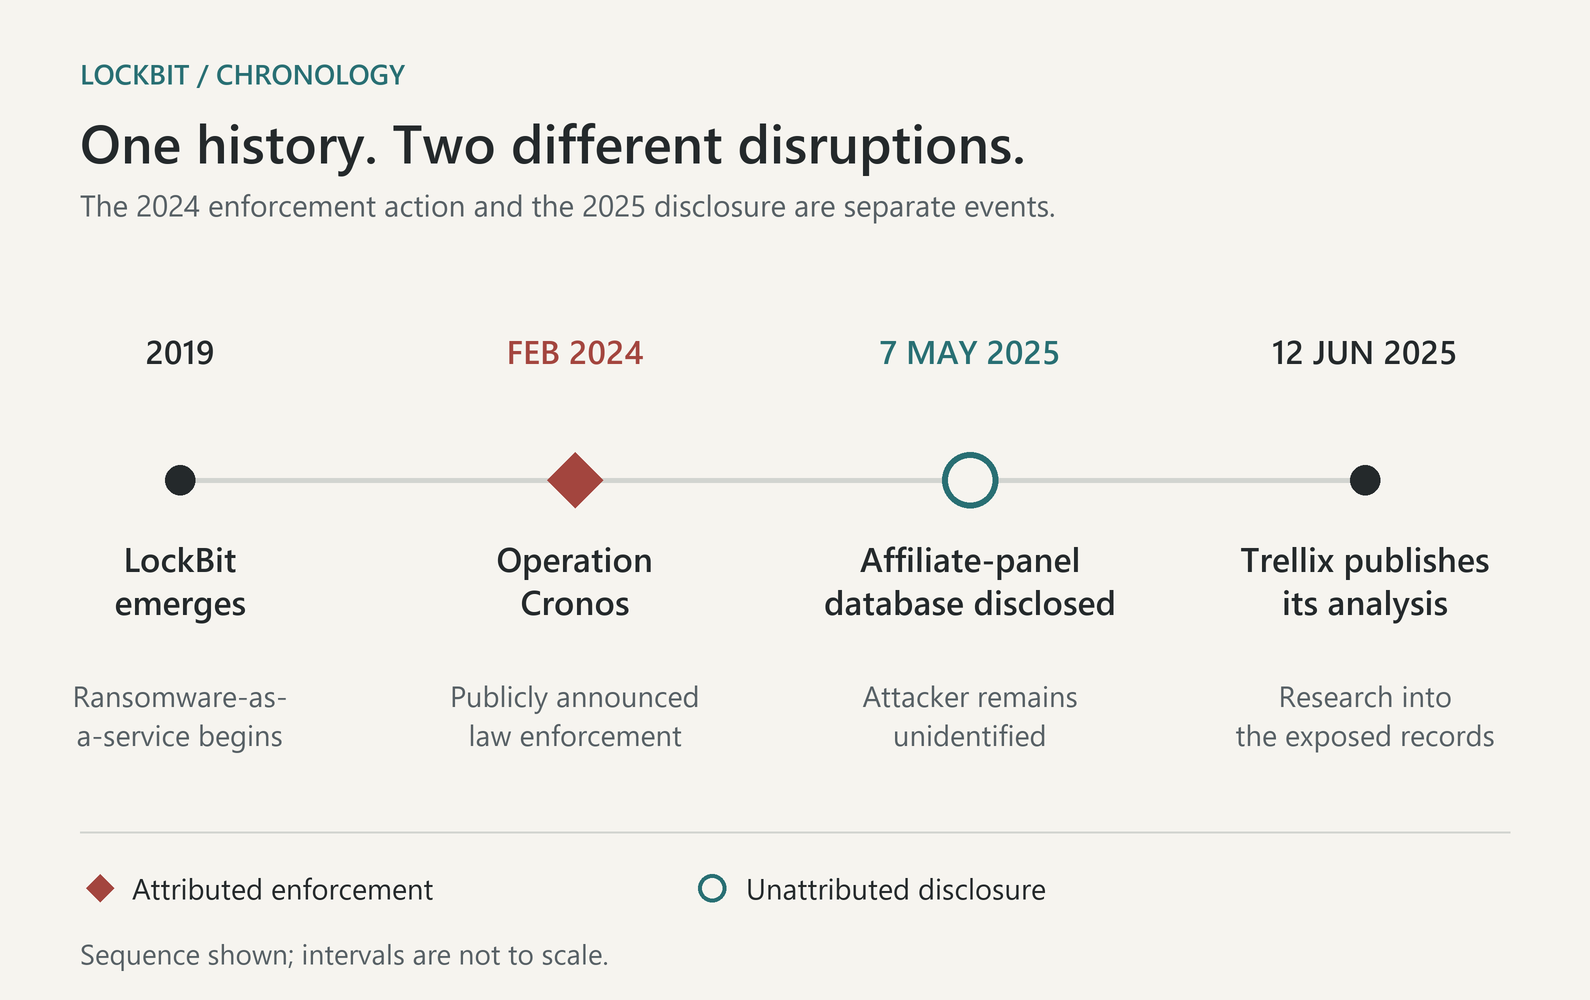
On May 7, 2025, the LockBit ransomware gang, one of the most feared cybercriminal groups, had an affiliate admin panel hacked and defaced by an unknown actor. As Trellix’s analysis of the exposed database describes, the panel displayed the taunt “Don’t do crime. CRIME IS BAD. xoxo from Prague.” The attacker released internal records, but their identity and method of access remained unresolved. The leak was separate from the publicly announced Operation Cronos action of February 2024.
LockBit had survived before. After a global enforcement campaign in 2024, it attempted to rebuild. But the National Crime Agency’s May 2024 assessment described a reduced operation and inflated victim claims, not an established return to first place. The May 2025 leak was another setback. It exposed internal operations without establishing that the group had finally collapsed.
What made this breach distinctive was its anonymity. Instead of an official announcement identifying the investigators responsible, an unknown actor released database records concerning Bitcoin addresses, build configurations, negotiations and panel users. That exposure raised questions about LockBit’s ability to protect the people using its platform. It did not, by itself, show how many affiliates left or whether the operation had ended.
For cybersecurity defenders and analysts, the implications are serious. This was more than a breach. It was a warning: even the most hardened ransomware-as-a-service syndicates can implode from betrayal, sabotage, or reputational collapse. In today’s cybercrime economy, credibility is survival.
This article unpacks the breach, the leak, possible motives, and what it reveals about the growing instability of ransomware networks.
Key Takeaways
- The LockBit ransomware hack exposed internal records from one ransomware service, including account details, negotiation messages, cryptocurrency addresses, and build configurations.
- The ransomware affiliate leak created risks to secrecy and trust, but did not establish the claimed mass departure of affiliates or closure of LockBit.
- The attacker’s identity was unresolved. The May disclosure was separate from the publicly announced February 2024 Operation Cronos action; the message alone does not establish who was responsible.
- The LockBit data breach shows why credibility matters: exposing a service’s records can challenge the assurances it gives affiliates, alongside the technical damage of a compromise.
- Ransomware groups could tighten access or separate operations after an exposure, but this incident does not prove that they did so or predict how attacks would change.
- For defenders, the leak provides rare intel into ransomware operations, offering valuable insight for attribution, prevention, and policy action.
What Is LockBit and Why It Matters
LockBit didn’t begin as a dominant force. When it emerged in 2019, it was just one of many ransomware-as-a-service (RaaS) outfits offering encryption tools for hire. Over time, it became one of the most aggressive and organized ransomware syndicates in the world. The June 2023 joint CISA/FBI advisory identified LockBit as the most deployed ransomware variant in 2022. Its prominence made both its attacks and attempts to disrupt it important to defenders.
LockBit’s success came from its scale and strategy. It perfected the affiliate model, enlisting cybercriminals to deploy its tools in exchange for a cut of each ransom. This allowed it to grow rapidly without managing each attack directly. As a result, the LockBit ransomware hack carries implications beyond a single group. It exposed structural flaws in a business model built on shared trust and decentralized execution.
LockBit’s Origins and Rise
LockBit was originally branded as ABCD ransomware. It rebranded and evolved, integrating faster encryption and self-spreading features. By the time LockBit 2.0 and 3.0 rolled out, it had become a professional-grade RaaS platform with leak sites, affiliate support, and payloads for Windows, Linux, and VMware. Its adaptability helped it survive takedowns that eliminated other groups.
The LockBit ransomware hack showed that even a prominent operation could lose control of sensitive internal records. It was not the first time a top-tier ransomware gang had looked vulnerable: the earlier enforcement action had already demonstrated that. The incident also showed why other hacked ransomware gangs relying on secrecy and compartmentalization face similar risks.
Victim Impact and Financial Damage
LockBit’s financial footprint was massive. The June 2023 joint advisory put U.S. ransom payments to LockBit at approximately $91 million since January 2020. Its targets included hospitals, universities, manufacturers, and government agencies. The damage extended beyond a ransom demand: disrupted services, exposed information and recovery costs could continue long after an attack. That history explains why intelligence about the group mattered to defenders.
That reach made the LockBit data breach an unusual and valuable intelligence event. It exposed names, negotiations, affiliate behavior, and backend infrastructure. This kind of leak gives defenders a rare view into the mechanics of ransomware and how to counter it.
Critical Infrastructure at Risk
LockBit affiliates haven’t focused solely on soft targets. They have disrupted healthcare, education and public services. In December 2022, a LockBit affiliate attacked Toronto’s Hospital for Sick Children, known as SickKids, in Canada. The hospital’s January 2023 recovery statement described the restoration of priority systems and an offered decryptor. In 2023, LockBit also disrupted the UK’s Royal Mail. These attacks weren’t just financial blows. They interfered with essential services.
Even after past takedown efforts, LockBit proved resilient. It relocated infrastructure and shifted domains. The 2025 breach exposed further weaknesses in an operation already damaged by enforcement.
The next section explores what was exposed through LockBit’s affiliate panel and what remained unknown about the intrusion.
The Hack That Exposed LockBit
On May 7, 2025, LockBit was hacked and defaced by an unknown actor. For a group that had survived global law enforcement campaigns and built a reputation on resilience, this breach was different. Someone infiltrated its admin systems, leaked a cache of internal data, and posted a mocking message: “Don’t do crime. CRIME IS BAD. xoxo from Prague.”
The public presentation differed from Operation Cronos, the coordinated enforcement action announced in February 2024. The May leak appeared as an anonymous defacement and database release. That difference is observable; the attacker’s affiliation is not. A rival, insider, independent actor or government-linked operation could not be distinguished simply from the taunt.
Visitors to the affected panel encountered a defaced page and a link to an archive titled paneldb_dump.zip. Its contents were more significant than a changed homepage: they included records from the backend database. Access to those records demonstrated a compromise, but did not establish which vulnerability or credential had made it possible.
Trellix assessed with high confidence that the database originated from LockBit’s affiliate admin panel. That is an authenticity assessment, not attribution. Neither the presence of plaintext passwords nor the detailed operational records establishes that reused credentials or an insider caused the breach. The distinction matters: a visible security weakness is not automatically the explanation for an intrusion.
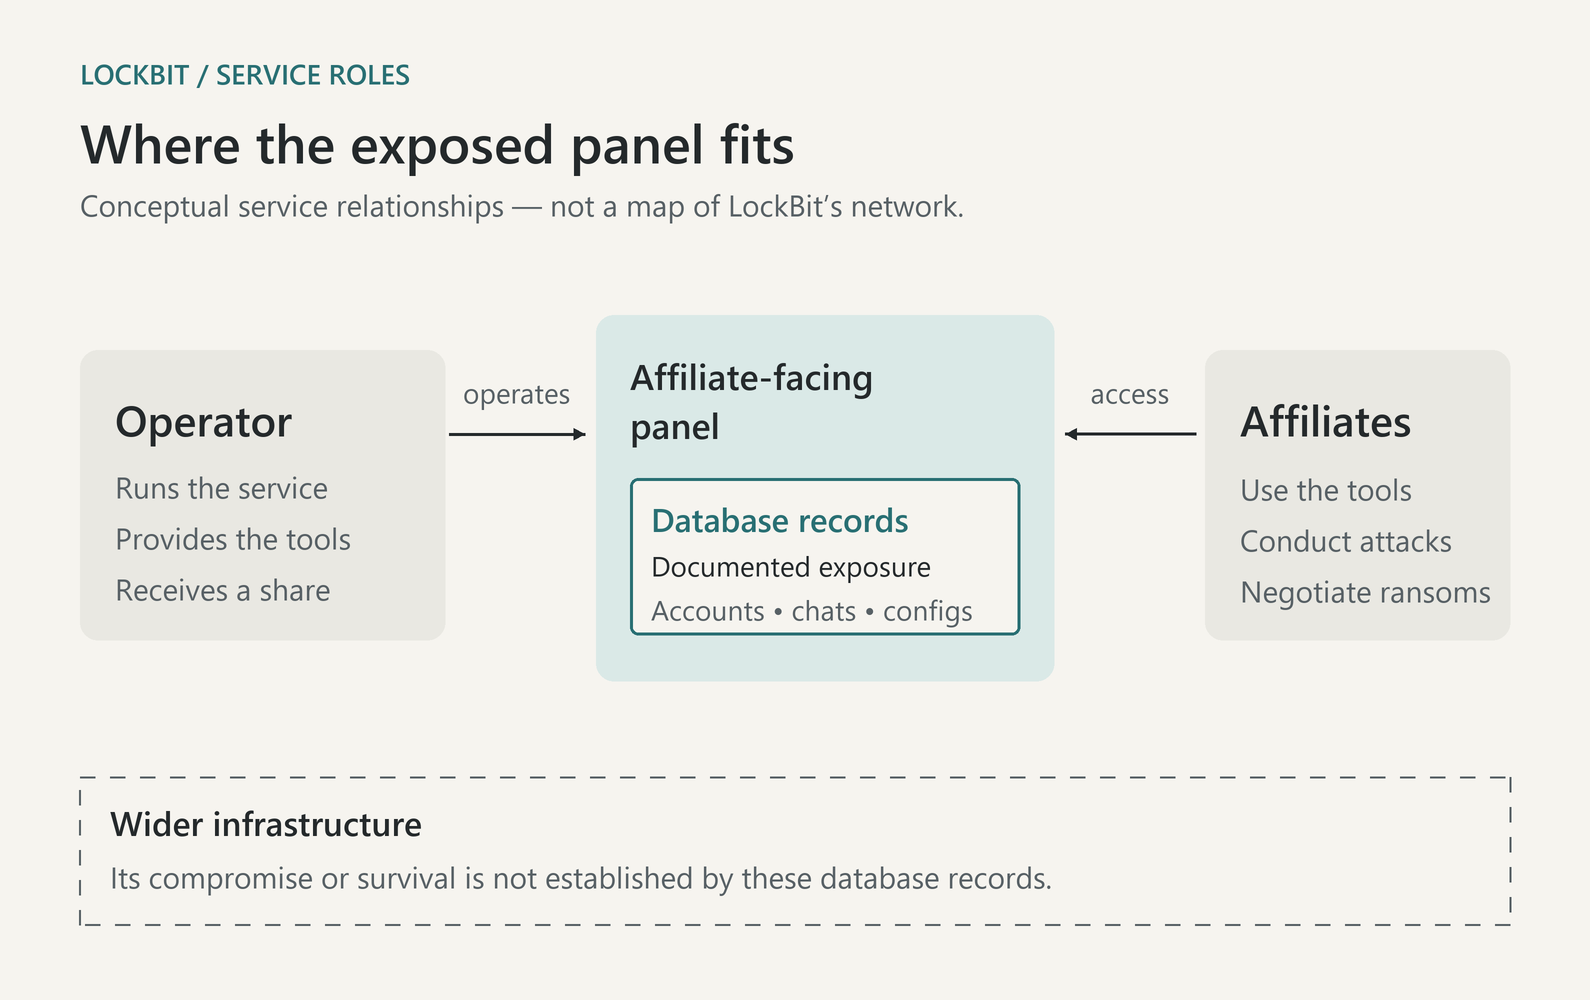
The exposed records included affiliate usernames, plaintext panel passwords, ransomware build configurations, negotiation messages and cryptocurrency addresses. These are different kinds of intelligence. Configuration records describe how the platform prepared attacks; they are not the same as released malware executables or source code.
This ransomware affiliate leak challenged a core rule of the underground economy: protect operational secrecy. Affiliates rely on anonymity to avoid arrest, extortion, or rival attacks. Exposed account and negotiation records could help investigators connect activity across cases. That risk is serious without assuming that every person who ever used LockBit’s platform appeared in the database.
Unlike the usual ransomware disclosure, this one turned the spotlight on the attackers themselves. The syndicate’s inner workings were dragged into the open. Yet negotiations also concerned victims, so this was not an exposure affecting only criminals. Treating those records as intelligence does not remove their sensitivity for the organizations already attacked.
LockBit had previously attempted to rebuild after the February 2024 crackdown under Operation Cronos, which seized infrastructure and led to charges and arrests. The renewed affiliate panel shows continued activity, not proof of hardened systems or stricter screening. Trellix described an auto-registration option, illustrating why a claim of tighter recruitment controls would need separate evidence.
After the May leak, LockBit’s operator claimed that the affected system was its Lite panel and that the full panel and leak site remained operational. That was a self-interested account, not independent proof of recovery. It nevertheless makes a claim that the attacker dismantled the entire operation too strong. The documented result was a database exposure and public embarrassment.
Events like this can do more than disrupt operations. They can corrode trust and weaken the affiliate model that ransomware-as-a-service depends on to function. Whether that risk translates into departures or closure requires evidence beyond the fact of a leak.
The next section unpacks what was inside the leak and why those records mattered to researchers and to the people whose activity they exposed.
What Was Leaked and Why It Mattered
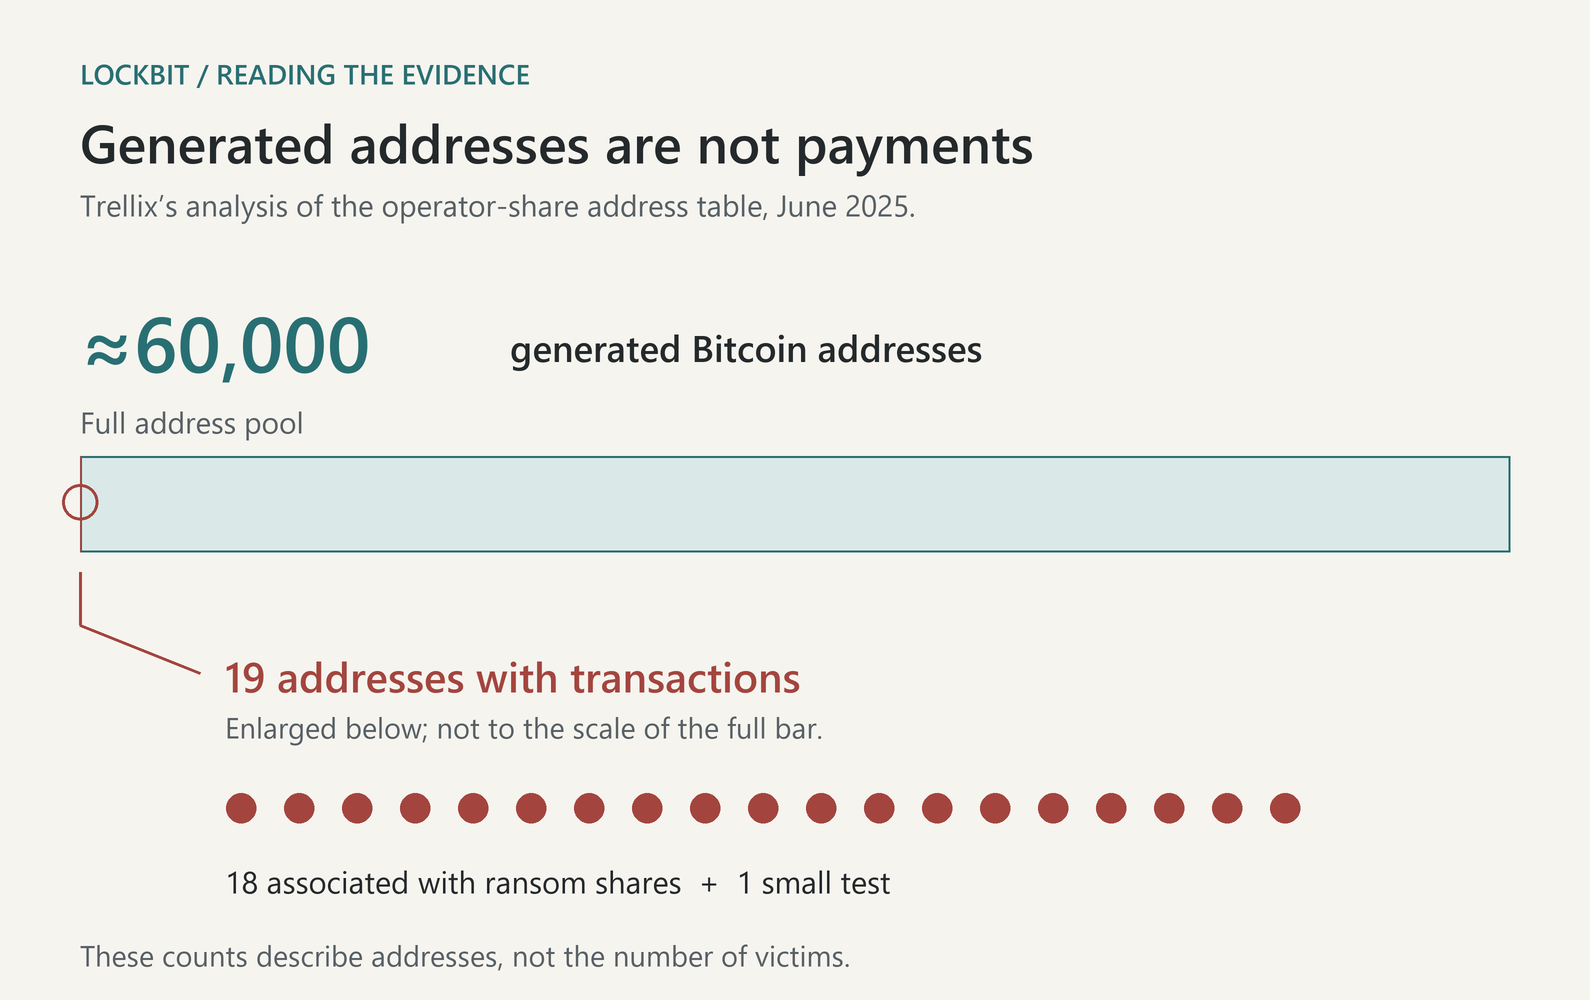
The LockBit breach didn’t just expose infrastructure. It laid bare the people, processes, and secrets that powered one of the most prolific cybercrime operations in the world. The files leaked on May 7, 2025, provided a rare window into the inner workings of a ransomware syndicate that had relied on fear, speed, and secrecy to stay ahead.
The archive, paneldb_dump.zip, contained a SQL database rather than a verified collection of every LockBit secret. Arete’s May 2025 analysis and Trellix’s later examination identified:
- Nearly 60,000 Bitcoin addresses generated for affiliates to remit the operator’s share, not evidence of 60,000 paid ransoms
- 4,442 negotiation messages, dated December 19, 2024 through April 29, 2025, rather than that many separate negotiations
- 75 panel user accounts, including usernames and passwords stored in plaintext
- Build and configuration records showing how affiliates prepared ransomware for particular targets
- Affiliate access information and records linking panel activity to negotiation and payment processes
For defenders, this was a valuable view of criminal operations. For LockBit, it was a loss of secrecy. The size of a table should not be confused with the number of successful attacks or payments: Trellix found transaction activity on only 19 of the nearly 60,000 operator-share Bitcoin addresses, including one small test transaction.
The Scale and Consequences
The public release differed from an announced seizure under legal process. It exposed account identifiers and operational records to anyone who obtained the database. Those details could create investigative and competitive risks for affiliates. But a username is not automatically a verified real-world identity, and a leaked database should not be described as proof that every part of the operation was exposed.
The plaintext passwords were a concrete sign of poor credential handling. They should not have been stored in a form that made them immediately readable after a database disclosure. That is enough to challenge the group’s professional image. It does not establish that administrators reused the same passwords across services, or that such reuse caused this intrusion.
Negotiation Logs and the Limits of Criminal Promises
The extortion messages offered a detailed look into how LockBit affiliates negotiated. Trellix’s analysis described:
- Initial demands that varied substantially between affiliates and targets
- Substantial discounts offered during negotiations
- Different outcomes across affiliates, including negotiations that did not produce a confirmed payment
These records show bargaining, not a dependable service contract. A willingness to lower a demand does not make an extortionist’s assurances trustworthy. The analysis does not establish that companies in this dataset paid for deletion and were then extorted again. Difficult negotiations and changing demands must be distinguished from a documented second demand after a completed agreement.
Affiliate Records and Operational Exposure
The database also held information about the people using the platform and the work associated with their accounts. Researchers could examine:
- Panel user records and affiliate classifications
- Build configurations associated with intended targets
- Negotiation and access records that might help connect activity across cases
Such records are useful for understanding how a service organizes affiliates and victims. They may also provide leads connecting accounts, targets and negotiations. Those connections require care: an account entry is a starting point for investigation, not automatically a verified identity. For the service, the reputational problem is straightforward: information affiliates might expect to remain private became available outside it.
The Risk to Affiliate Trust
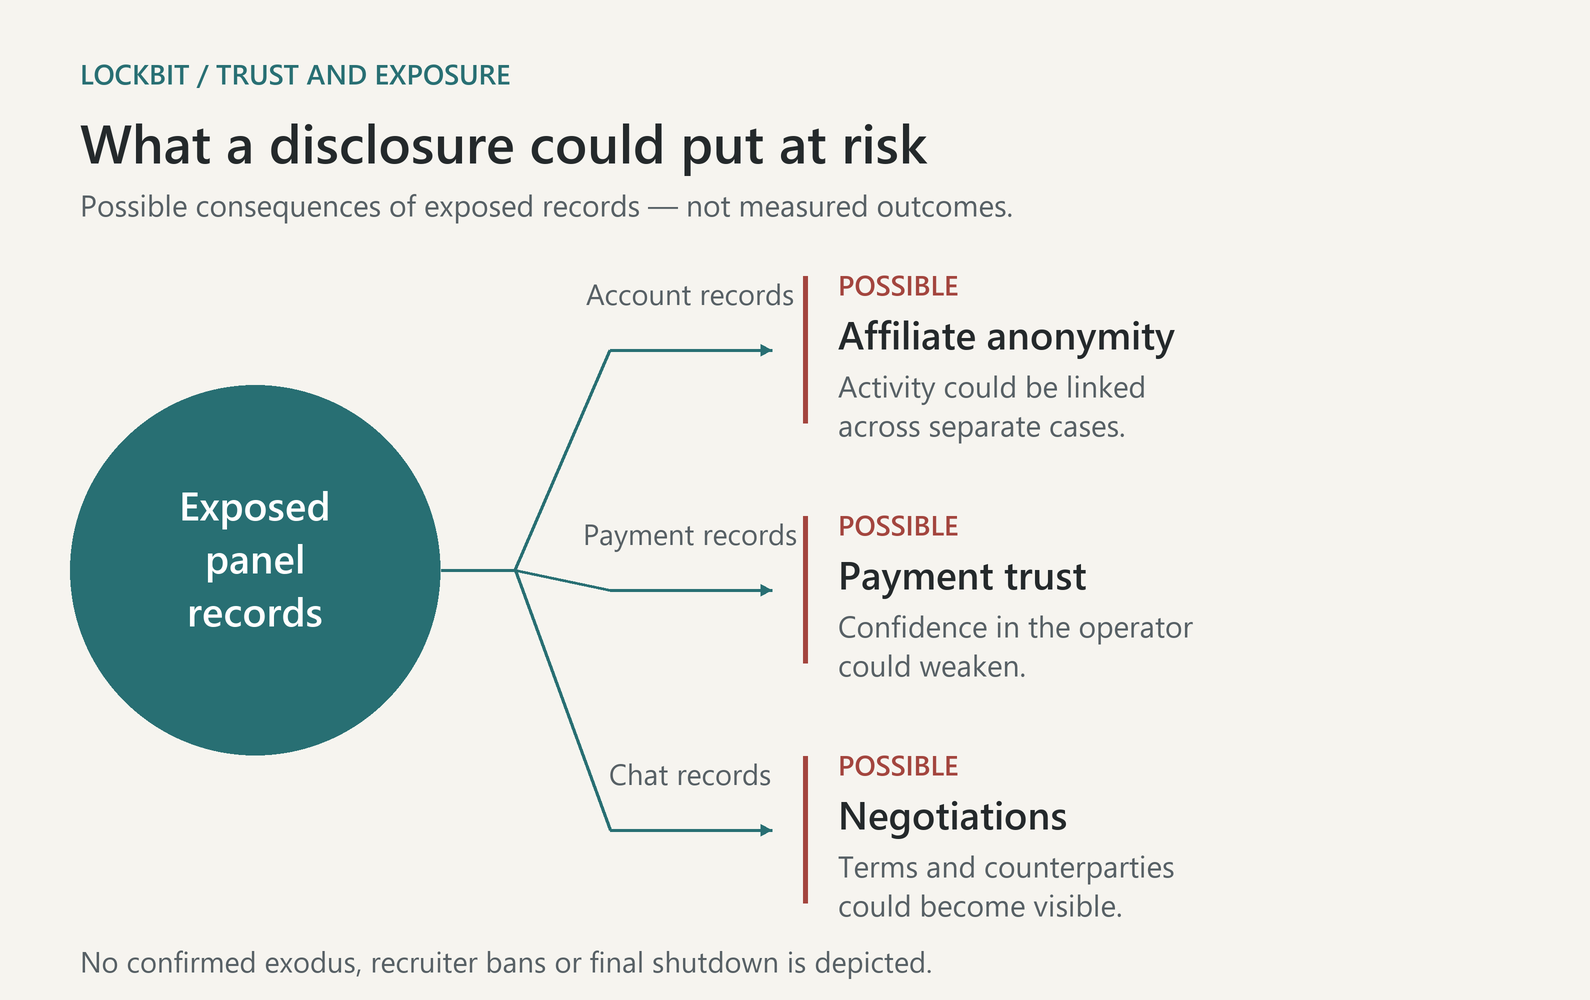
For an affiliate, a leaked panel raises practical questions. Can an account be linked to other activity? Are negotiation records exposing the targets and terms of an attack? Can the operator protect the next set of records? Those questions could discourage participation, even if the malware and some infrastructure remained available.
Public discussion after the leak included LockBit’s attempts to minimize its significance. But forum mockery does not measure how many affiliates abandoned the service, and the exposed database does not establish a final collapse. Damage to recruitment is a plausible consequence of such a disclosure; proving its scale would require evidence of departures and subsequent activity.
Damage to the LockBit Image
LockBit had branded itself as sleek, stable, and elite. Its “2.0” and “3.0” versions were marketed like software upgrades. It issued press statements, maintained leak portals, and claimed to follow a twisted internal code.
The breach challenged that image. Plaintext passwords and exposed operational records are difficult to reconcile with a claim of secure, professional administration. For affiliates deciding whether to use the service, its ability to protect their activity matters alongside the malware’s technical features. Losing control of those records was a serious failure even without proof of permanent closure.
For defenders, this leak was an intelligence opportunity. For cybercriminals, it was a warning about the cost of lost secrecy. Trust can be damaged while an operation continues, and those are different outcomes.
For a separate example of criminals exploiting trust and concealed identity, read North Korean Deepfake Job Scam: 7 Shocking Red Flags. That article concerns deceptive recruiting rather than the cause of the LockBit leak.
Next, we explore possible explanations for the breach, while keeping the attacker’s identity and motive unresolved.
Theories About Who Did It
The breach that exposed LockBit’s inner workings has triggered speculation about who was responsible. The technical depth of the intrusion does not identify the attacker, and the absence of a public law enforcement announcement does not exclude government involvement. A rival gang, a disgruntled insider, or a vigilante are possible explanations, not established findings.
Each theory carries different implications. These possibilities affect how hacked ransomware gangs assess their own risks and how trust fractures in underground ecosystems.
A Rival Gang Seeking to Discredit
One possibility is a competing ransomware group. In a market where reputation drives affiliate recruitment, discrediting LockBit could clear the way for smaller operations to rise.
The public defacement mocked LockBit, and releasing its database could damage its credibility with affiliates. That would suit a rival seeking to undermine recruitment. But the message and absence of a public ransom demand do not establish the attacker’s identity or full motives.
There is precedent for damaging disclosures. In 2022, Conti’s internal chats were leaked after it supported Russia during the invasion of Ukraine. Trellix’s Summer 2022 threat report described that disclosure and noted that attacks continued. Exposure does not automatically end a ransomware operation.
A Disgruntled Insider or Affiliate
Another possibility is that the attacker was a LockBit insider. A dispute over payments or treatment could provide a motive for retaliation, while a trusted participant might already know the service’s systems.
The exposed account information described by Arete does not explain how the intruder entered the panel. Finding plaintext passwords after a breach is different from showing that a stolen or reused password enabled it.
The public release does not strengthen this theory over the others. An outsider could also publish stolen records; publication does not establish a previous relationship with LockBit.
A Vigilante or Hacktivist
A vigilante or hacktivist is another possible explanation. The anti-crime message could express opposition to ransomware operators or simply be a taunt chosen for publicity. The wording does not identify its author.
The sources describing the leak do not establish who controlled the intrusion or what resources they used. Technical access to a database does not identify a political motive or rule out official involvement.
If this theory were correct, it would illustrate the risk of independent actors penetrating and exposing criminal infrastructure. That remains a possible explanation, not a finding about this breach.
Whatever the source, exposing private operational records creates a risk to secrecy and trust. The next section compares the May leak with the publicly announced Operation Cronos action, while keeping the unresolved identity of the May attacker separate from what investigators had already disclosed in 2024.
Comparing the Leak With Operation Cronos
LockBit long symbolized how ransomware gangs survive pressure. It attempted to rebuild after infrastructure seizures, arrests, and takedowns. The 2025 LockBit ransomware hack exposed another part of the operation. Its anonymous public disclosure differed from the announced enforcement action, but both incidents could affect infrastructure, identity, and trust.
Why the 2025 Leak Was Different
The February 2024 Operation Cronos action involved announced infrastructure seizures, charges, arrests, and decryption assistance. The May 2025 incident became public through a defacement and database release by an unidentified actor. The records included account information, negotiation messages, and ransomware build configurations, rather than a collection of compiled ransomware payloads.
Law enforcement aims to disable infrastructure and prosecute suspects; seized records can also expose how a criminal service treats victims and affiliates. In May, the mocking message made public embarrassment visible, but did not establish the attacker’s full purpose or its effect on recruitment.
An announced operation identifies participating authorities and their actions. A taunt and an anonymously released archive do not offer the same basis for attribution. Both can undermine the assumption that criminal infrastructure keeps participants’ activity secret.
Law Enforcement’s Role After the Fact
Whatever the attacker’s identity, law enforcement could benefit. Account details, cryptocurrency addresses, build configurations, and negotiation messages may help investigators test connections between cases. Those connections need corroboration; an account name alone does not establish who used it or prove a criminal charge.
Operation Cronos had already challenged LockBit’s credibility. The NCA’s May 2024 assessment described reduced active affiliate numbers, inflated victim claims, and failures of some decryptors supplied to paying victims. That is an earlier enforcement-related finding, not evidence that the May 2025 leak caused those changes. Technical disruption and reputational exposure can work together.
As threat actors shift tactics, defenders must understand how credibility itself becomes a target. The next section explores how narrative control has become a critical front in cybercrime.
For another example of trust-based manipulation, read AI-Generated Disinformation: 5 Alarming Deepfake Threats Unveiled.
Reputation Warfare and the New Cybercrime Battlefield
The LockBit ransomware hack exposed credentials and operational records, raising a reputational problem. A ransomware service needs affiliates to trust its infrastructure and payment arrangements. An embarrassing disclosure can challenge those assurances. Its effect on the business, however, cannot be ranked above decryption or enforcement from this incident alone.
Leaks as Strategic Weapons
The defacement added public embarrassment to the database disclosure. Affiliates would have reason to consider what the records reveal about their activity and whether the service could protect it. Those concerns are plausible, but the evidence does not measure departures, panic, or stalled recruitment caused by the leak.
The LockBit affiliate leak is therefore both a breach and an intelligence opportunity. It makes the relationship between operational secrecy and credibility visible, even though it does not demonstrate that the criminal service ended.
What Earlier Leaks Can Tell Us
LockBit is not the first ransomware operation whose internal records have become public. The Conti disclosure shows their value for understanding an operation’s relationships. It also illustrates a limit: exposure can occur while attacks continue, and each group’s subsequent changes need their own evidence.
Ransomware gangs can face more than arrests. Disputes, sabotage, and anonymous disclosures may expose relationships they would rather conceal. That makes internal trust relevant without identifying a rival or insider as the May attacker.
Reputation Is the Payload
Affiliates may question who can access their records and how those records are protected. Tighter access controls or separation between users would be possible responses. The May leak does not establish that forums changed their rules or affiliates abandoned LockBit.
Credibility also matters when assessing a leak. A rival could exaggerate exposure, and an operator could minimise it. Researchers must distinguish the records from either side’s publicity: neither a boast nor a taunt establishes the lasting effect of a compromise.
Cybercrime groups are no longer just defending code. They are defending brands.
The next section considers what this exposure could mean for ransomware economics and how defenders can use the records without confusing a reputational risk with a measured outcome.
What This Means for the Future of Ransomware
The LockBit ransomware hack raises questions about how ransomware groups respond when their own records become public. The LockBit data breach gives defenders a rare window into the operation’s inner workings. It also offers a basis for examining the risks of the ransomware-as-a-service model, while leaving its longer-term consequences unresolved.
The ransomware affiliate leak exposed information that the service had reason to protect. For other groups, it illustrates a risk: operational trust and internal controls matter alongside the malware itself.
Operational Security Lessons
The most immediate lesson from the LockBit ransomware hack is the risk of exposing internal records. Plaintext passwords create an obvious security concern, but do not show whether they were reused across services, whether accounts were shared, or how the attacker gained access.
Backend security matters even when the main product is malware. Protecting credentials and limiting access are sensible controls, but they do not reconstruct this intrusion. The sources do not establish stolen passwords as the entry point or show what tools the attack required.
Ransomware groups exposed in this way may restrict access or segment infrastructure. Whether an affiliate stays would also depend on access to victims, expected payments, and alternatives. The May leak does not measure that decision or demonstrate these possible responses.
Fragmentation of RaaS Ecosystems
The exposure raises the question of whether participants would stay with LockBit or use another service. The database can help analysts examine relationships, but it is not a record of departures caused by the leak. Deleted recruitment threads and silent channels are not established consequences in the cited evidence.
One possible response would be smaller, more isolated teams. Participants could rotate infrastructure, reduce public branding, or limit what they share. Greater separation could make relationships harder to study, but this incident does not demonstrate that shift or predict fewer attacks.
A service benefits from coordination while participants have reasons to conceal their activity. A leak exposes that tension. Using a criminal service does not guarantee anonymity, and separating teams does not remove all evidence of their work.
Opportunities for Researchers and Law Enforcement
Whatever its source, the LockBit breach produced records potentially useful to investigators and researchers, including:
- Individual messages about ransom pricing and negotiations
- Timestamped account and affiliate activity records
- Cryptocurrency addresses and records relevant to payment analysis
- Ransomware build configurations for Windows, Linux, and VMware ESXi systems
This information can help analysts investigate connections between accounts, attacks, and campaigns. Findings need context: configuration entries may include tests, and a generated address does not necessarily show a completed payment.
For defenders, the breach is an opportunity to refine threat models, examine affiliate activity, and identify records relevant to their own incidents. It complements evidence from affected networks.
For more on how these shifts connect to global threat dynamics and AI-driven tactics, see AI Cybersecurity Arms Race: 7 Alarming Signs Hackers Are Winning. That post explores how asymmetric attacks are becoming common in both criminal and state-sponsored operations.
The LockBit data breach illustrates why technical capability alone does not guarantee that an operation’s records will remain secret. Human relationships, access to information, and trust in a service are also relevant to understanding how ransomware businesses operate.
Conclusion & Future Outlook
The LockBit ransomware hack exposed private credentials, messages, and build configurations from a well-known ransomware service. The disclosure created risks for its users and made its internal workings available for scrutiny. Those findings matter without proving that the leak ended LockBit or destabilised the entire ransomware-as-a-service model.
The attacker was not publicly identified in the sources available for this article. The May database release differed from the announced Operation Cronos action, but that does not establish its author. Exposure can pressure the trust affiliates place in payment arrangements, protection, and discretion; lasting damage needs evidence beyond the disclosure itself.
For defenders, the breach offers a valuable intelligence opportunity. The leaked data provides insight into ransomware economics, affiliate activity, and negotiation tactics. Used with appropriate context and corroboration, it can inform threat models, investigations, and policy discussion.
For policymakers, exposing internal records may complement technical disruption and criminal investigation. This incident does not show that reputational sabotage is more effective than seizures, decryption assistance, or prosecution. Assessing those approaches requires evidence about outcomes.
As ransomware evolves, the battlefield is shifting. It is no longer just about encryption keys. It is about loyalty, credibility, and who controls the narrative.
AI is rewriting the rules of cyber conflict. Our briefings cover what regulators miss, from Volt Typhoon to digital ID rollbacks. Stay ahead of policy, strategy, and global risks by joining the Quantum Cyber AI Brief.
FAQ
Q1: Was the LockBit ransomware hack carried out by the FBI or Europol?
The attacker was not publicly identified. The May leak should not be presented as a confirmed FBI or Europol operation, but government involvement was not ruled out. It was separate from the announced February 2024 Operation Cronos action.
Q2: What kind of data was leaked in the LockBit data breach?
The database included thousands of cryptocurrency addresses, more than 4,000 individual negotiation messages, account records including plaintext passwords, and ransomware build configurations. A message count is not a count of separate negotiations, and configurations are not compiled ransomware payloads.
Q3: Why was the LockBit ransomware hack significant?
It exposed private operational records relevant to studying affiliates, negotiations, payment arrangements, and trust in the service. That value does not establish that the incident caused LockBit’s collapse or came from an insider.
Q4: Can defenders and researchers use the leaked data?
Yes, with corroboration. The records can inform analysis of negotiations, payments, affiliate accounts, and build configurations. An account name is not a verified identity, a configuration may be a test, and an address may have no payment history.
Q5: What could ransomware groups do after an exposure?
They could tighten access, separate infrastructure, or reconsider affiliate relationships. Those are possible responses, not developments established by the May leak. A disclosure alone does not show whether participants left or a service closed.