The scale and speed of cyber incidents demand a clear recovery plan. AI hacking recovery involves the same fundamentals as other incident response: establish what happened, contain further harm, preserve evidence and restore operations safely. AI can help criminals impersonate trusted people or produce convincing messages, but its suspected involvement does not tell you which systems were compromised or what response is needed.
The 2024 fraud figures and 2025 breach research illustrate the scale of the problem. In 2024, consumers reported more than $12.5 billion in fraud losses to the FTC. Among people who reported fraud, the proportion reporting a financial loss rose from 27% in 2023 to 38% in 2024. These are fraud figures overall, not a measurement of losses caused by AI. Similarly, Verizon's 2025 Data Breach Investigations Report found ransomware in 44% of the breaches it reviewed, up from 32% in the previous report. Neither finding establishes that AI caused those incidents.
This article is for professionals and policymakers who need a structured view of organizational response. It covers the threat picture, immediate actions, account and device security, financial and identity protections, professional response, and prevention. A fraudulent payment, a stolen account and an encrypted network require different action even if all three begin with convincing deception. Start with the evidence of harm rather than treating “AI” as a diagnosis.
Key Takeaways
- Recovery begins with the incident you can establish, not an assumption about AI. Contain affected systems or accounts while preserving the information responders need.
- Identity controls, prioritized patching and evidence preservation belong in the same response plan. A password reset alone does not demonstrate that an attacker has lost access.
- Financial controls matter alongside technical recovery. Verify payment changes independently and contact the financial institution immediately after a fraudulent transfer.
- Restore services deliberately, with named owners and documented decisions. Reporting a crime or recovering a backup does not guarantee that money or data will be recovered.
- Convert lessons into tested controls for employees, helpdesks, suppliers and privileged access. Training should support reliable authorization procedures rather than ask staff to detect every fake.
1. Understanding AI Hacking and Why It Matters
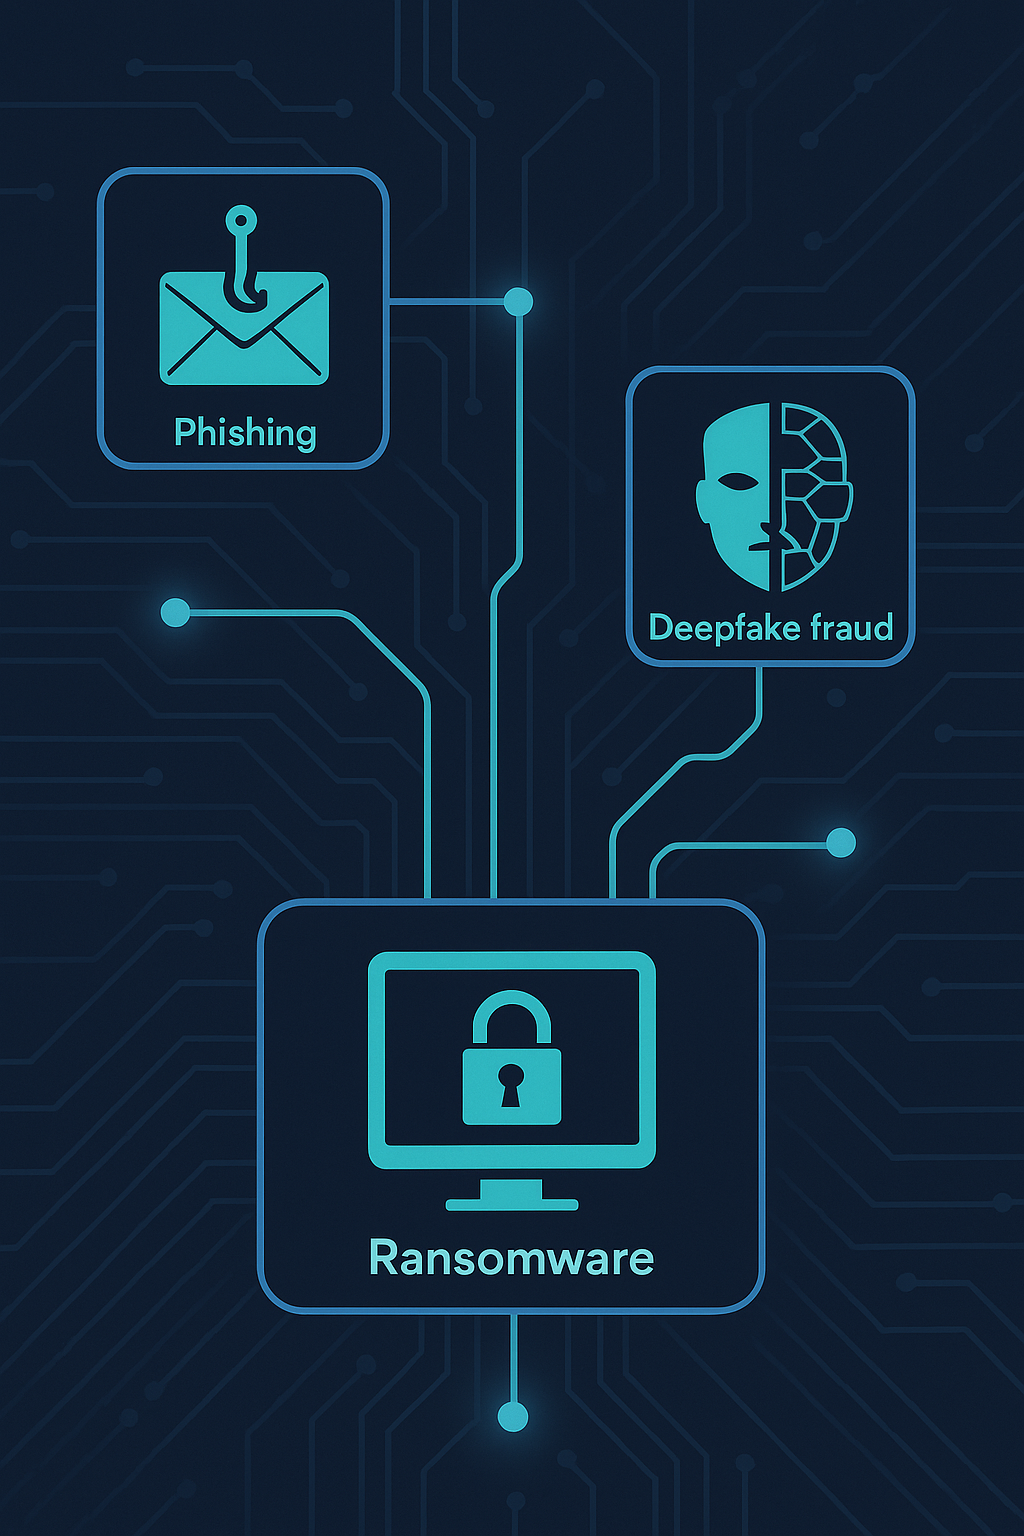
Stolen data fuels a crime-as-a-service ecosystem in which access and personal information can be traded and reused across regions. Europol's 2025 assessment of the stolen-data economy described credentials and datasets being sold, resold and repackaged, alongside growing use of generative AI in social engineering. This matters to recovery because stopping one transaction or removing one account does not necessarily resolve the exposure of information already copied.
AI can support deception that looks or sounds human. Microsoft's April 2025 Cyber Signals report describes criminals using generated content, voice cloning and fake websites to make fraud more convincing and cheaper to produce. It also distinguishes incidents in which Microsoft did not observe AI use. That distinction is important: convincing social engineering is not, by itself, evidence of an AI-enabled attack.
For agencies and enterprises, the operational question is what an attacker obtained or induced someone to do. Did a worker disclose credentials? Did an administrator register an unfamiliar authentication device? Did finance authorize a transfer to a substituted account? Those questions lead to specific containment decisions. Speculation about the tool used to write a message should not delay them.
Our earlier discussion of how cybercriminals were weaponizing AI in 2025 provides the broader threat context. Here, the emphasis is response: verify identity through an independent channel, record exceptions and establish who can authorize consequential changes during an incident.
The threat picture is only useful if it translates into action. A recovery plan should connect observed behavior to an owner and a decision. Security staff need authority to contain compromised access; finance needs a way to stop or question payments; executives need validated information about operations and exposure. These responsibilities should be coordinated rather than left to separate teams making conflicting assumptions.
2. Immediate Steps to Take After a Breach
Speed matters, but the goal is to contain harm without destroying evidence. Activate the organization's incident response process and identify the affected accounts, systems or transactions. The FTC's business breach response guide recommends assembling a response team, securing operations, fixing vulnerabilities and determining notification responsibilities. The exact response depends on the incident; an indiscriminate shutdown or reset of every service is not a universal first step.
For confirmed account compromise, restrict the affected access, reset compromised credentials from a trusted device and review active sessions and authentication methods. For an individual email or social account, the FTC's account recovery guidance explains using the provider's recovery process, signing out other sessions and checking for changes made by the intruder. In an organization, coordinate these changes with the identity and incident response teams so an affected employee is not trying to remediate a managed environment alone.
Document everything. Designate a single incident log to timestamp actions, commands and changes. Use ticket numbers to connect decisions to people and systems. Preserve relevant messages, transaction records and available logs. Qualified responders should decide how to collect volatile evidence such as running processes and network connections before reimaging; do not ask employees to experiment on a suspected compromised device. Record urgent containment actions even when they must happen before a complete evidence collection.
Communicate with precision. Switch to a known, independent channel for critical coordination if the normal communication system may be compromised. Provide validated facts to executives and external stakeholders, distinguishing what is confirmed from what remains under investigation. If ransomware is suspected, the response team should isolate affected systems and assess spread. Continuing to use the same affected account for confidential response discussions can undermine the response itself.
Financial loss requires parallel action, not a place at the end of the technical checklist. The FBI's business email compromise guidance says to contact the financial institution immediately after discovering a fraudulent transfer, request a recall and file an IC3 complaint promptly, regardless of the amount. A report may support efforts to freeze funds; it does not automatically trigger a successful recall or guarantee reimbursement. Retain the payment details and the institution's case reference.
With the first hours contained and documented, the next priority is hardening the accounts and devices the attacker may try to reuse. Keep immediate containment distinct from the decision to return a system to normal service.
3. Securing Your Accounts and Devices
After initial containment, recovery shifts to the technical entry points that attackers may try to reuse. Accounts and endpoints need attention together. Changing a password does not remediate a compromised computer, and patching one device does not revoke access an intruder established elsewhere. The response team should document what has been corrected and what is still being investigated before treating an account or service as restored.
Multifactor Authentication as a Baseline
Multifactor authentication (MFA) should cover critical user accounts, administrator dashboards, cloud services and remote access systems. CISA's guidance on stronger MFA recommends phishing-resistant authentication and discusses number matching as an improvement for organizations still using push-based methods. The methods are not equivalent, and an unsolicited approval prompt should never be accepted simply to make it stop.
After compromise, check how a user regains access as well as how they normally sign in. Helpdesk identity checks and approval of new authentication devices deserve the same attention as the normal login. An organization can strengthen authentication while leaving its reset process vulnerable. Document exceptions and make sure the appropriate administrator reviews changes before access is restored.
Strong Password Hygiene
Use long, unique passwords and a password manager to reduce reuse. Replace a password when there is evidence it has been compromised. Routine calendar-based changes and mandatory mixtures of character types should not be treated as universal requirements. NIST's digital authentication guidance rejects those requirements for the password verifiers it covers and calls for screening new passwords against commonly used, expected or compromised values. Password policy should follow the applicable standard and the organization's risk, rather than assume more frequent changes mean better security.
Our guide to passwords, passkeys and two-factor authentication explains the methods in plain language. For organizational recovery, the important distinction is between replacing a compromised secret and verifying the rest of the account's access and recovery configuration. Document both rather than treating the password change as the closing action.
Patch and Remediate Quickly
Software vulnerabilities remain important entry points. In Verizon's 2025 report, vulnerability exploitation accounted for 20% of initial access in the relevant breach dataset. Its analysis of edge-device vulnerabilities found about 54% fully remediated during the year, with a median of 32 days to remediate. Those were observations from the report, not acceptable deadlines or universal measures of every organization's patching performance.
Prioritize remediation by exposure and exploitation risk rather than relying only on a quarterly cycle. Track the affected product, the required vendor fix, the system owner and whether the change was actually applied. If a device was compromised, installing a patch does not by itself establish that the intruder's changes have been removed. The incident response team should decide whether repair, rebuilding or replacement is appropriate before reconnecting it.
4. Protecting Financial and Personal Data
Recovery does not stop at technical remediation. Financial and identity exposure need their own assessment because restoring access does not reverse a payment or retrieve copied information. Determine which organizational funds, employee records, customer information or personal identifiers were involved. Keep confirmed exposure separate from an assumption that every kind of information was taken.
Business Email Compromise Losses
Business email compromise (BEC) remains a major financial risk. The FBI IC3's 2024 annual report recorded approximately $2.77 billion in reported BEC losses for that year. This category is not a count of AI-enabled fraud. It does, however, explain why email verification and wire-transfer controls belong in the response plan alongside technical remediation.
For finance teams, layered authorization is more useful than asking staff to judge whether a message sounds like the executive who appears to have sent it. Verify changes to payment instructions through a previously established contact route. Record who approved the transaction and which independent check was made. If the contact record itself may have been changed, verify that record before relying on it. Escalation should allow a worker to pause a consequential payment without having to prove that the apparent executive is an impostor.
Consumer Safeguards
When an organizational incident exposes individuals' information, the response should explain which personal actions fit that exposure. The FTC's explanation of credit freezes and fraud alerts distinguishes the two: a freeze restricts access to a credit report and helps prevent new credit accounts, while a fraud alert asks businesses to verify identity before granting credit. A freeze must be placed with each of the three nationwide credit bureaus; an initial fraud alert can be requested through one, which informs the others.
Neither measure secures an existing bank account or reverses a fraudulent transfer. If identity theft has occurred, the FTC's identity theft reporting and recovery resource directs people to a personalized plan and sample letters. Avoid telling every affected employee or customer to complete the same checklist without regard to what was exposed. Explain what is known, what remains uncertain and where to obtain the relevant help.
Case Study: Arup Deepfake Scam
Early in 2024, an employee at Arup was deceived into transferring about $25 million following a video call involving deepfake impersonations. In a February 2025 interview with Arup's CIO, the World Economic Forum described the incident and the company's response. The CIO said the company's systems were not compromised and no data was affected.
This was a case of technology-enhanced social engineering, not evidence that AI had broken into Arup's network. Its lesson for recovery planning is to assess the actual event: unauthorized money movement may require urgent finance and law-enforcement action even when technical investigation finds no systems intrusion. Independent verification and layered financial controls matter because an apparently familiar face or voice is not sufficient authorization.
5. Working with Professionals for Recovery
Complex incidents often exceed the capacity of internal teams. Engage specialized responders when the scope, evidence collection or restoration work requires skills the organization does not have. Treat this as an extension of the response rather than a complete handoff. Align legal, compliance, security operations and communications so that decisions remain defensible and well documented. Establish who can authorize containment, business interruption and restoration, and keep those decisions in the incident record.
The joint FBI, CISA and Australian advisory on Play ransomware describes account abuse, exploitation of public-facing applications and misuse of remote access. It recommends measures including MFA, vulnerability remediation, segmentation and offline backups. These are useful reference points when the observed incident matches them. An advisory about a named ransomware group is not proof that the same group, or AI, was involved in your incident.
Responders should also investigate the routes an intruder used to retain access. The joint Scattered Spider advisory updated in July 2025 describes social engineering of employees and helpdesks, manipulation of MFA registration and use of legitimate remote-access tools. It also warns that attackers may monitor incident-response communications. These observations support strict verification for sensitive access changes and the use of independent response channels. They do not establish that every helpdesk impersonation uses AI.
Financial loss and wire fraud remain a parallel track. Keep the bank, investigators and the organization's finance lead supplied with accurate transaction details and any requested supporting records. Retain complaint and case references. Do not describe a police or IC3 report as a guarantee of recovery, proof of insurance coverage or satisfaction of every regulatory obligation. Counsel and the appropriate specialists should determine the notification and contractual requirements that apply to the actual incident.
During triage, keep evidence preservation and change control strict. Maintain a single incident log that timestamps actions, tools and affected systems. Align communications with facts validated by responders. The report should distinguish what investigators observed, what they reasonably inferred and what they could not determine. This discipline reduces conflicting instructions and makes it possible to explain why a service was restored while another remained restricted.
Once responders stabilize systems and assess financial exposure, turn the findings into durable defenses. Assign an owner to each material correction and record what evidence will demonstrate completion. An incident should not be closed solely because the most visible disruption has stopped.
6. Preventing Future Attacks
Recovery is not complete until lessons become preventive controls. The goal is to reduce the chance that the same weakness will be exploited again. That requires attention to business processes as well as technical access: payment approvals, supplier relationships and helpdesk recovery procedures can all matter alongside endpoint security.
Building a Zero-Trust Security Model
NIST's zero-trust architecture guidance rejects implicit trust based solely on network location or asset ownership. Authentication and authorization of the user and device are separate decisions made before access to an enterprise resource is established. This is more specific than the slogan that every request must be verified, and it does not mean repeatedly interrupting every employee with a login prompt.
For post-incident planning, examine which access was broader than necessary and which decisions relied on a trusted location or familiar identity alone. Use the findings to prioritize access policies and monitoring. Zero trust is an architectural approach, not a product purchase that retrospectively makes an affected environment secure.
Strengthening Organizational Resilience
The July 2025 joint Interlock ransomware advisory recommends layered protections including DNS filtering, web access firewalls, MFA and network segmentation. These controls address different routes of attack. Choose and maintain them according to the organization's systems and exposure rather than assume that adding a tool resolves the underlying incident.
Training, response exercises and protected backups support resilience when they are tied to the actual environment. Test restoration as well as backup creation, and keep recovery copies protected from the production environment. Exercises should establish who makes a decision when a usual approver or communication channel cannot be trusted. Our AI fraud and deepfakes hub provides related explanations for staff who need context about impersonation risk.
Lessons from High-Profile Cases
Caesars' September 2023 disclosure attributed suspicious network activity to social engineering of an outsourced IT support vendor and described the theft of a loyalty-program database. The company said its customer-facing operations continued without disruption. That disclosure supports a lesson about supplier access and identity checks; it does not establish AI involvement or justify treating every casino incident as the same event.
For policymakers, the useful question is how organizational accountability extends to contracted services and affected people. For organizations, the practical response is to review vendor access, escalation paths and the information needed to assess an incident. Resources alone do not replace a tested process. A convincing impersonation should still encounter limits on what one person or one supplier can authorize.
Conclusion
AI hacking recovery needs disciplined incident response, not a separate set of assumptions about every attack. Establish the scope, contain further harm, protect evidence and restore services deliberately. Treat identity, device, network and financial controls as connected responsibilities, while keeping the response proportionate to what actually happened.
The path forward is practical. Strengthen authentication and account recovery procedures, prioritize exposed vulnerabilities and independently verify sensitive changes. Document the response so findings become assigned corrections in policy, technology and training. Keep unresolved questions visible rather than imply that restored service proves every consequence has been addressed.
Subscribe to the Quantum Cyber AI Brief for explanations of cybersecurity and AI developments.
FAQ
What is the first action in AI hacking recovery if compromise is suspected?
Activate the organization's incident response process and establish what account, system or transaction is affected. Contain further harm and preserve relevant evidence. Password resets and session revocation may be appropriate for compromised accounts, but an organization-wide reset is not the universal first action for every suspected incident.
How can organizations reduce deepfake-enabled payment fraud?
Use independent verification for wire transfers and changes to payment details, with layered authorization for consequential transactions. A familiar voice or face does not substitute for those controls. After a fraudulent transfer, contact the financial institution immediately and report promptly through the appropriate law-enforcement channel; recovery is not guaranteed.
How fast should vulnerabilities be patched during a response?
Prioritize by evidence of exploitation, internet exposure and the affected system's role. Follow the vendor's remediation instructions and coordinate changes with responders. The 32-day median in Verizon's 2025 analysis described observed remediation performance; it was not a recommended waiting period. A patch also does not, by itself, remove access already established by an intruder.
Should law enforcement be involved even if losses seem small?
The FBI recommends reporting business email compromise promptly regardless of the amount lost. Retain transaction records and complaint references. For other incidents, coordinate reporting with the organization's response and legal teams. A crime report can aid an investigation but does not replace applicable notifications or guarantee recovery.